All Articles
Ordered by Date Received
: Year: "2026"
Month: "11"
Day: "07"
Hour: "09"
Page:
1 (of 0)
Total Articles in this collection: 3
Navigation Help at the bottom of the page
Article: dtls - published about 10 hours ago.
Content: Native Go implementation of DTLS 1.2 and 1.3 with ECDHE and PSK key exchange, AEAD ciphers, connection IDs, session resumption, 0-RTT, and Encrypted Client Hello....
https://kitploit.com/en/tools/github/pion/dtls
Published: 2026 11 07 08:12:02
Received: 2026 11 07 09:41:25
Feed: PenTest and Hacking Tools - powered by FeedBurner
Source: PenTest and Hacking Tools - powered by FeedBurner
Category: News
Topic: Security Tooling
Content: Native Go implementation of DTLS 1.2 and 1.3 with ECDHE and PSK key exchange, AEAD ciphers, connection IDs, session resumption, 0-RTT, and Encrypted Client Hello....
https://kitploit.com/en/tools/github/pion/dtls
Published: 2026 11 07 08:12:02
Received: 2026 11 07 09:41:25
Feed: PenTest and Hacking Tools - powered by FeedBurner
Source: PenTest and Hacking Tools - powered by FeedBurner
Category: News
Topic: Security Tooling
|
Article: dtls - published about 10 hours ago. Content: Native Go implementation of DTLS 1.2 and 1.3 with ECDHE and PSK key exchange, AEAD ciphers, connection IDs, session resumption, 0-RTT, and Encrypted Client Hello.... https://kitploit.com/en/tools/github/pion/dtls Published: 2026 11 07 08:12:02 Received: 2026 11 07 09:41:25 Feed: PenTest and Hacking Tools - powered by FeedBurner Source: PenTest and Hacking Tools - powered by FeedBurner Category: News Topic: Security Tooling |
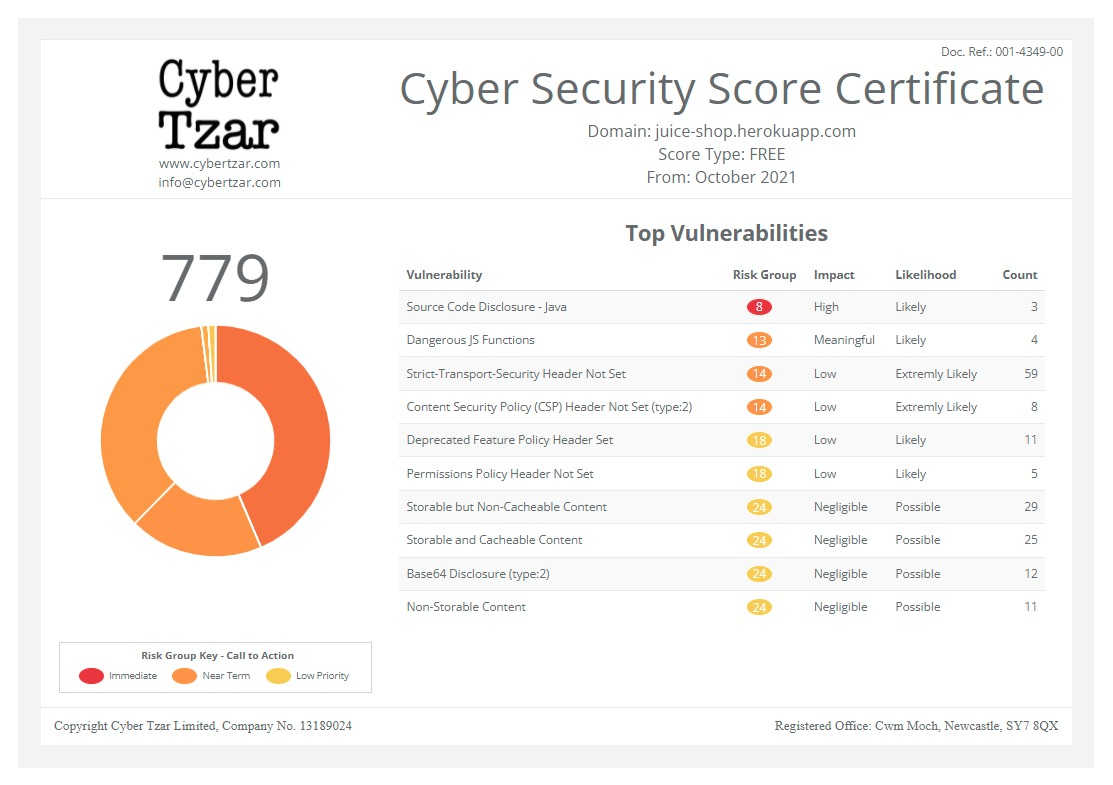
Article: Forwarded Without Question: How Web Frameworks Overtrust the Forwarded Header - published 1 day ago.
Content: Many common web frameworks like Spring and Ruby on Rails trust the RFC 7239 Forwarded header by default, even though most proxies don't actually have any support for it. This makes apps vulnerable to request hostname or client IP address spoofing in the default configurations. I've been researching how the Forwarded header is supported across frameworks and ...
https://www.reddit.com/r/netsec/comments/1xp9n79/forwarded_without_question_how_web_frameworks/
Published: 2026 11 06 10:34:37
Received: 2026 11 07 09:39:05
Feed: /r/netsec - Information Security News and Discussion
Source: /r/netsec - Information Security News and Discussion
Category: Cyber Security
Topic: Cyber Security
Content: Many common web frameworks like Spring and Ruby on Rails trust the RFC 7239 Forwarded header by default, even though most proxies don't actually have any support for it. This makes apps vulnerable to request hostname or client IP address spoofing in the default configurations. I've been researching how the Forwarded header is supported across frameworks and ...
https://www.reddit.com/r/netsec/comments/1xp9n79/forwarded_without_question_how_web_frameworks/
Published: 2026 11 06 10:34:37
Received: 2026 11 07 09:39:05
Feed: /r/netsec - Information Security News and Discussion
Source: /r/netsec - Information Security News and Discussion
Category: Cyber Security
Topic: Cyber Security
|
Article: Forwarded Without Question: How Web Frameworks Overtrust the Forwarded Header - published 1 day ago. Content: Many common web frameworks like Spring and Ruby on Rails trust the RFC 7239 Forwarded header by default, even though most proxies don't actually have any support for it. This makes apps vulnerable to request hostname or client IP address spoofing in the default configurations. I've been researching how the Forwarded header is supported across frameworks and ... https://www.reddit.com/r/netsec/comments/1xp9n79/forwarded_without_question_how_web_frameworks/ Published: 2026 11 06 10:34:37 Received: 2026 11 07 09:39:05 Feed: /r/netsec - Information Security News and Discussion Source: /r/netsec - Information Security News and Discussion Category: Cyber Security Topic: Cyber Security |
|
Article: The Exploit Was the Bottleneck - published about 9 hours ago.
Content: submitted by /u/kygyty [link] [comments]
https://www.reddit.com/r/netsec/comments/1xq2ix1/the_exploit_was_the_bottleneck/
Published: 2026 11 07 09:38:30
Received: 2026 11 07 09:39:05
Feed: /r/netsec - Information Security News and Discussion
Source: /r/netsec - Information Security News and Discussion
Category: Cyber Security
Topic: Cyber Security
Content: submitted by /u/kygyty [link] [comments]
https://www.reddit.com/r/netsec/comments/1xq2ix1/the_exploit_was_the_bottleneck/
Published: 2026 11 07 09:38:30
Received: 2026 11 07 09:39:05
Feed: /r/netsec - Information Security News and Discussion
Source: /r/netsec - Information Security News and Discussion
Category: Cyber Security
Topic: Cyber Security
|
Article: The Exploit Was the Bottleneck - published about 9 hours ago. Content: submitted by /u/kygyty [link] [comments] https://www.reddit.com/r/netsec/comments/1xq2ix1/the_exploit_was_the_bottleneck/ Published: 2026 11 07 09:38:30 Received: 2026 11 07 09:39:05 Feed: /r/netsec - Information Security News and Discussion Source: /r/netsec - Information Security News and Discussion Category: Cyber Security Topic: Cyber Security |
|
All Articles
Ordered by Date Received
: Year: "2026"
Month: "11"
Day: "07"
Hour: "09"
Page:
1 (of 0)
Total Articles in this collection: 3
- "All Articles" links back to the front page, effectivly the Planet "Home Page"; shows all articles, with no selections, or groupings.
- Default date ordering is by "Received Date" (due to not all RSS feeds having a "Published Date").
- Only Published Date selections use the articles Published Date.
- The first page always shows fifty items plus from zero to up to a remaining forty-nine items, before they are commited permently to the next page.
- All subsequent pages show fifty items.
- Pagination is in reverse ordering (so that pages are permamenent links, aka "permalinks", to their content).
- "<<" moves you to the first page (aka newest articles)
- ">>" moves you to the last page (aka oldest articles)
- "<" moves you to the previous page (aka newer articles)
- ">" moves you to the next page (aka older articles)
- Return to the top of this page Go Now
