All Articles
Ordered by Date Received
Page:
<<
<
10,553 (of 10,737)
>
>>
Total Articles in this collection: 536,867
Navigation Help at the bottom of the page
Article: APT41: A Dual Espionage and Cyber Crime Operation - published over 7 years ago.
Content: Today, FireEye Intelligence is releasing a comprehensive report detailing APT41, a prolific Chinese cyber threat group that carries out state-sponsored espionage activity in parallel with financially motivated operations. APT41 is unique among tracked China-based actors in that it leverages non-public malware typically reserved for espionage campai...
http://www.fireeye.com/blog/threat-research/2019/08/apt41-dual-espionage-and-cyber-crime-operation.html
Published: 2019 08 07 12:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Today, FireEye Intelligence is releasing a comprehensive report detailing APT41, a prolific Chinese cyber threat group that carries out state-sponsored espionage activity in parallel with financially motivated operations. APT41 is unique among tracked China-based actors in that it leverages non-public malware typically reserved for espionage campai...
http://www.fireeye.com/blog/threat-research/2019/08/apt41-dual-espionage-and-cyber-crime-operation.html
Published: 2019 08 07 12:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: APT41: A Dual Espionage and Cyber Crime Operation - published over 7 years ago. Content: Today, FireEye Intelligence is releasing a comprehensive report detailing APT41, a prolific Chinese cyber threat group that carries out state-sponsored espionage activity in parallel with financially motivated operations. APT41 is unique among tracked China-based actors in that it leverages non-public malware typically reserved for espionage campai... http://www.fireeye.com/blog/threat-research/2019/08/apt41-dual-espionage-and-cyber-crime-operation.html Published: 2019 08 07 12:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: Fuzzing Image Parsing in Windows, Part One: Color Profiles - published about 6 years ago.
Content: Image parsing and rendering are basic features of any modern operating system (OS). Image parsing is an easily accessible attack surface, and a vulnerability that may lead to remote code execution or information disclosure in such a feature is valuable to attackers. In this multi-part blog series, I am reviewing Windows OS’ built-in image parsers a...
http://www.fireeye.com/blog/threat-research/2020/09/fuzzing-image-parsing-in-windows-color-profiles.html
Published: 2020 09 24 15:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Image parsing and rendering are basic features of any modern operating system (OS). Image parsing is an easily accessible attack surface, and a vulnerability that may lead to remote code execution or information disclosure in such a feature is valuable to attackers. In this multi-part blog series, I am reviewing Windows OS’ built-in image parsers a...
http://www.fireeye.com/blog/threat-research/2020/09/fuzzing-image-parsing-in-windows-color-profiles.html
Published: 2020 09 24 15:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Fuzzing Image Parsing in Windows, Part One: Color Profiles - published about 6 years ago. Content: Image parsing and rendering are basic features of any modern operating system (OS). Image parsing is an easily accessible attack surface, and a vulnerability that may lead to remote code execution or information disclosure in such a feature is valuable to attackers. In this multi-part blog series, I am reviewing Windows OS’ built-in image parsers a... http://www.fireeye.com/blog/threat-research/2020/09/fuzzing-image-parsing-in-windows-color-profiles.html Published: 2020 09 24 15:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |

|
Article: Detecting Microsoft 365 and Azure Active Directory Backdoors - published about 6 years ago.
Content: Mandiant has seen an uptick in incidents involving Microsoft 365 (M365) and Azure Active Directory (Azure AD). Most of these incidents are the result of a phishing email coercing a user to enter their credentials used for accessing M365 into a phishing site. Other incidents have been a result of password spraying, password stuffing, or simple brute...
http://www.fireeye.com/blog/threat-research/2020/09/detecting-microsoft-365-azure-active-directory-backdoors.html
Published: 2020 09 30 16:45:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Mandiant has seen an uptick in incidents involving Microsoft 365 (M365) and Azure Active Directory (Azure AD). Most of these incidents are the result of a phishing email coercing a user to enter their credentials used for accessing M365 into a phishing site. Other incidents have been a result of password spraying, password stuffing, or simple brute...
http://www.fireeye.com/blog/threat-research/2020/09/detecting-microsoft-365-azure-active-directory-backdoors.html
Published: 2020 09 30 16:45:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Detecting Microsoft 365 and Azure Active Directory Backdoors - published about 6 years ago. Content: Mandiant has seen an uptick in incidents involving Microsoft 365 (M365) and Azure Active Directory (Azure AD). Most of these incidents are the result of a phishing email coercing a user to enter their credentials used for accessing M365 into a phishing site. Other incidents have been a result of password spraying, password stuffing, or simple brute... http://www.fireeye.com/blog/threat-research/2020/09/detecting-microsoft-365-azure-active-directory-backdoors.html Published: 2020 09 30 16:45:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: FIN11: Widespread Email Campaigns as Precursor for Ransomware and Data Theft - published about 6 years ago.
Content: Mandiant Threat Intelligence recently promoted a threat cluster to a named FIN (or financially motivated) threat group for the first time since 2017. We have detailed FIN11's various tactics, techniques and procedures in a report that is available now by signing up for Mandiant Advantage Free. In some ways, FIN11 is reminiscent of APT1; they are n...
http://www.fireeye.com/blog/threat-research/2020/10/fin11-email-campaigns-precursor-for-ransomware-data-theft.html
Published: 2020 10 14 12:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Mandiant Threat Intelligence recently promoted a threat cluster to a named FIN (or financially motivated) threat group for the first time since 2017. We have detailed FIN11's various tactics, techniques and procedures in a report that is available now by signing up for Mandiant Advantage Free. In some ways, FIN11 is reminiscent of APT1; they are n...
http://www.fireeye.com/blog/threat-research/2020/10/fin11-email-campaigns-precursor-for-ransomware-data-theft.html
Published: 2020 10 14 12:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: FIN11: Widespread Email Campaigns as Precursor for Ransomware and Data Theft - published about 6 years ago. Content: Mandiant Threat Intelligence recently promoted a threat cluster to a named FIN (or financially motivated) threat group for the first time since 2017. We have detailed FIN11's various tactics, techniques and procedures in a report that is available now by signing up for Mandiant Advantage Free. In some ways, FIN11 is reminiscent of APT1; they are n... http://www.fireeye.com/blog/threat-research/2020/10/fin11-email-campaigns-precursor-for-ransomware-data-theft.html Published: 2020 10 14 12:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: Flare-On 7 Challenge Solutions - published about 6 years ago.
Content: We are thrilled to announce the conclusion of the seventh annual Flare-On challenge. This year proved to be the most difficult challenge we’ve produced, with the lowest rate of finishers. This year’s winners are truly the elite of the elite! Lucky for them, all 260 winners will receive this cyberpunk metal key. We would like to thank the challe...
http://www.fireeye.com/blog/threat-research/2020/10/flare-on-7-challenge-solutions.html
Published: 2020 10 24 00:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: We are thrilled to announce the conclusion of the seventh annual Flare-On challenge. This year proved to be the most difficult challenge we’ve produced, with the lowest rate of finishers. This year’s winners are truly the elite of the elite! Lucky for them, all 260 winners will receive this cyberpunk metal key. We would like to thank the challe...
http://www.fireeye.com/blog/threat-research/2020/10/flare-on-7-challenge-solutions.html
Published: 2020 10 24 00:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Flare-On 7 Challenge Solutions - published about 6 years ago. Content: We are thrilled to announce the conclusion of the seventh annual Flare-On challenge. This year proved to be the most difficult challenge we’ve produced, with the lowest rate of finishers. This year’s winners are truly the elite of the elite! Lucky for them, all 260 winners will receive this cyberpunk metal key. We would like to thank the challe... http://www.fireeye.com/blog/threat-research/2020/10/flare-on-7-challenge-solutions.html Published: 2020 10 24 00:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Welcome to ThreatPursuit VM: A Threat Intelligence and Hunting Virtual Machine - published about 6 years ago.
Content: Skilled adversaries can deceive detection and often employ new measures in their tradecraft. Keeping a stringent focus on the lifecycle and evolution of adversaries allows analysts to devise new detection mechanisms and response processes. Access to the appropriate tooling and resources is critical to discover these threats within a timely and a...
http://www.fireeye.com/blog/threat-research/2020/10/threatpursuit-vm-threat-intelligence-and-hunting-virtual-machine.html
Published: 2020 10 28 15:30:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Skilled adversaries can deceive detection and often employ new measures in their tradecraft. Keeping a stringent focus on the lifecycle and evolution of adversaries allows analysts to devise new detection mechanisms and response processes. Access to the appropriate tooling and resources is critical to discover these threats within a timely and a...
http://www.fireeye.com/blog/threat-research/2020/10/threatpursuit-vm-threat-intelligence-and-hunting-virtual-machine.html
Published: 2020 10 28 15:30:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Welcome to ThreatPursuit VM: A Threat Intelligence and Hunting Virtual Machine - published about 6 years ago. Content: Skilled adversaries can deceive detection and often employ new measures in their tradecraft. Keeping a stringent focus on the lifecycle and evolution of adversaries allows analysts to devise new detection mechanisms and response processes. Access to the appropriate tooling and resources is critical to discover these threats within a timely and a... http://www.fireeye.com/blog/threat-research/2020/10/threatpursuit-vm-threat-intelligence-and-hunting-virtual-machine.html Published: 2020 10 28 15:30:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Ransomware Protection and Containment Strategies: Practical Guidance for Endpoint Protection, Hardening, and Containment - published about 7 years ago.
Content: UPDATE (Oct. 30, 2020): We have updated the report to include additional protection and containment strategies based on front-line visibility and response efforts in combating ransomware. While the full scope of recommendations included within the initial report remain unchanged, the following strategies have been added into the report: ...
http://www.fireeye.com/blog/threat-research/2019/09/ransomware-protection-and-containment-strategies.html
Published: 2019 09 05 09:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: UPDATE (Oct. 30, 2020): We have updated the report to include additional protection and containment strategies based on front-line visibility and response efforts in combating ransomware. While the full scope of recommendations included within the initial report remain unchanged, the following strategies have been added into the report: ...
http://www.fireeye.com/blog/threat-research/2019/09/ransomware-protection-and-containment-strategies.html
Published: 2019 09 05 09:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Ransomware Protection and Containment Strategies: Practical Guidance for Endpoint Protection, Hardening, and Containment - published about 7 years ago. Content: UPDATE (Oct. 30, 2020): We have updated the report to include additional protection and containment strategies based on front-line visibility and response efforts in combating ransomware. While the full scope of recommendations included within the initial report remain unchanged, the following strategies have been added into the report: ... http://www.fireeye.com/blog/threat-research/2019/09/ransomware-protection-and-containment-strategies.html Published: 2019 09 05 09:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: In Wild Critical Buffer Overflow Vulnerability in Solaris Can Allow Remote Takeover — CVE-2020-14871 - published about 6 years ago.
Content: FireEye Mandiant has been investigating compromised Oracle Solaris machines in customer environments. During our investigations, we discovered an exploit tool on a customer’s system and analyzed it to see how it was attacking their Solaris environment. The FLARE team’s Offensive Task Force analyzed the exploit to determine how it worked, reproduced...
http://www.fireeye.com/blog/threat-research/2020/11/critical-buffer-overflow-vulnerability-in-solaris-can-allow-remote-takeover.html
Published: 2020 11 04 19:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: FireEye Mandiant has been investigating compromised Oracle Solaris machines in customer environments. During our investigations, we discovered an exploit tool on a customer’s system and analyzed it to see how it was attacking their Solaris environment. The FLARE team’s Offensive Task Force analyzed the exploit to determine how it worked, reproduced...
http://www.fireeye.com/blog/threat-research/2020/11/critical-buffer-overflow-vulnerability-in-solaris-can-allow-remote-takeover.html
Published: 2020 11 04 19:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: In Wild Critical Buffer Overflow Vulnerability in Solaris Can Allow Remote Takeover — CVE-2020-14871 - published about 6 years ago. Content: FireEye Mandiant has been investigating compromised Oracle Solaris machines in customer environments. During our investigations, we discovered an exploit tool on a customer’s system and analyzed it to see how it was attacking their Solaris environment. The FLARE team’s Offensive Task Force analyzed the exploit to determine how it worked, reproduced... http://www.fireeye.com/blog/threat-research/2020/11/critical-buffer-overflow-vulnerability-in-solaris-can-allow-remote-takeover.html Published: 2020 11 04 19:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Live off the Land? How About Bringing Your Own Island? An Overview of UNC1945 - published about 6 years ago.
Content: Through Mandiant investigation of intrusions, the FLARE Advanced Practices team observed a group we track as UNC1945 compromise managed service providers and operate against a tailored set of targets within the financial and professional consulting industries by leveraging access to third-party networks (see this blog post for an in-depth descripti...
http://www.fireeye.com/blog/threat-research/2020/11/live-off-the-land-an-overview-of-unc1945.html
Published: 2020 11 02 19:15:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Through Mandiant investigation of intrusions, the FLARE Advanced Practices team observed a group we track as UNC1945 compromise managed service providers and operate against a tailored set of targets within the financial and professional consulting industries by leveraging access to third-party networks (see this blog post for an in-depth descripti...
http://www.fireeye.com/blog/threat-research/2020/11/live-off-the-land-an-overview-of-unc1945.html
Published: 2020 11 02 19:15:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Live off the Land? How About Bringing Your Own Island? An Overview of UNC1945 - published about 6 years ago. Content: Through Mandiant investigation of intrusions, the FLARE Advanced Practices team observed a group we track as UNC1945 compromise managed service providers and operate against a tailored set of targets within the financial and professional consulting industries by leveraging access to third-party networks (see this blog post for an in-depth descripti... http://www.fireeye.com/blog/threat-research/2020/11/live-off-the-land-an-overview-of-unc1945.html Published: 2020 11 02 19:15:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Unhappy Hour Special: KEGTAP and SINGLEMALT With a Ransomware Chaser - published about 6 years ago.
Content: Throughout 2020, ransomware activity has become increasingly prolific, relying on an ecosystem of distinct but co-enabling operations to gain access to targets of interest before conducting extortion. Mandiant Threat Intelligence has tracked several loader and backdoor campaigns that lead to the post-compromise deployment of ransomware, sometimes w...
http://www.fireeye.com/blog/threat-research/2020/10/kegtap-and-singlemalt-with-a-ransomware-chaser.html
Published: 2020 10 28 22:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Throughout 2020, ransomware activity has become increasingly prolific, relying on an ecosystem of distinct but co-enabling operations to gain access to targets of interest before conducting extortion. Mandiant Threat Intelligence has tracked several loader and backdoor campaigns that lead to the post-compromise deployment of ransomware, sometimes w...
http://www.fireeye.com/blog/threat-research/2020/10/kegtap-and-singlemalt-with-a-ransomware-chaser.html
Published: 2020 10 28 22:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Unhappy Hour Special: KEGTAP and SINGLEMALT With a Ransomware Chaser - published about 6 years ago. Content: Throughout 2020, ransomware activity has become increasingly prolific, relying on an ecosystem of distinct but co-enabling operations to gain access to targets of interest before conducting extortion. Mandiant Threat Intelligence has tracked several loader and backdoor campaigns that lead to the post-compromise deployment of ransomware, sometimes w... http://www.fireeye.com/blog/threat-research/2020/10/kegtap-and-singlemalt-with-a-ransomware-chaser.html Published: 2020 10 28 22:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: WOW64!Hooks: WOW64 Subsystem Internals and Hooking Techniques - published about 6 years ago.
Content: Microsoft is known for their backwards compatibility. When they rolled out the 64-bit variant of Windows years ago they needed to provide compatibility with existing 32-bit applications. In order to provide seamless execution regardless of application bitness, the WoW (Windows on Windows) system was coined. This layer, which will be referred to as ...
http://www.fireeye.com/blog/threat-research/2020/11/wow64-subsystem-internals-and-hooking-techniques.html
Published: 2020 11 09 19:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Microsoft is known for their backwards compatibility. When they rolled out the 64-bit variant of Windows years ago they needed to provide compatibility with existing 32-bit applications. In order to provide seamless execution regardless of application bitness, the WoW (Windows on Windows) system was coined. This layer, which will be referred to as ...
http://www.fireeye.com/blog/threat-research/2020/11/wow64-subsystem-internals-and-hooking-techniques.html
Published: 2020 11 09 19:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: WOW64!Hooks: WOW64 Subsystem Internals and Hooking Techniques - published about 6 years ago. Content: Microsoft is known for their backwards compatibility. When they rolled out the 64-bit variant of Windows years ago they needed to provide compatibility with existing 32-bit applications. In order to provide seamless execution regardless of application bitness, the WoW (Windows on Windows) system was coined. This layer, which will be referred to as ... http://www.fireeye.com/blog/threat-research/2020/11/wow64-subsystem-internals-and-hooking-techniques.html Published: 2020 11 09 19:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: CertUtil Qualms: They Came to Drop FOMBs - published about 7 years ago.
Content: This blog post covers an interesting intrusion attempt that Mandiant Managed Defense thwarted involving the rapid weaponization of a recently disclosed vulnerability combined with the creative use of WMI compiled “.bmf” files and CertUtil for obfuscated execution. This intrusion attempt highlights a number of valuable lessons in security, chiefly:...
http://www.fireeye.com/blog/threat-research/2019/10/certutil-qualms-they-came-to-drop-fombs.html
Published: 2019 10 29 18:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: This blog post covers an interesting intrusion attempt that Mandiant Managed Defense thwarted involving the rapid weaponization of a recently disclosed vulnerability combined with the creative use of WMI compiled “.bmf” files and CertUtil for obfuscated execution. This intrusion attempt highlights a number of valuable lessons in security, chiefly:...
http://www.fireeye.com/blog/threat-research/2019/10/certutil-qualms-they-came-to-drop-fombs.html
Published: 2019 10 29 18:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: CertUtil Qualms: They Came to Drop FOMBs - published about 7 years ago. Content: This blog post covers an interesting intrusion attempt that Mandiant Managed Defense thwarted involving the rapid weaponization of a recently disclosed vulnerability combined with the creative use of WMI compiled “.bmf” files and CertUtil for obfuscated execution. This intrusion attempt highlights a number of valuable lessons in security, chiefly:... http://www.fireeye.com/blog/threat-research/2019/10/certutil-qualms-they-came-to-drop-fombs.html Published: 2019 10 29 18:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Hard Pass: Declining APT34’s Invite to Join Their Professional Network - published over 7 years ago.
Content: Background With increasing geopolitical tensions in the Middle East, we expect Iran to significantly increase the volume and scope of its cyber espionage campaigns. Iran has a critical need for strategic intelligence and is likely to fill this gap by conducting espionage against decision makers and key organizations that may have information that ...
http://www.fireeye.com/blog/threat-research/2019/07/hard-pass-declining-apt34-invite-to-join-their-professional-network.html
Published: 2019 07 18 15:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Background With increasing geopolitical tensions in the Middle East, we expect Iran to significantly increase the volume and scope of its cyber espionage campaigns. Iran has a critical need for strategic intelligence and is likely to fill this gap by conducting espionage against decision makers and key organizations that may have information that ...
http://www.fireeye.com/blog/threat-research/2019/07/hard-pass-declining-apt34-invite-to-join-their-professional-network.html
Published: 2019 07 18 15:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Hard Pass: Declining APT34’s Invite to Join Their Professional Network - published over 7 years ago. Content: Background With increasing geopolitical tensions in the Middle East, we expect Iran to significantly increase the volume and scope of its cyber espionage campaigns. Iran has a critical need for strategic intelligence and is likely to fill this gap by conducting espionage against decision makers and key organizations that may have information that ... http://www.fireeye.com/blog/threat-research/2019/07/hard-pass-declining-apt34-invite-to-join-their-professional-network.html Published: 2019 07 18 15:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: COOKIEJAR: Tracking Adversaries With FireEye Endpoint Security’s Logon Tracker Module - published over 6 years ago.
Content: During a recent investigation at a telecommunications company led by Mandiant Managed Defense, our team was tasked with rapidly identifying systems that had been accessed by a threat actor using legitimate, but compromised domain credentials. This sometimes-challenging task was made simple because the customer had enabled the Logon Tracker modu...
http://www.fireeye.com/blog/threat-research/2020/08/cookiejar-tracking-adversaries-with-fireeye-endpoint-security-module.html
Published: 2020 08 11 17:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: During a recent investigation at a telecommunications company led by Mandiant Managed Defense, our team was tasked with rapidly identifying systems that had been accessed by a threat actor using legitimate, but compromised domain credentials. This sometimes-challenging task was made simple because the customer had enabled the Logon Tracker modu...
http://www.fireeye.com/blog/threat-research/2020/08/cookiejar-tracking-adversaries-with-fireeye-endpoint-security-module.html
Published: 2020 08 11 17:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: COOKIEJAR: Tracking Adversaries With FireEye Endpoint Security’s Logon Tracker Module - published over 6 years ago. Content: During a recent investigation at a telecommunications company led by Mandiant Managed Defense, our team was tasked with rapidly identifying systems that had been accessed by a threat actor using legitimate, but compromised domain credentials. This sometimes-challenging task was made simple because the customer had enabled the Logon Tracker modu... http://www.fireeye.com/blog/threat-research/2020/08/cookiejar-tracking-adversaries-with-fireeye-endpoint-security-module.html Published: 2020 08 11 17:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Head Fake: Tackling Disruptive Ransomware Attacks - published about 7 years ago.
Content: Within the past several months, FireEye has observed financially-motivated threat actors employ tactics that focus on disrupting business processes by deploying ransomware in mass throughout a victim’s environment. Understanding that normal business processes are critical to organizational success, these ransomware campaigns have been accompanied w...
http://www.fireeye.com/blog/threat-research/2019/10/head-fake-tackling-disruptive-ransomware-attacks.html
Published: 2019 10 01 10:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Within the past several months, FireEye has observed financially-motivated threat actors employ tactics that focus on disrupting business processes by deploying ransomware in mass throughout a victim’s environment. Understanding that normal business processes are critical to organizational success, these ransomware campaigns have been accompanied w...
http://www.fireeye.com/blog/threat-research/2019/10/head-fake-tackling-disruptive-ransomware-attacks.html
Published: 2019 10 01 10:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Head Fake: Tackling Disruptive Ransomware Attacks - published about 7 years ago. Content: Within the past several months, FireEye has observed financially-motivated threat actors employ tactics that focus on disrupting business processes by deploying ransomware in mass throughout a victim’s environment. Understanding that normal business processes are critical to organizational success, these ransomware campaigns have been accompanied w... http://www.fireeye.com/blog/threat-research/2019/10/head-fake-tackling-disruptive-ransomware-attacks.html Published: 2019 10 01 10:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Purgalicious VBA: Macro Obfuscation With VBA Purging
Content:
http://www.fireeye.com/blog/threat-research/2020/11/purgalicious-vba-macro-obfuscation-with-vba-purging.html
Published: :
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content:
http://www.fireeye.com/blog/threat-research/2020/11/purgalicious-vba-macro-obfuscation-with-vba-purging.html
Published: :
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Purgalicious VBA: Macro Obfuscation With VBA Purging Content: http://www.fireeye.com/blog/threat-research/2020/11/purgalicious-vba-macro-obfuscation-with-vba-purging.html Published: : Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: Election Cyber Threats in the Asia-Pacific Region - published almost 6 years ago.
Content: In democratic societies, elections are the mechanism for choosing heads of state and policymakers. There are strong incentives for adversary nations to understand the intentions and preferences of the people and parties that will shape a country's future path and to reduce uncertainty about likely winners. Mandiant Threat Intelligence regularly obs...
http://www.fireeye.com/blog/threat-research/2020/11/election-cyber-threats-in-the-asia-pacific-region.html
Published: 2020 11 22 23:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: In democratic societies, elections are the mechanism for choosing heads of state and policymakers. There are strong incentives for adversary nations to understand the intentions and preferences of the people and parties that will shape a country's future path and to reduce uncertainty about likely winners. Mandiant Threat Intelligence regularly obs...
http://www.fireeye.com/blog/threat-research/2020/11/election-cyber-threats-in-the-asia-pacific-region.html
Published: 2020 11 22 23:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Election Cyber Threats in the Asia-Pacific Region - published almost 6 years ago. Content: In democratic societies, elections are the mechanism for choosing heads of state and policymakers. There are strong incentives for adversary nations to understand the intentions and preferences of the people and parties that will shape a country's future path and to reduce uncertainty about likely winners. Mandiant Threat Intelligence regularly obs... http://www.fireeye.com/blog/threat-research/2020/11/election-cyber-threats-in-the-asia-pacific-region.html Published: 2020 11 22 23:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Using Speakeasy Emulation Framework Programmatically to Unpack Malware - published almost 6 years ago.
Content: Andrew Davis recently announced the public release of his new Windows emulation framework named Speakeasy. While the introductory blog post focused on using Speakeasy as an automated malware sandbox of sorts, this entry will highlight another powerful use of the framework: automated malware unpacking. I will demonstrate, with code exampl...
http://www.fireeye.com/blog/threat-research/2020/12/using-speakeasy-emulation-framework-programmatically-to-unpack-malware.html
Published: 2020 12 01 20:30:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Andrew Davis recently announced the public release of his new Windows emulation framework named Speakeasy. While the introductory blog post focused on using Speakeasy as an automated malware sandbox of sorts, this entry will highlight another powerful use of the framework: automated malware unpacking. I will demonstrate, with code exampl...
http://www.fireeye.com/blog/threat-research/2020/12/using-speakeasy-emulation-framework-programmatically-to-unpack-malware.html
Published: 2020 12 01 20:30:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Using Speakeasy Emulation Framework Programmatically to Unpack Malware - published almost 6 years ago. Content: Andrew Davis recently announced the public release of his new Windows emulation framework named Speakeasy. While the introductory blog post focused on using Speakeasy as an automated malware sandbox of sorts, this entry will highlight another powerful use of the framework: automated malware unpacking. I will demonstrate, with code exampl... http://www.fireeye.com/blog/threat-research/2020/12/using-speakeasy-emulation-framework-programmatically-to-unpack-malware.html Published: 2020 12 01 20:30:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Unauthorized Access of FireEye Red Team Tools - published almost 6 years ago.
Content: Overview A highly sophisticated state-sponsored adversary stole FireEye Red Team tools. Because we believe that an adversary possesses these tools, and we do not know whether the attacker intends to use the stolen tools themselves or publicly disclose them, FireEye is releasing hundreds of countermeasures with this blog post to enable the broader ...
http://www.fireeye.com/blog/threat-research/2020/12/unauthorized-access-of-fireeye-red-team-tools.html
Published: 2020 12 08 21:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Overview A highly sophisticated state-sponsored adversary stole FireEye Red Team tools. Because we believe that an adversary possesses these tools, and we do not know whether the attacker intends to use the stolen tools themselves or publicly disclose them, FireEye is releasing hundreds of countermeasures with this blog post to enable the broader ...
http://www.fireeye.com/blog/threat-research/2020/12/unauthorized-access-of-fireeye-red-team-tools.html
Published: 2020 12 08 21:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Unauthorized Access of FireEye Red Team Tools - published almost 6 years ago. Content: Overview A highly sophisticated state-sponsored adversary stole FireEye Red Team tools. Because we believe that an adversary possesses these tools, and we do not know whether the attacker intends to use the stolen tools themselves or publicly disclose them, FireEye is releasing hundreds of countermeasures with this blog post to enable the broader ... http://www.fireeye.com/blog/threat-research/2020/12/unauthorized-access-of-fireeye-red-team-tools.html Published: 2020 12 08 21:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: Highly Evasive Attacker Leverages SolarWinds Supply Chain to Compromise Multiple Global Victims With SUNBURST Backdoor - published almost 6 years ago.
Content: Executive Summary We have discovered a global intrusion campaign. We are tracking the actors behind this campaign as UNC2452. FireEye discovered a supply chain attack trojanizing SolarWinds Orion business software updates in order to distribute malware we call SUNBURST. The attacker’s post compromise activity leverages multiple techniq...
http://www.fireeye.com/blog/threat-research/2020/12/evasive-attacker-leverages-solarwinds-supply-chain-compromises-with-sunburst-backdoor.html
Published: 2020 12 13 22:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Executive Summary We have discovered a global intrusion campaign. We are tracking the actors behind this campaign as UNC2452. FireEye discovered a supply chain attack trojanizing SolarWinds Orion business software updates in order to distribute malware we call SUNBURST. The attacker’s post compromise activity leverages multiple techniq...
http://www.fireeye.com/blog/threat-research/2020/12/evasive-attacker-leverages-solarwinds-supply-chain-compromises-with-sunburst-backdoor.html
Published: 2020 12 13 22:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Highly Evasive Attacker Leverages SolarWinds Supply Chain to Compromise Multiple Global Victims With SUNBURST Backdoor - published almost 6 years ago. Content: Executive Summary We have discovered a global intrusion campaign. We are tracking the actors behind this campaign as UNC2452. FireEye discovered a supply chain attack trojanizing SolarWinds Orion business software updates in order to distribute malware we call SUNBURST. The attacker’s post compromise activity leverages multiple techniq... http://www.fireeye.com/blog/threat-research/2020/12/evasive-attacker-leverages-solarwinds-supply-chain-compromises-with-sunburst-backdoor.html Published: 2020 12 13 22:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: SUNBURST Additional Technical Details - published almost 6 years ago.
Content: FireEye has discovered additional details about the SUNBURST backdoor since our initial publication on Dec. 13, 2020. Before diving into the technical depth of this malware, we recommend readers familiarize themselves with our blog post about the SolarWinds supply chain compromise, which revealed a global intrusion campaign by a sophisticated thr...
http://www.fireeye.com/blog/threat-research/2020/12/sunburst-additional-technical-details.html
Published: 2020 12 24 20:15:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: FireEye has discovered additional details about the SUNBURST backdoor since our initial publication on Dec. 13, 2020. Before diving into the technical depth of this malware, we recommend readers familiarize themselves with our blog post about the SolarWinds supply chain compromise, which revealed a global intrusion campaign by a sophisticated thr...
http://www.fireeye.com/blog/threat-research/2020/12/sunburst-additional-technical-details.html
Published: 2020 12 24 20:15:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: SUNBURST Additional Technical Details - published almost 6 years ago. Content: FireEye has discovered additional details about the SUNBURST backdoor since our initial publication on Dec. 13, 2020. Before diving into the technical depth of this malware, we recommend readers familiarize themselves with our blog post about the SolarWinds supply chain compromise, which revealed a global intrusion campaign by a sophisticated thr... http://www.fireeye.com/blog/threat-research/2020/12/sunburst-additional-technical-details.html Published: 2020 12 24 20:15:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Excelerating Analysis – Tips and Tricks to Analyze Data with Microsoft Excel - published almost 7 years ago.
Content: Incident response investigations don’t always involve standard host-based artifacts with fully developed parsing and analysis tools. At FireEye Mandiant, we frequently encounter incidents that involve a number of systems and solutions that utilize custom logging or artifact data. Determining what happened in an incident involves taking a dive into ...
http://www.fireeye.com/blog/threat-research/2019/12/tips-and-tricks-to-analyze-data-with-microsoft-excel.html
Published: 2019 12 03 16:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Incident response investigations don’t always involve standard host-based artifacts with fully developed parsing and analysis tools. At FireEye Mandiant, we frequently encounter incidents that involve a number of systems and solutions that utilize custom logging or artifact data. Determining what happened in an incident involves taking a dive into ...
http://www.fireeye.com/blog/threat-research/2019/12/tips-and-tricks-to-analyze-data-with-microsoft-excel.html
Published: 2019 12 03 16:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Excelerating Analysis – Tips and Tricks to Analyze Data with Microsoft Excel - published almost 7 years ago. Content: Incident response investigations don’t always involve standard host-based artifacts with fully developed parsing and analysis tools. At FireEye Mandiant, we frequently encounter incidents that involve a number of systems and solutions that utilize custom logging or artifact data. Determining what happened in an incident involves taking a dive into ... http://www.fireeye.com/blog/threat-research/2019/12/tips-and-tricks-to-analyze-data-with-microsoft-excel.html Published: 2019 12 03 16:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: Emulation of Kernel Mode Rootkits With Speakeasy - published almost 6 years ago.
Content: In August 2020, we released a blog post about how the Speakeasy emulation framework can be used to emulate user mode malware such as shellcode. If you haven’t had a chance, give the post a read today. In addition to user mode emulation, Speakeasy also supports emulation of kernel mode Windows binaries. When malware authors employ kernel mode mal...
http://www.fireeye.com/blog/threat-research/2021/01/emulation-of-kernel-mode-rootkits-with-speakeasy.html
Published: 2021 01 20 16:45:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: In August 2020, we released a blog post about how the Speakeasy emulation framework can be used to emulate user mode malware such as shellcode. If you haven’t had a chance, give the post a read today. In addition to user mode emulation, Speakeasy also supports emulation of kernel mode Windows binaries. When malware authors employ kernel mode mal...
http://www.fireeye.com/blog/threat-research/2021/01/emulation-of-kernel-mode-rootkits-with-speakeasy.html
Published: 2021 01 20 16:45:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Emulation of Kernel Mode Rootkits With Speakeasy - published almost 6 years ago. Content: In August 2020, we released a blog post about how the Speakeasy emulation framework can be used to emulate user mode malware such as shellcode. If you haven’t had a chance, give the post a read today. In addition to user mode emulation, Speakeasy also supports emulation of kernel mode Windows binaries. When malware authors employ kernel mode mal... http://www.fireeye.com/blog/threat-research/2021/01/emulation-of-kernel-mode-rootkits-with-speakeasy.html Published: 2021 01 20 16:45:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Training Transformers for Cyber Security Tasks: A Case Study on Malicious URL Prediction - published almost 6 years ago.
Content: Highlights Perform a case study on using Transformer models to solve cyber security problems Train a Transformer model to detect malicious URLs under multiple training regimes Compare our model against other deep learning methods, and show it performs on-par with other top-scoring models Identify issues with applying generative p...
http://www.fireeye.com/blog/threat-research/2021/01/training-transformers-for-cyber-security-tasks-malicious-url-prediction.html
Published: 2021 01 21 17:30:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Highlights Perform a case study on using Transformer models to solve cyber security problems Train a Transformer model to detect malicious URLs under multiple training regimes Compare our model against other deep learning methods, and show it performs on-par with other top-scoring models Identify issues with applying generative p...
http://www.fireeye.com/blog/threat-research/2021/01/training-transformers-for-cyber-security-tasks-malicious-url-prediction.html
Published: 2021 01 21 17:30:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Training Transformers for Cyber Security Tasks: A Case Study on Malicious URL Prediction - published almost 6 years ago. Content: Highlights Perform a case study on using Transformer models to solve cyber security problems Train a Transformer model to detect malicious URLs under multiple training regimes Compare our model against other deep learning methods, and show it performs on-par with other top-scoring models Identify issues with applying generative p... http://www.fireeye.com/blog/threat-research/2021/01/training-transformers-for-cyber-security-tasks-malicious-url-prediction.html Published: 2021 01 21 17:30:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Phishing Campaign Leverages WOFF Obfuscation and Telegram Channels for Communication - published almost 6 years ago.
Content: FireEye Email Security recently encountered various phishing campaigns, mostly in the Americas and Europe, using source code obfuscation with compromised or bad domains. These domains were masquerading as authentic websites and stole personal information such as credit card data. The stolen information was then shared to cross-platform, cloud-bas...
http://www.fireeye.com/blog/threat-research/2021/01/phishing-campaign-woff-obfuscation-telegram-communications.html
Published: 2021 01 26 20:45:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: FireEye Email Security recently encountered various phishing campaigns, mostly in the Americas and Europe, using source code obfuscation with compromised or bad domains. These domains were masquerading as authentic websites and stole personal information such as credit card data. The stolen information was then shared to cross-platform, cloud-bas...
http://www.fireeye.com/blog/threat-research/2021/01/phishing-campaign-woff-obfuscation-telegram-communications.html
Published: 2021 01 26 20:45:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Phishing Campaign Leverages WOFF Obfuscation and Telegram Channels for Communication - published almost 6 years ago. Content: FireEye Email Security recently encountered various phishing campaigns, mostly in the Americas and Europe, using source code obfuscation with compromised or bad domains. These domains were masquerading as authentic websites and stole personal information such as credit card data. The stolen information was then shared to cross-platform, cloud-bas... http://www.fireeye.com/blog/threat-research/2021/01/phishing-campaign-woff-obfuscation-telegram-communications.html Published: 2021 01 26 20:45:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: FLARE VM Update - published almost 8 years ago.
Content: FLARE VM is the first of its kind reverse engineering and malware analysis distribution on Windows platform. Since its introduction in July 2017, FLARE VM has been continuously trusted and used by many reverse engineers, malware analysts, and security researchers as their go-to environment for analyzing malware. Just like the ever-evolving securi...
http://www.fireeye.com/blog/threat-research/2018/11/flare-vm-update.html
Published: 2018 11 14 20:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: FLARE VM is the first of its kind reverse engineering and malware analysis distribution on Windows platform. Since its introduction in July 2017, FLARE VM has been continuously trusted and used by many reverse engineers, malware analysts, and security researchers as their go-to environment for analyzing malware. Just like the ever-evolving securi...
http://www.fireeye.com/blog/threat-research/2018/11/flare-vm-update.html
Published: 2018 11 14 20:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: FLARE VM Update - published almost 8 years ago. Content: FLARE VM is the first of its kind reverse engineering and malware analysis distribution on Windows platform. Since its introduction in July 2017, FLARE VM has been continuously trusted and used by many reverse engineers, malware analysts, and security researchers as their go-to environment for analyzing malware. Just like the ever-evolving securi... http://www.fireeye.com/blog/threat-research/2018/11/flare-vm-update.html Published: 2018 11 14 20:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: A Totally Tubular Treatise on TRITON and TriStation - published over 8 years ago.
Content: Introduction In December 2017, FireEye's Mandiant discussed an incident response involving the TRITON framework. The TRITON attack and many of the publicly discussed ICS intrusions involved routine techniques where the threat actors used only what is necessary to succeed in their mission. For both INDUSTROYER and TRITON, the attackers moved from t...
http://www.fireeye.com/blog/threat-research/2018/06/totally-tubular-treatise-on-triton-and-tristation.html
Published: 2018 06 07 14:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Introduction In December 2017, FireEye's Mandiant discussed an incident response involving the TRITON framework. The TRITON attack and many of the publicly discussed ICS intrusions involved routine techniques where the threat actors used only what is necessary to succeed in their mission. For both INDUSTROYER and TRITON, the attackers moved from t...
http://www.fireeye.com/blog/threat-research/2018/06/totally-tubular-treatise-on-triton-and-tristation.html
Published: 2018 06 07 14:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: A Totally Tubular Treatise on TRITON and TriStation - published over 8 years ago. Content: Introduction In December 2017, FireEye's Mandiant discussed an incident response involving the TRITON framework. The TRITON attack and many of the publicly discussed ICS intrusions involved routine techniques where the threat actors used only what is necessary to succeed in their mission. For both INDUSTROYER and TRITON, the attackers moved from t... http://www.fireeye.com/blog/threat-research/2018/06/totally-tubular-treatise-on-triton-and-tristation.html Published: 2018 06 07 14:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Shining a Light on SolarCity: Practical Exploitation of the X2e IoT Device (Part Two) - published over 5 years ago.
Content: In this post, we continue our analysis of the SolarCity ConnectPort X2e Zigbee device (referred to throughout as X2e device). In Part One, we discussed the X2e at a high level, performed initial network-based attacks, then discussed the hardware techniques used to gain a remote shell on the X2e device as a non-privileged system user. In this se...
http://www.fireeye.com/blog/threat-research/2021/02/solarcity-exploitation-of-x2e-iot-device-part-two.html
Published: 2021 02 17 13:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: In this post, we continue our analysis of the SolarCity ConnectPort X2e Zigbee device (referred to throughout as X2e device). In Part One, we discussed the X2e at a high level, performed initial network-based attacks, then discussed the hardware techniques used to gain a remote shell on the X2e device as a non-privileged system user. In this se...
http://www.fireeye.com/blog/threat-research/2021/02/solarcity-exploitation-of-x2e-iot-device-part-two.html
Published: 2021 02 17 13:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Shining a Light on SolarCity: Practical Exploitation of the X2e IoT Device (Part Two) - published over 5 years ago. Content: In this post, we continue our analysis of the SolarCity ConnectPort X2e Zigbee device (referred to throughout as X2e device). In Part One, we discussed the X2e at a high level, performed initial network-based attacks, then discussed the hardware techniques used to gain a remote shell on the X2e device as a non-privileged system user. In this se... http://www.fireeye.com/blog/threat-research/2021/02/solarcity-exploitation-of-x2e-iot-device-part-two.html Published: 2021 02 17 13:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: Mandiant Exposes APT1 – One of China's Cyber Espionage Units & Releases 3,000 Indicators - published over 13 years ago.
Content: Today, The Mandiant® Intelligence Center™ released an unprecedented report exposing APT1's multi-year, enterprise-scale computer espionage campaign. APT1 is one of dozens of threat groups Mandiant tracks around the world and we consider it to be one of the most prolific in terms of the sheer quantity of information it has stolen. Highlig...
http://www.fireeye.com/blog/threat-research/2013/02/mandiant-exposes-apt1-chinas-cyber-espionage-units.html
Published: 2013 02 19 07:00:45
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Today, The Mandiant® Intelligence Center™ released an unprecedented report exposing APT1's multi-year, enterprise-scale computer espionage campaign. APT1 is one of dozens of threat groups Mandiant tracks around the world and we consider it to be one of the most prolific in terms of the sheer quantity of information it has stolen. Highlig...
http://www.fireeye.com/blog/threat-research/2013/02/mandiant-exposes-apt1-chinas-cyber-espionage-units.html
Published: 2013 02 19 07:00:45
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Mandiant Exposes APT1 – One of China's Cyber Espionage Units & Releases 3,000 Indicators - published over 13 years ago. Content: Today, The Mandiant® Intelligence Center™ released an unprecedented report exposing APT1's multi-year, enterprise-scale computer espionage campaign. APT1 is one of dozens of threat groups Mandiant tracks around the world and we consider it to be one of the most prolific in terms of the sheer quantity of information it has stolen. Highlig... http://www.fireeye.com/blog/threat-research/2013/02/mandiant-exposes-apt1-chinas-cyber-espionage-units.html Published: 2013 02 19 07:00:45 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Shining a Light on SolarCity: Practical Exploitation of the X2e IoT Device (Part One) - published over 5 years ago.
Content: In 2019, Mandiant’s Red Team discovered a series of vulnerabilities present within Digi International’s ConnectPort X2e device, which allows for remote code execution as a privileged user. Specifically, Mandiant’s research focused on SolarCity’s (now owned by Tesla) rebranded ConnectPort X2e device, which is used in residential solar installations....
http://www.fireeye.com/blog/threat-research/2021/02/solarcity-exploitation-of-x2e-iot-device-part-one.html
Published: 2021 02 17 13:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: In 2019, Mandiant’s Red Team discovered a series of vulnerabilities present within Digi International’s ConnectPort X2e device, which allows for remote code execution as a privileged user. Specifically, Mandiant’s research focused on SolarCity’s (now owned by Tesla) rebranded ConnectPort X2e device, which is used in residential solar installations....
http://www.fireeye.com/blog/threat-research/2021/02/solarcity-exploitation-of-x2e-iot-device-part-one.html
Published: 2021 02 17 13:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Shining a Light on SolarCity: Practical Exploitation of the X2e IoT Device (Part One) - published over 5 years ago. Content: In 2019, Mandiant’s Red Team discovered a series of vulnerabilities present within Digi International’s ConnectPort X2e device, which allows for remote code execution as a privileged user. Specifically, Mandiant’s research focused on SolarCity’s (now owned by Tesla) rebranded ConnectPort X2e device, which is used in residential solar installations.... http://www.fireeye.com/blog/threat-research/2021/02/solarcity-exploitation-of-x2e-iot-device-part-one.html Published: 2021 02 17 13:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Cyber Criminals Exploit Accellion FTA for Data Theft and Extortion - published over 5 years ago.
Content: Starting in mid-December 2020, malicious actors that Mandiant tracks as UNC2546 exploited multiple zero-day vulnerabilities in Accellion’s legacy File Transfer Appliance (FTA) to install a newly discovered web shell named DEWMODE. The motivation of UNC2546 was not immediately apparent, but starting in late January 2021, several organizations that h...
http://www.fireeye.com/blog/threat-research/2021/02/accellion-fta-exploited-for-data-theft-and-extortion.html
Published: 2021 02 22 14:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Starting in mid-December 2020, malicious actors that Mandiant tracks as UNC2546 exploited multiple zero-day vulnerabilities in Accellion’s legacy File Transfer Appliance (FTA) to install a newly discovered web shell named DEWMODE. The motivation of UNC2546 was not immediately apparent, but starting in late January 2021, several organizations that h...
http://www.fireeye.com/blog/threat-research/2021/02/accellion-fta-exploited-for-data-theft-and-extortion.html
Published: 2021 02 22 14:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Cyber Criminals Exploit Accellion FTA for Data Theft and Extortion - published over 5 years ago. Content: Starting in mid-December 2020, malicious actors that Mandiant tracks as UNC2546 exploited multiple zero-day vulnerabilities in Accellion’s legacy File Transfer Appliance (FTA) to install a newly discovered web shell named DEWMODE. The motivation of UNC2546 was not immediately apparent, but starting in late January 2021, several organizations that h... http://www.fireeye.com/blog/threat-research/2021/02/accellion-fta-exploited-for-data-theft-and-extortion.html Published: 2021 02 22 14:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: So Unchill: Melting UNC2198 ICEDID to Ransomware Operations - published over 5 years ago.
Content: Mandiant Advanced Practices (AP) closely tracks the shifting tactics, techniques, and procedures (TTPs) of financially motivated groups who severely disrupt organizations with ransomware. In May 2020, FireEye released a blog post detailing intrusion tradecraft associated with the deployment of MAZE. As of publishing this post, we track 11 disti...
http://www.fireeye.com/blog/threat-research/2021/02/melting-unc2198-icedid-to-ransomware-operations.html
Published: 2021 02 25 16:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Mandiant Advanced Practices (AP) closely tracks the shifting tactics, techniques, and procedures (TTPs) of financially motivated groups who severely disrupt organizations with ransomware. In May 2020, FireEye released a blog post detailing intrusion tradecraft associated with the deployment of MAZE. As of publishing this post, we track 11 disti...
http://www.fireeye.com/blog/threat-research/2021/02/melting-unc2198-icedid-to-ransomware-operations.html
Published: 2021 02 25 16:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: So Unchill: Melting UNC2198 ICEDID to Ransomware Operations - published over 5 years ago. Content: Mandiant Advanced Practices (AP) closely tracks the shifting tactics, techniques, and procedures (TTPs) of financially motivated groups who severely disrupt organizations with ransomware. In May 2020, FireEye released a blog post detailing intrusion tradecraft associated with the deployment of MAZE. As of publishing this post, we track 11 disti... http://www.fireeye.com/blog/threat-research/2021/02/melting-unc2198-icedid-to-ransomware-operations.html Published: 2021 02 25 16:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Fuzzing Image Parsing in Windows, Part Two: Uninitialized Memory - published over 5 years ago.
Content: Continuing our discussion of image parsing vulnerabilities in Windows, we take a look at a comparatively less popular vulnerability class: uninitialized memory. In this post, we will look at Windows’ inbuilt image parsers—specifically for vulnerabilities involving the use of uninitialized memory. The Vulnerability: Uninitialized Memory In unman...
http://www.fireeye.com/blog/threat-research/2021/03/fuzzing-image-parsing-in-windows-uninitialized-memory.html
Published: 2021 03 03 19:30:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Continuing our discussion of image parsing vulnerabilities in Windows, we take a look at a comparatively less popular vulnerability class: uninitialized memory. In this post, we will look at Windows’ inbuilt image parsers—specifically for vulnerabilities involving the use of uninitialized memory. The Vulnerability: Uninitialized Memory In unman...
http://www.fireeye.com/blog/threat-research/2021/03/fuzzing-image-parsing-in-windows-uninitialized-memory.html
Published: 2021 03 03 19:30:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Fuzzing Image Parsing in Windows, Part Two: Uninitialized Memory - published over 5 years ago. Content: Continuing our discussion of image parsing vulnerabilities in Windows, we take a look at a comparatively less popular vulnerability class: uninitialized memory. In this post, we will look at Windows’ inbuilt image parsers—specifically for vulnerabilities involving the use of uninitialized memory. The Vulnerability: Uninitialized Memory In unman... http://www.fireeye.com/blog/threat-research/2021/03/fuzzing-image-parsing-in-windows-uninitialized-memory.html Published: 2021 03 03 19:30:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: New SUNSHUTTLE Second-Stage Backdoor Uncovered Targeting U.S.-Based Entity; Possible Connection to UNC2452 - published over 5 years ago.
Content: Executive Summary In August 2020, a U.S.-based entity uploaded a new backdoor that we have named SUNSHUTTLE to a public malware repository. SUNSHUTTLE is a second-stage backdoor written in GoLang that features some detection evasion capabilities. Mandiant observed SUNSHUTTLE at a victim compromised by UNC2452, and have indications that ...
http://www.fireeye.com/blog/threat-research/2021/03/sunshuttle-second-stage-backdoor-targeting-us-based-entity.html
Published: 2021 03 04 17:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Executive Summary In August 2020, a U.S.-based entity uploaded a new backdoor that we have named SUNSHUTTLE to a public malware repository. SUNSHUTTLE is a second-stage backdoor written in GoLang that features some detection evasion capabilities. Mandiant observed SUNSHUTTLE at a victim compromised by UNC2452, and have indications that ...
http://www.fireeye.com/blog/threat-research/2021/03/sunshuttle-second-stage-backdoor-targeting-us-based-entity.html
Published: 2021 03 04 17:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: New SUNSHUTTLE Second-Stage Backdoor Uncovered Targeting U.S.-Based Entity; Possible Connection to UNC2452 - published over 5 years ago. Content: Executive Summary In August 2020, a U.S.-based entity uploaded a new backdoor that we have named SUNSHUTTLE to a public malware repository. SUNSHUTTLE is a second-stage backdoor written in GoLang that features some detection evasion capabilities. Mandiant observed SUNSHUTTLE at a victim compromised by UNC2452, and have indications that ... http://www.fireeye.com/blog/threat-research/2021/03/sunshuttle-second-stage-backdoor-targeting-us-based-entity.html Published: 2021 03 04 17:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: Detection and Response to Exploitation of Microsoft Exchange Zero-Day Vulnerabilities - published over 5 years ago.
Content: Beginning in January 2021, Mandiant Managed Defense observed multiple instances of abuse of Microsoft Exchange Server within at least one client environment. The observed activity included creation of web shells for persistent access, remote code execution, and reconnaissance for endpoint security solutions. Our investigation revealed that the file...
http://www.fireeye.com/blog/threat-research/2021/03/detection-response-to-exploitation-of-microsoft-exchange-zero-day-vulnerabilities.html
Published: 2021 03 04 22:30:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Beginning in January 2021, Mandiant Managed Defense observed multiple instances of abuse of Microsoft Exchange Server within at least one client environment. The observed activity included creation of web shells for persistent access, remote code execution, and reconnaissance for endpoint security solutions. Our investigation revealed that the file...
http://www.fireeye.com/blog/threat-research/2021/03/detection-response-to-exploitation-of-microsoft-exchange-zero-day-vulnerabilities.html
Published: 2021 03 04 22:30:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Detection and Response to Exploitation of Microsoft Exchange Zero-Day Vulnerabilities - published over 5 years ago. Content: Beginning in January 2021, Mandiant Managed Defense observed multiple instances of abuse of Microsoft Exchange Server within at least one client environment. The observed activity included creation of web shells for persistent access, remote code execution, and reconnaissance for endpoint security solutions. Our investigation revealed that the file... http://www.fireeye.com/blog/threat-research/2021/03/detection-response-to-exploitation-of-microsoft-exchange-zero-day-vulnerabilities.html Published: 2021 03 04 22:30:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Remediation and Hardening Strategies for Microsoft 365 to Defend Against UNC2452 - published almost 6 years ago.
Content: UPDATE (Mar. 18): Mandiant recently observed targeted threat actors modifying mailbox folder permissions of user mailboxes to maintain persistent access to the targeted users' email messages. This stealthy technique is not usually monitored by defenders and provides threat actors a way to access the desired email messages using any com...
http://www.fireeye.com/blog/threat-research/2021/01/remediation-and-hardening-strategies-for-microsoft-365-to-defend-against-unc2452.html
Published: 2021 01 19 14:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: UPDATE (Mar. 18): Mandiant recently observed targeted threat actors modifying mailbox folder permissions of user mailboxes to maintain persistent access to the targeted users' email messages. This stealthy technique is not usually monitored by defenders and provides threat actors a way to access the desired email messages using any com...
http://www.fireeye.com/blog/threat-research/2021/01/remediation-and-hardening-strategies-for-microsoft-365-to-defend-against-unc2452.html
Published: 2021 01 19 14:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Remediation and Hardening Strategies for Microsoft 365 to Defend Against UNC2452 - published almost 6 years ago. Content: UPDATE (Mar. 18): Mandiant recently observed targeted threat actors modifying mailbox folder permissions of user mailboxes to maintain persistent access to the targeted users' email messages. This stealthy technique is not usually monitored by defenders and provides threat actors a way to access the desired email messages using any com... http://www.fireeye.com/blog/threat-research/2021/01/remediation-and-hardening-strategies-for-microsoft-365-to-defend-against-unc2452.html Published: 2021 01 19 14:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Monitoring ICS Cyber Operation Tools and Software Exploit Modules To Anticipate Future Threats - published over 6 years ago.
Content: There has only been a small number of broadly documented cyber attacks targeting operational technologies (OT) / industrial control systems (ICS) over the last decade. While fewer attacks is clearly a good thing, the lack of an adequate sample size to determine risk thresholds can make it difficult for defenders to understand the threat environment...
http://www.fireeye.com/blog/threat-research/2020/03/monitoring-ics-cyber-operation-tools-and-software-exploit-modules.html
Published: 2020 03 23 12:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: There has only been a small number of broadly documented cyber attacks targeting operational technologies (OT) / industrial control systems (ICS) over the last decade. While fewer attacks is clearly a good thing, the lack of an adequate sample size to determine risk thresholds can make it difficult for defenders to understand the threat environment...
http://www.fireeye.com/blog/threat-research/2020/03/monitoring-ics-cyber-operation-tools-and-software-exploit-modules.html
Published: 2020 03 23 12:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Monitoring ICS Cyber Operation Tools and Software Exploit Modules To Anticipate Future Threats - published over 6 years ago. Content: There has only been a small number of broadly documented cyber attacks targeting operational technologies (OT) / industrial control systems (ICS) over the last decade. While fewer attacks is clearly a good thing, the lack of an adequate sample size to determine risk thresholds can make it difficult for defenders to understand the threat environment... http://www.fireeye.com/blog/threat-research/2020/03/monitoring-ics-cyber-operation-tools-and-software-exploit-modules.html Published: 2020 03 23 12:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: Back in a Bit: Attacker Use of the Windows Background Intelligent Transfer Service - published over 5 years ago.
Content: In this blog post we will describe: How attackers use the Background Intelligent Transfer Service (BITS) Forensic techniques for detecting attacker activity with data format specifications Public release of the BitsParser tool A real-world example of malware using BITS persistenc...
http://www.fireeye.com/blog/threat-research/2021/03/attacker-use-of-windows-background-intelligent-transfer-service.html
Published: 2021 03 31 15:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: In this blog post we will describe: How attackers use the Background Intelligent Transfer Service (BITS) Forensic techniques for detecting attacker activity with data format specifications Public release of the BitsParser tool A real-world example of malware using BITS persistenc...
http://www.fireeye.com/blog/threat-research/2021/03/attacker-use-of-windows-background-intelligent-transfer-service.html
Published: 2021 03 31 15:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Back in a Bit: Attacker Use of the Windows Background Intelligent Transfer Service - published over 5 years ago. Content: In this blog post we will describe: How attackers use the Background Intelligent Transfer Service (BITS) Forensic techniques for detecting attacker activity with data format specifications Public release of the BitsParser tool A real-world example of malware using BITS persistenc... http://www.fireeye.com/blog/threat-research/2021/03/attacker-use-of-windows-background-intelligent-transfer-service.html Published: 2021 03 31 15:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
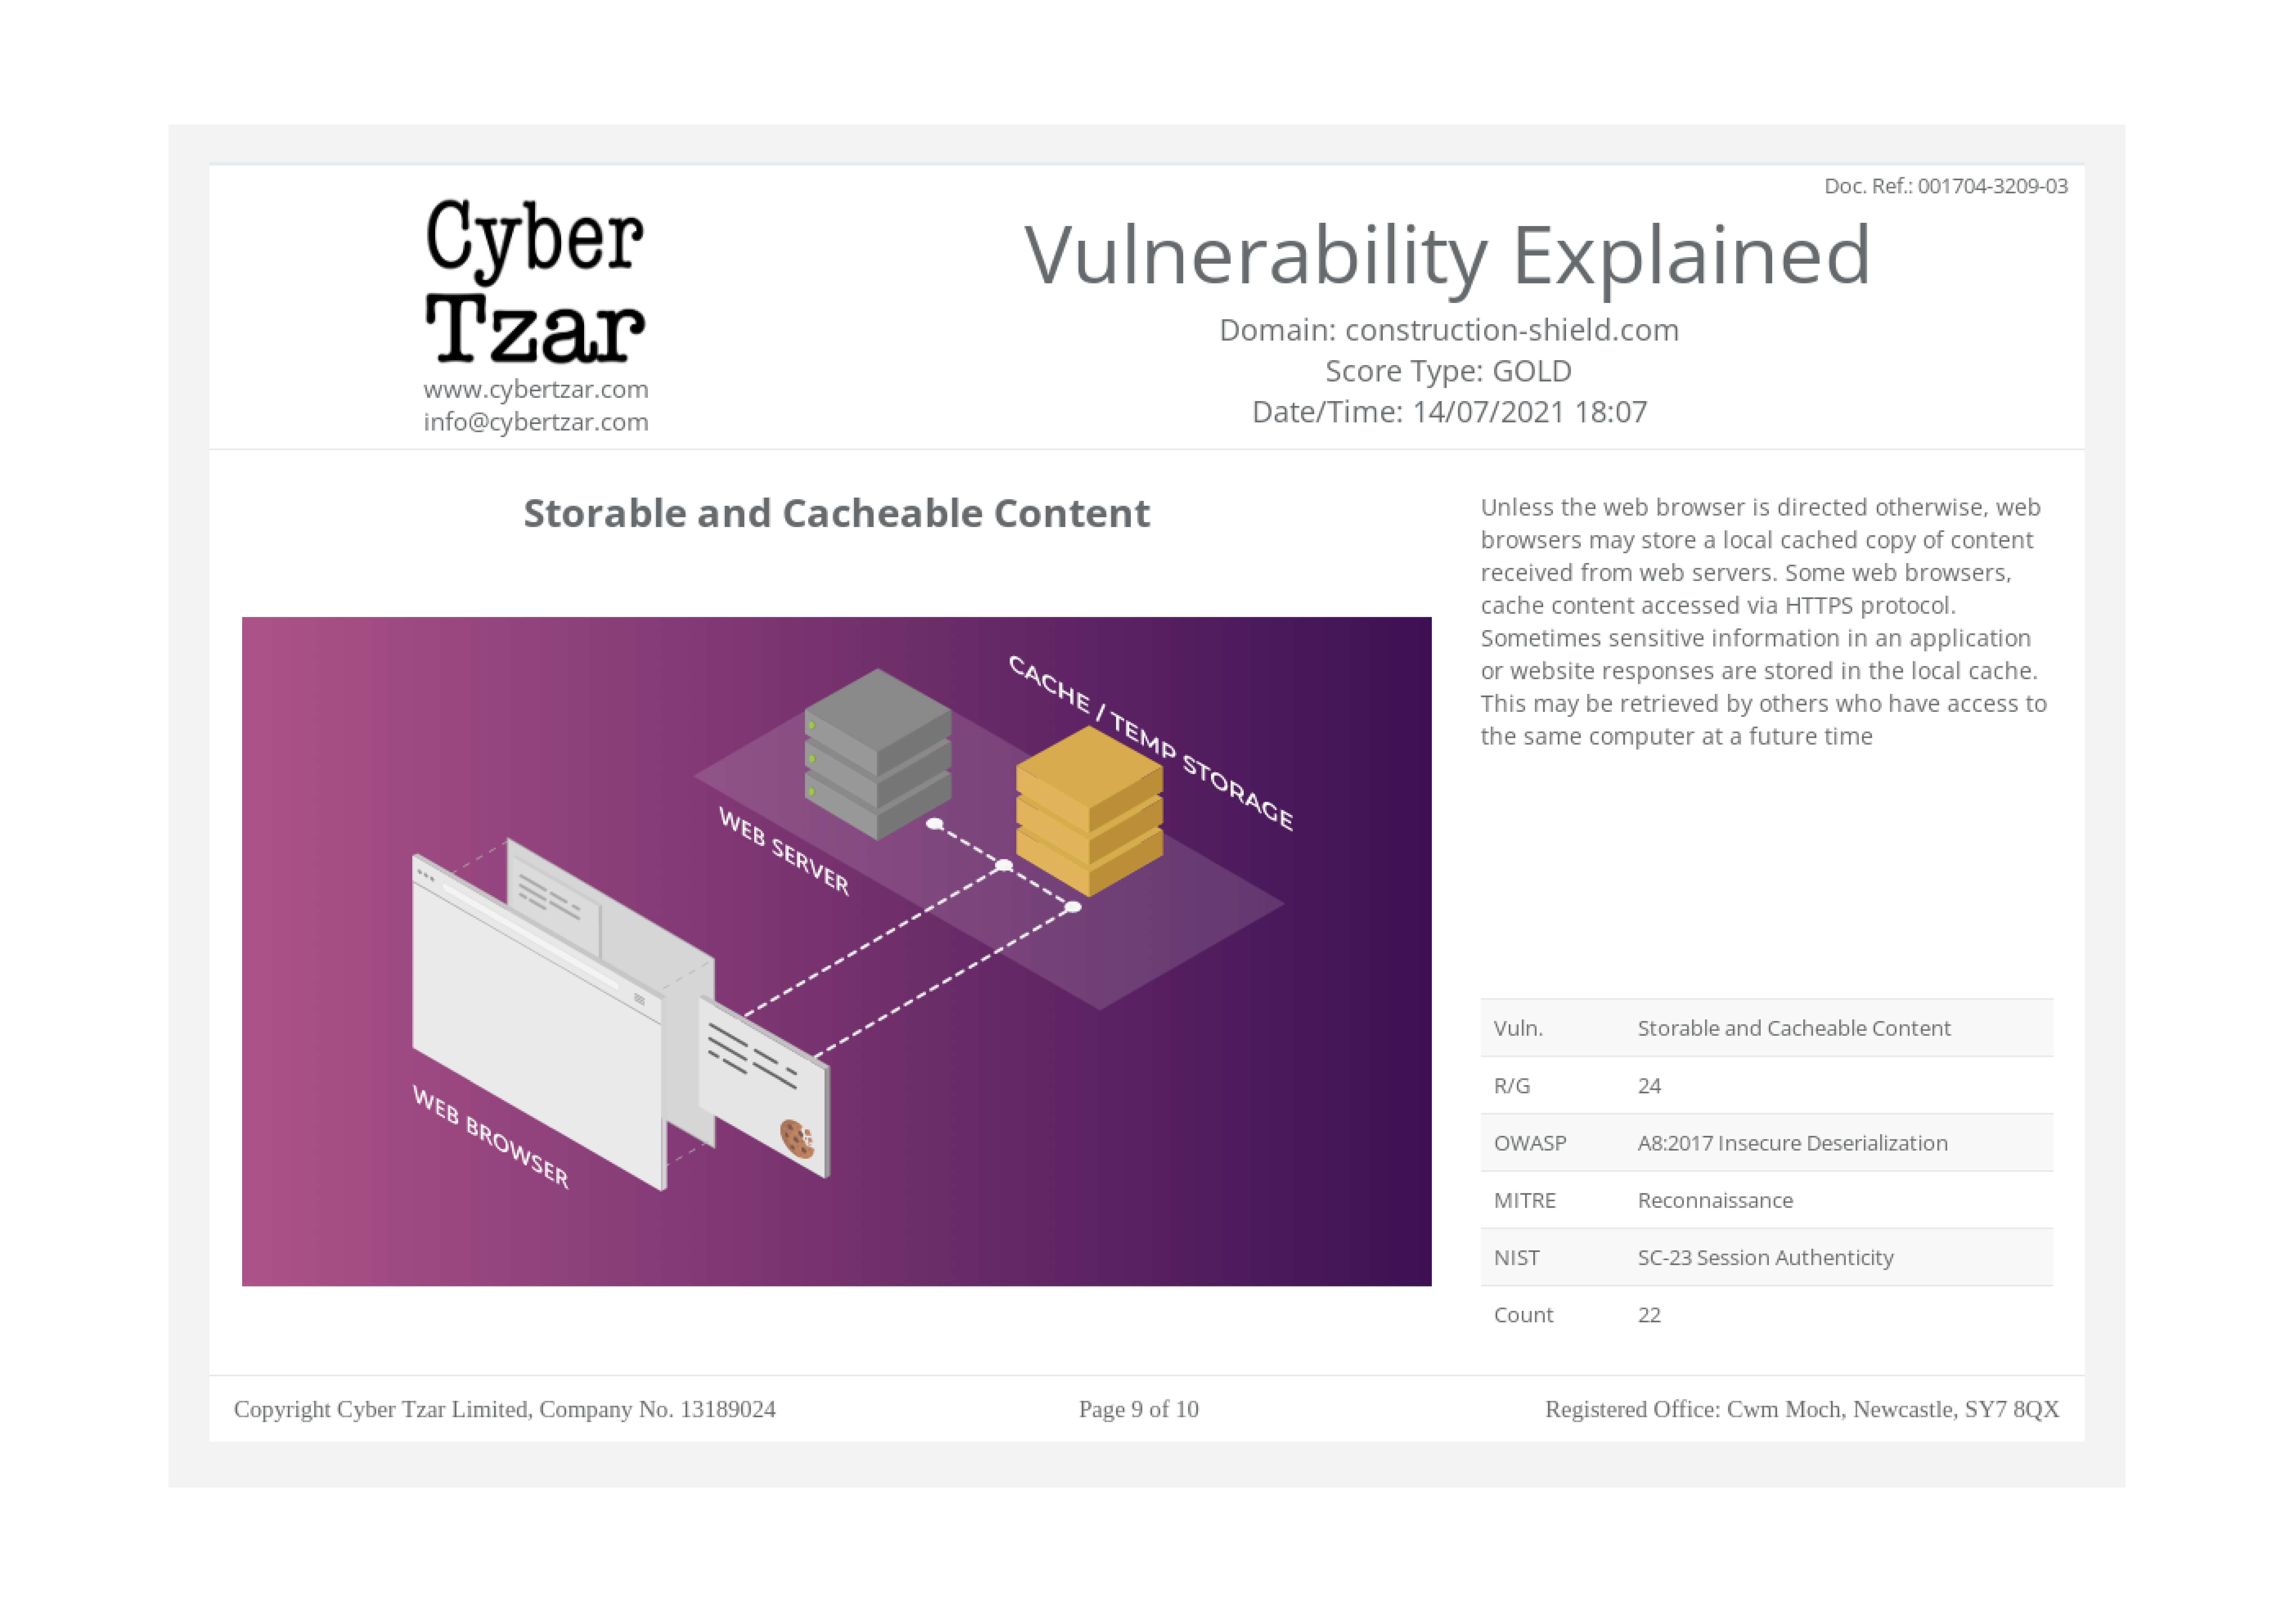
|
Article: M-Trends 2021: A View From the Front Lines - published over 5 years ago.
Content: We are thrilled to launch M-Trends 2021, the 12th edition of our annual FireEye Mandiant publication. The past year has been unique, as we witnessed an unprecedented combination of global events. Business operations shifted in response to the worldwide pandemic and threat actors continued to escalate the sophistication and aggressiveness of th...
http://www.fireeye.com/blog/threat-research/2021/04/m-trends-2021-a-view-from-the-front-lines.html
Published: 2021 04 13 13:45:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: We are thrilled to launch M-Trends 2021, the 12th edition of our annual FireEye Mandiant publication. The past year has been unique, as we witnessed an unprecedented combination of global events. Business operations shifted in response to the worldwide pandemic and threat actors continued to escalate the sophistication and aggressiveness of th...
http://www.fireeye.com/blog/threat-research/2021/04/m-trends-2021-a-view-from-the-front-lines.html
Published: 2021 04 13 13:45:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: M-Trends 2021: A View From the Front Lines - published over 5 years ago. Content: We are thrilled to launch M-Trends 2021, the 12th edition of our annual FireEye Mandiant publication. The past year has been unique, as we witnessed an unprecedented combination of global events. Business operations shifted in response to the worldwide pandemic and threat actors continued to escalate the sophistication and aggressiveness of th... http://www.fireeye.com/blog/threat-research/2021/04/m-trends-2021-a-view-from-the-front-lines.html Published: 2021 04 13 13:45:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
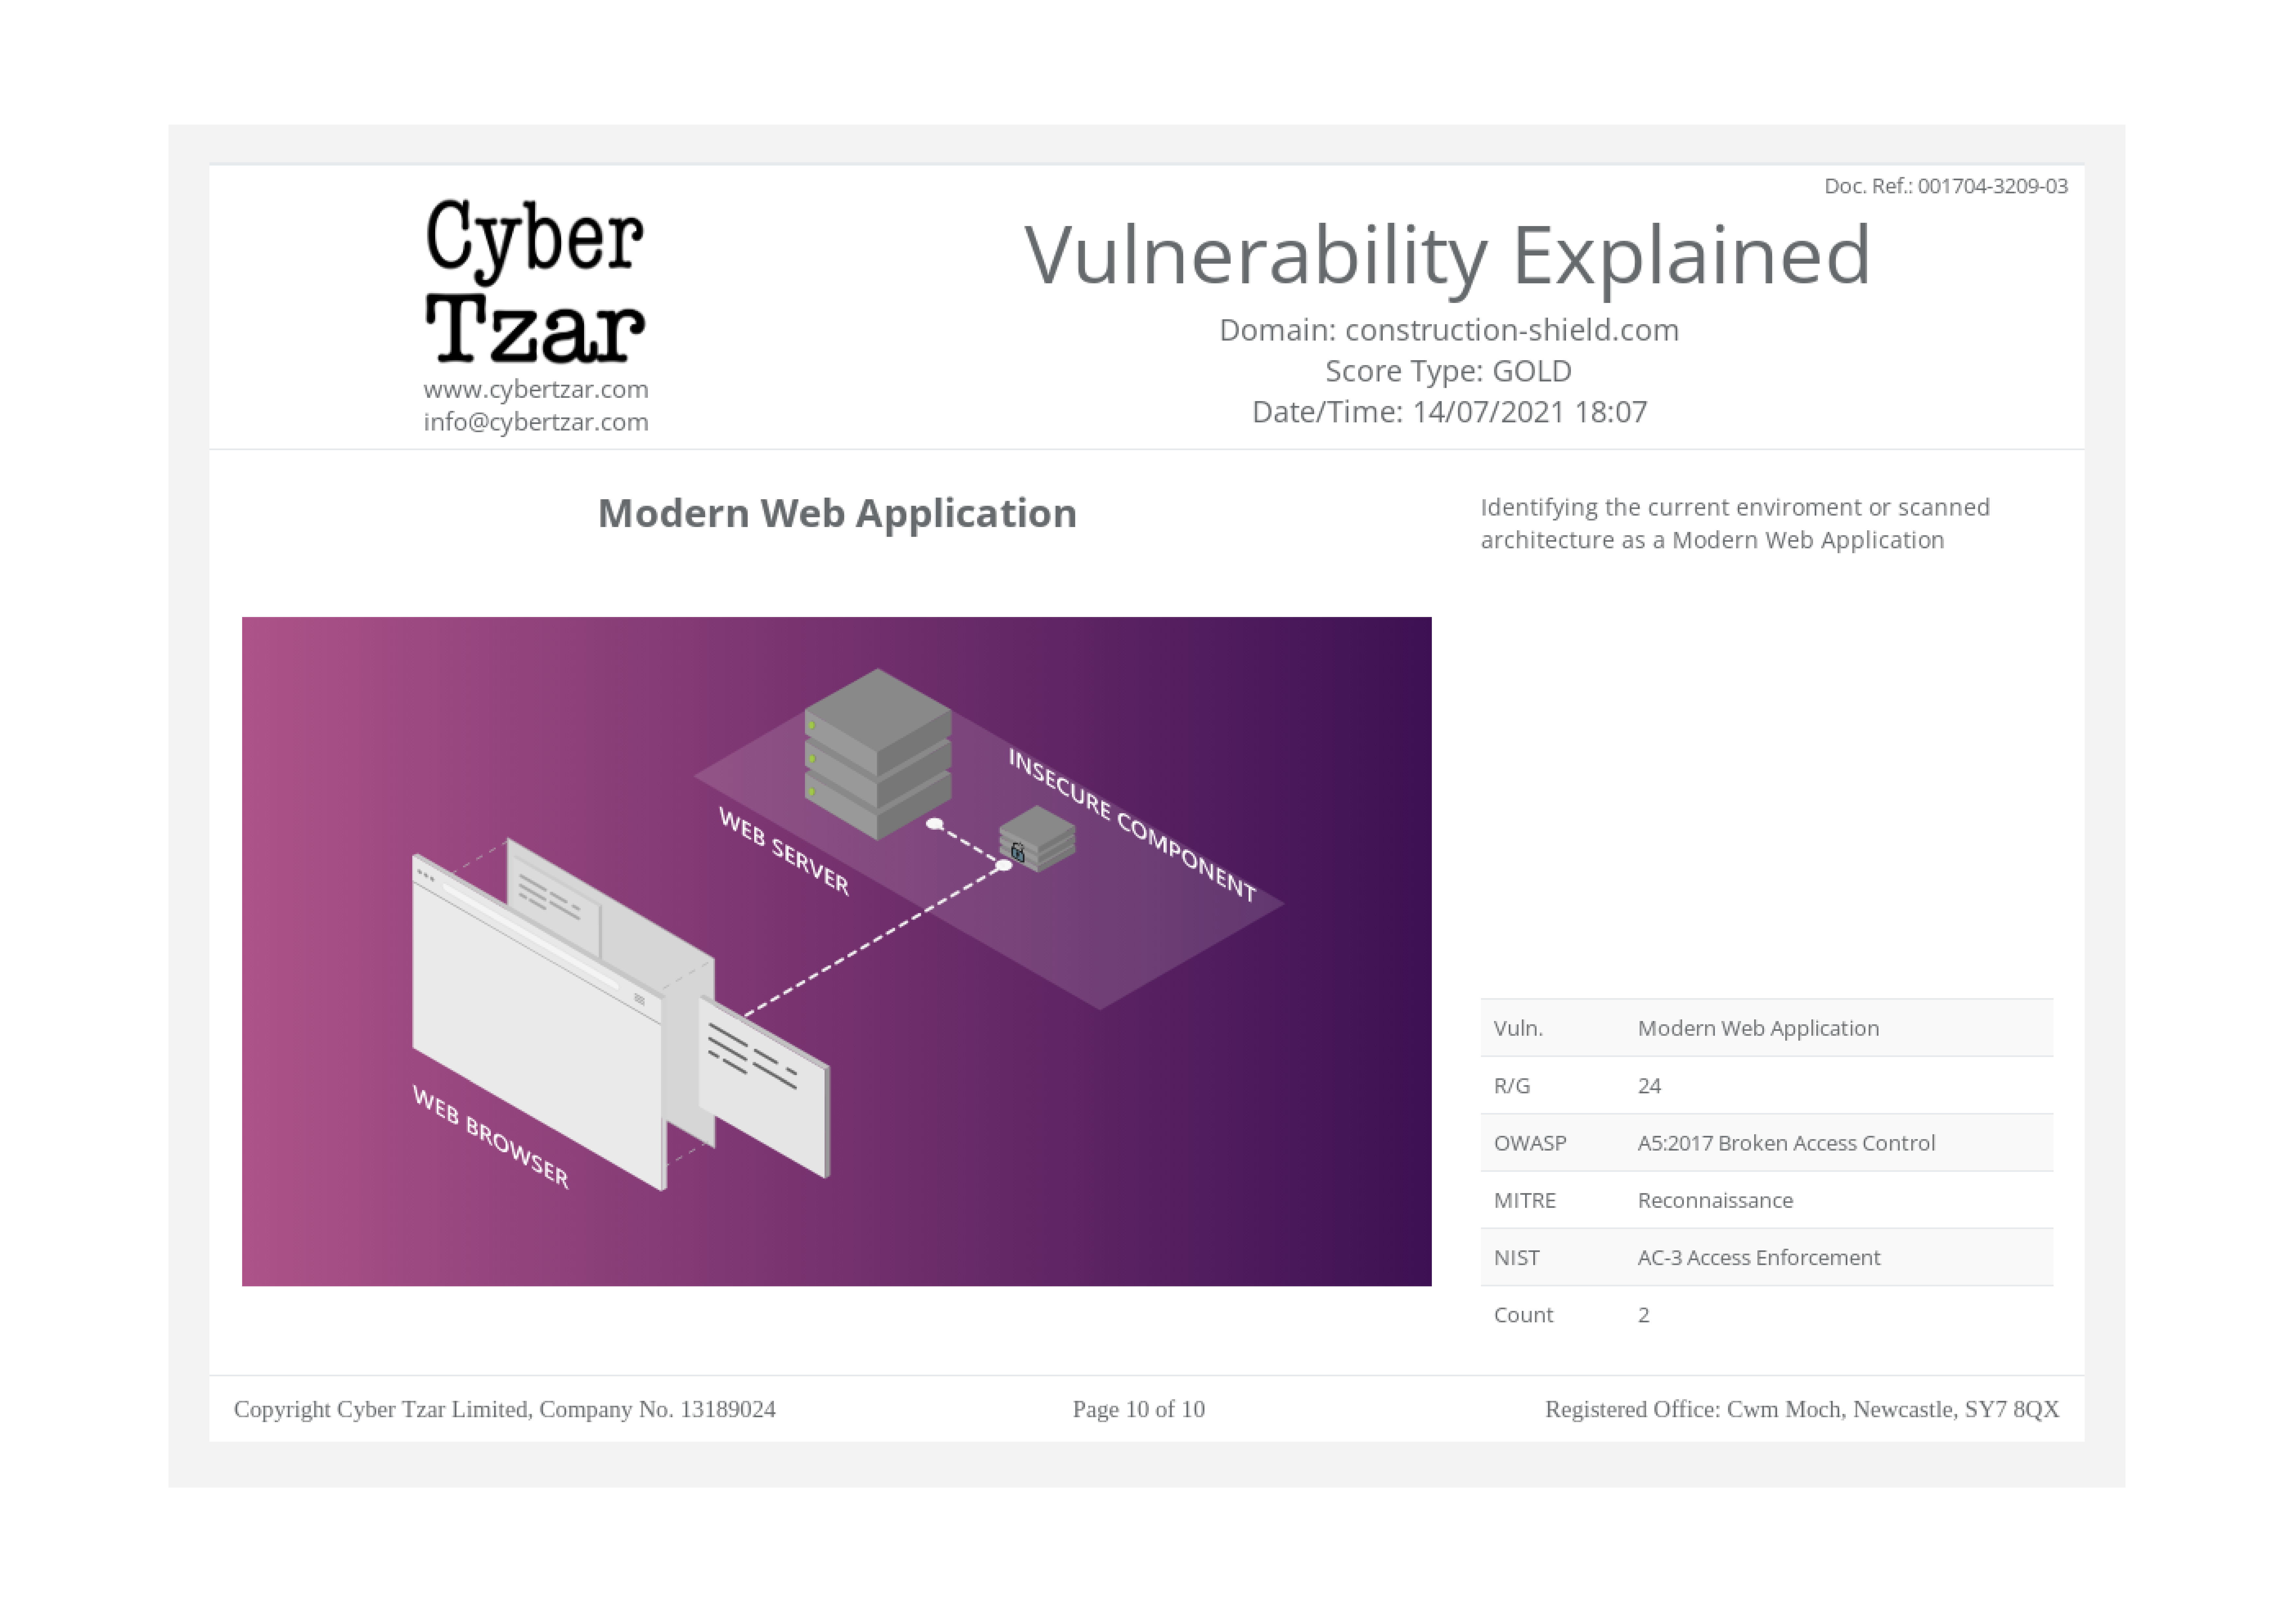
|
Article: Hacking Operational Technology for Defense: Lessons Learned From OT Red Teaming Smart Meter Control Infrastructure - published over 5 years ago.
Content: High-profile security incidents in the past decade have brought increased scrutiny to cyber security for operational technology (OT). However, there is a continued perception across critical infrastructure organizations that OT networks are isolated from public networks—such as the Internet. In Mandiant’s experience, the concept of an ‘air gap’ sep...
http://www.fireeye.com/blog/threat-research/2021/04/hacking-operational-technology-for-defense-lessons-learned.html
Published: 2021 04 13 15:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: High-profile security incidents in the past decade have brought increased scrutiny to cyber security for operational technology (OT). However, there is a continued perception across critical infrastructure organizations that OT networks are isolated from public networks—such as the Internet. In Mandiant’s experience, the concept of an ‘air gap’ sep...
http://www.fireeye.com/blog/threat-research/2021/04/hacking-operational-technology-for-defense-lessons-learned.html
Published: 2021 04 13 15:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Hacking Operational Technology for Defense: Lessons Learned From OT Red Teaming Smart Meter Control Infrastructure - published over 5 years ago. Content: High-profile security incidents in the past decade have brought increased scrutiny to cyber security for operational technology (OT). However, there is a continued perception across critical infrastructure organizations that OT networks are isolated from public networks—such as the Internet. In Mandiant’s experience, the concept of an ‘air gap’ sep... http://www.fireeye.com/blog/threat-research/2021/04/hacking-operational-technology-for-defense-lessons-learned.html Published: 2021 04 13 15:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: Abusing Replication: Stealing AD FS Secrets Over the Network - published over 5 years ago.
Content: Organizations are increasingly adopting cloud-based services such as Microsoft 365 to host applications and data. Sophisticated threat actors are catching on and Mandiant has observed an increased focus on long-term persistent access to Microsoft 365 as one of their primary objectives. The focus on developing novel and hard to detect methods to ach...
http://www.fireeye.com/blog/threat-research/2021/04/abusing-replication-stealing-adfs-secrets-over-the-network.html
Published: 2021 04 27 17:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Organizations are increasingly adopting cloud-based services such as Microsoft 365 to host applications and data. Sophisticated threat actors are catching on and Mandiant has observed an increased focus on long-term persistent access to Microsoft 365 as one of their primary objectives. The focus on developing novel and hard to detect methods to ach...
http://www.fireeye.com/blog/threat-research/2021/04/abusing-replication-stealing-adfs-secrets-over-the-network.html
Published: 2021 04 27 17:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Abusing Replication: Stealing AD FS Secrets Over the Network - published over 5 years ago. Content: Organizations are increasingly adopting cloud-based services such as Microsoft 365 to host applications and data. Sophisticated threat actors are catching on and Mandiant has observed an increased focus on long-term persistent access to Microsoft 365 as one of their primary objectives. The focus on developing novel and hard to detect methods to ach... http://www.fireeye.com/blog/threat-research/2021/04/abusing-replication-stealing-adfs-secrets-over-the-network.html Published: 2021 04 27 17:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
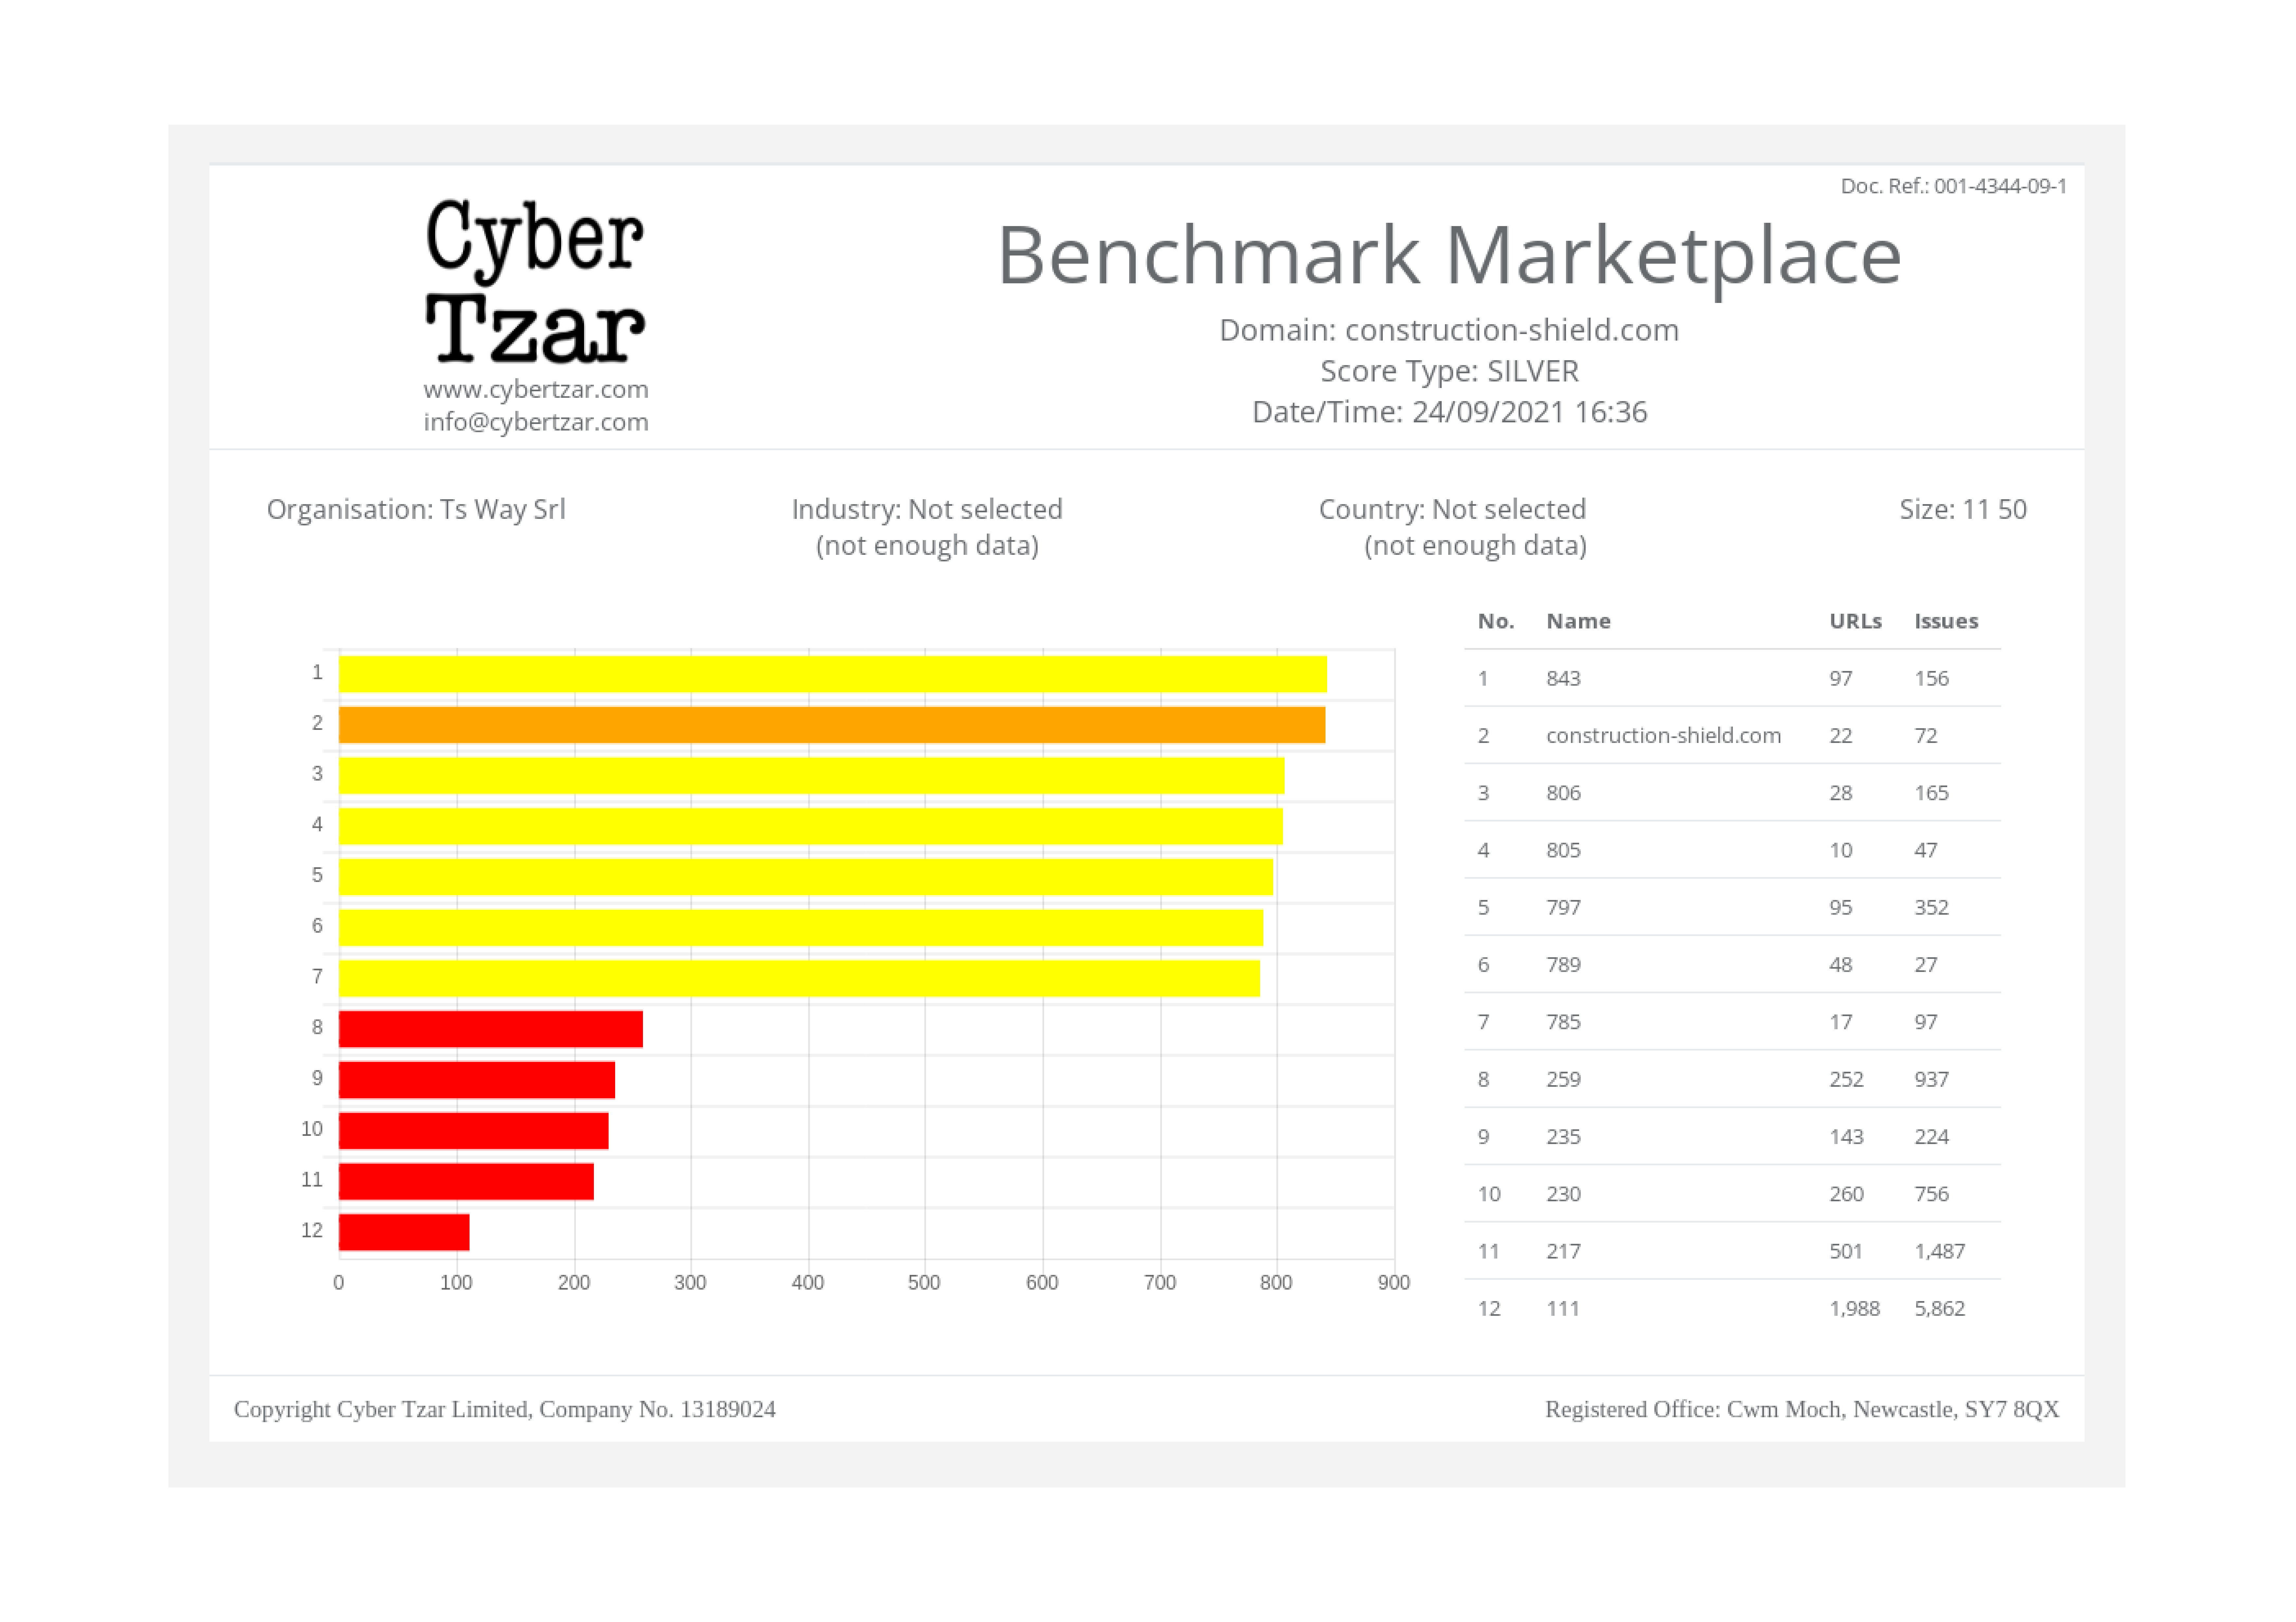
|
Article: Ghostwriter Update: Cyber Espionage Group UNC1151 Likely Conducts Ghostwriter Influence Activity - published over 5 years ago.
Content: In July 2020, Mandiant Threat Intelligence released a public report detailing an ongoing influence campaign we named “Ghostwriter.” Ghostwriter is a cyber-enabled influence campaign which primarily targets audiences in Lithuania, Latvia and Poland and promotes narratives critical of the North Atlantic Treaty Organization’s (NATO) presence in ...
http://www.fireeye.com/blog/threat-research/2021/04/espionage-group-unc1151-likely-conducts-ghostwriter-influence-activity.html
Published: 2021 04 28 10:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: In July 2020, Mandiant Threat Intelligence released a public report detailing an ongoing influence campaign we named “Ghostwriter.” Ghostwriter is a cyber-enabled influence campaign which primarily targets audiences in Lithuania, Latvia and Poland and promotes narratives critical of the North Atlantic Treaty Organization’s (NATO) presence in ...
http://www.fireeye.com/blog/threat-research/2021/04/espionage-group-unc1151-likely-conducts-ghostwriter-influence-activity.html
Published: 2021 04 28 10:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Ghostwriter Update: Cyber Espionage Group UNC1151 Likely Conducts Ghostwriter Influence Activity - published over 5 years ago. Content: In July 2020, Mandiant Threat Intelligence released a public report detailing an ongoing influence campaign we named “Ghostwriter.” Ghostwriter is a cyber-enabled influence campaign which primarily targets audiences in Lithuania, Latvia and Poland and promotes narratives critical of the North Atlantic Treaty Organization’s (NATO) presence in ... http://www.fireeye.com/blog/threat-research/2021/04/espionage-group-unc1151-likely-conducts-ghostwriter-influence-activity.html Published: 2021 04 28 10:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
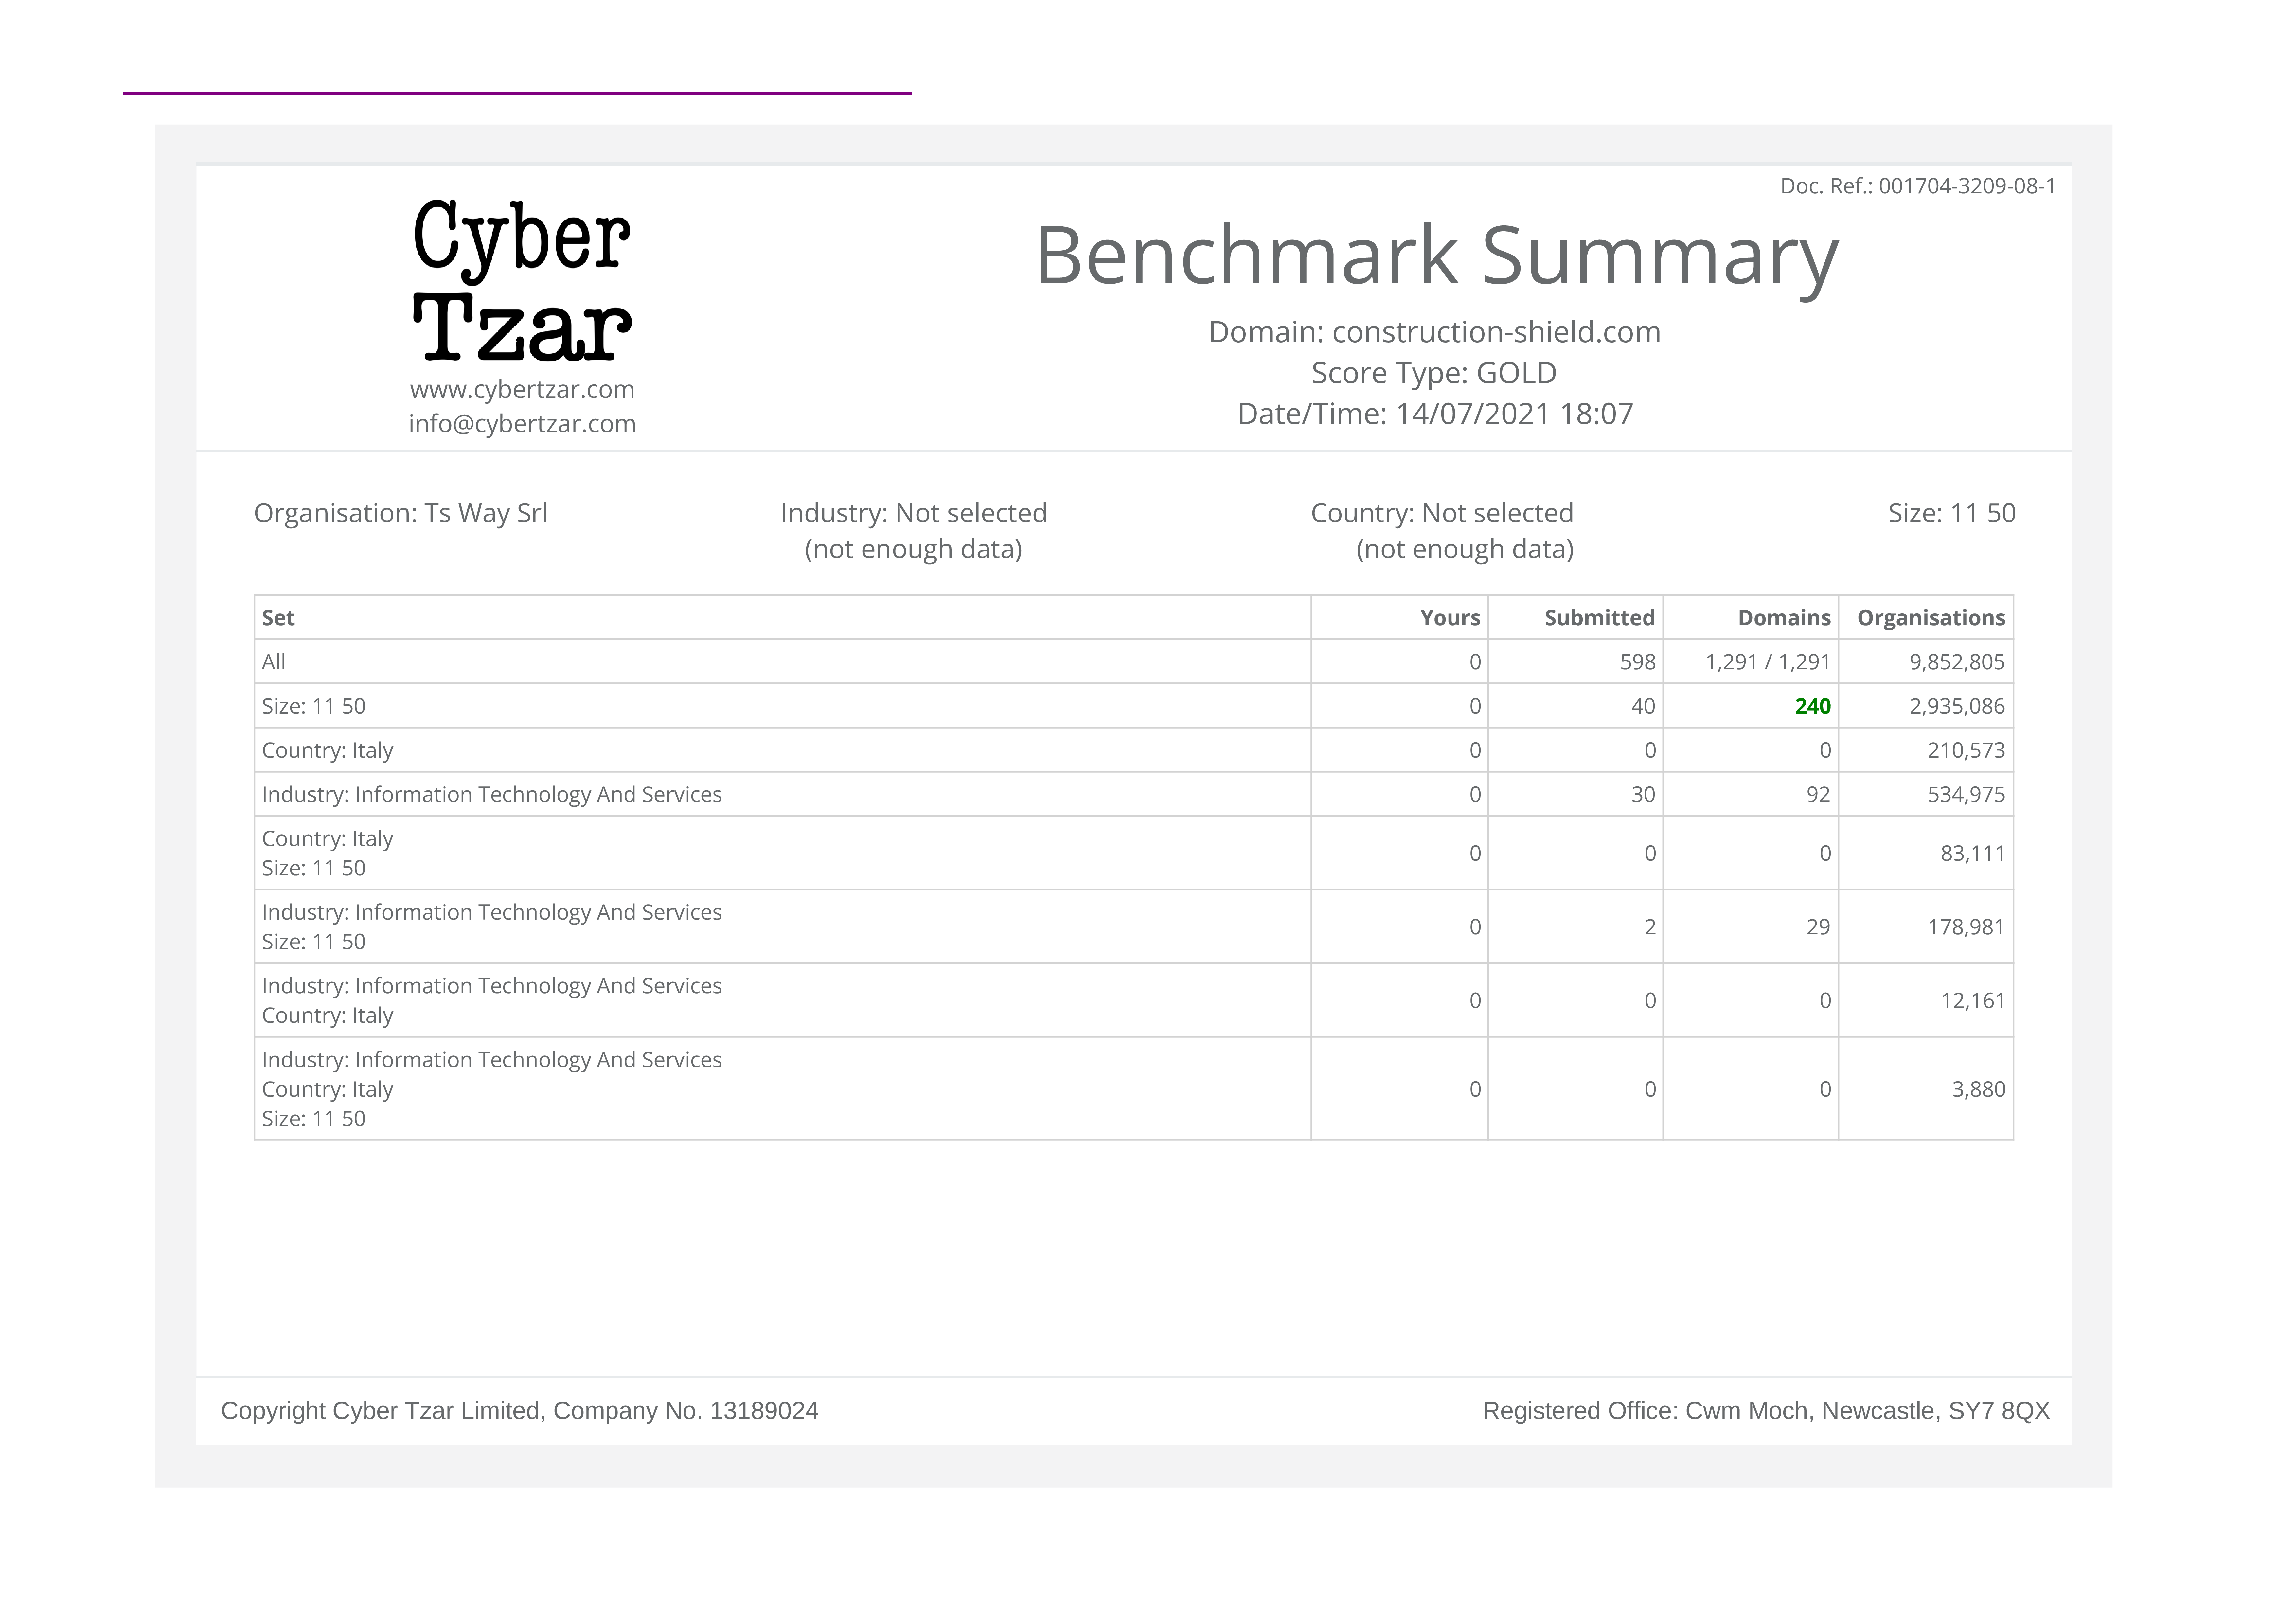
|
Article: Zero-Day Exploits in SonicWall Email Security Lead to Enterprise Compromise - published over 5 years ago.
Content: In March 2021, Mandiant Managed Defense identified three zero-day vulnerabilities in SonicWall’s Email Security (ES) product that were being exploited in the wild. These vulnerabilities were executed in conjunction to obtain administrative access and code execution on a SonicWall ES device. The adversary leveraged these vulnerabilities, with intima...
http://www.fireeye.com/blog/threat-research/2021/04/zero-day-exploits-in-sonicwall-email-security-lead-to-compromise.html
Published: 2021 04 20 21:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: In March 2021, Mandiant Managed Defense identified three zero-day vulnerabilities in SonicWall’s Email Security (ES) product that were being exploited in the wild. These vulnerabilities were executed in conjunction to obtain administrative access and code execution on a SonicWall ES device. The adversary leveraged these vulnerabilities, with intima...
http://www.fireeye.com/blog/threat-research/2021/04/zero-day-exploits-in-sonicwall-email-security-lead-to-compromise.html
Published: 2021 04 20 21:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Zero-Day Exploits in SonicWall Email Security Lead to Enterprise Compromise - published over 5 years ago. Content: In March 2021, Mandiant Managed Defense identified three zero-day vulnerabilities in SonicWall’s Email Security (ES) product that were being exploited in the wild. These vulnerabilities were executed in conjunction to obtain administrative access and code execution on a SonicWall ES device. The adversary leveraged these vulnerabilities, with intima... http://www.fireeye.com/blog/threat-research/2021/04/zero-day-exploits-in-sonicwall-email-security-lead-to-compromise.html Published: 2021 04 20 21:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: UNC2447 SOMBRAT and FIVEHANDS Ransomware: A Sophisticated Financial Threat - published over 5 years ago.
Content: Mandiant has observed an aggressive financially motivated group, UNC2447, exploiting one SonicWall VPN zero-day vulnerability prior to a patch being available and deploying sophisticated malware previously reported by other vendors as SOMBRAT. Mandiant has linked the use of SOMBRAT to the deployment of ransomware, which has not been previously repo...
http://www.fireeye.com/blog/threat-research/2021/04/unc2447-sombrat-and-fivehands-ransomware-sophisticated-financial-threat.html
Published: 2021 04 29 21:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Mandiant has observed an aggressive financially motivated group, UNC2447, exploiting one SonicWall VPN zero-day vulnerability prior to a patch being available and deploying sophisticated malware previously reported by other vendors as SOMBRAT. Mandiant has linked the use of SOMBRAT to the deployment of ransomware, which has not been previously repo...
http://www.fireeye.com/blog/threat-research/2021/04/unc2447-sombrat-and-fivehands-ransomware-sophisticated-financial-threat.html
Published: 2021 04 29 21:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: UNC2447 SOMBRAT and FIVEHANDS Ransomware: A Sophisticated Financial Threat - published over 5 years ago. Content: Mandiant has observed an aggressive financially motivated group, UNC2447, exploiting one SonicWall VPN zero-day vulnerability prior to a patch being available and deploying sophisticated malware previously reported by other vendors as SOMBRAT. Mandiant has linked the use of SOMBRAT to the deployment of ransomware, which has not been previously repo... http://www.fireeye.com/blog/threat-research/2021/04/unc2447-sombrat-and-fivehands-ransomware-sophisticated-financial-threat.html Published: 2021 04 29 21:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
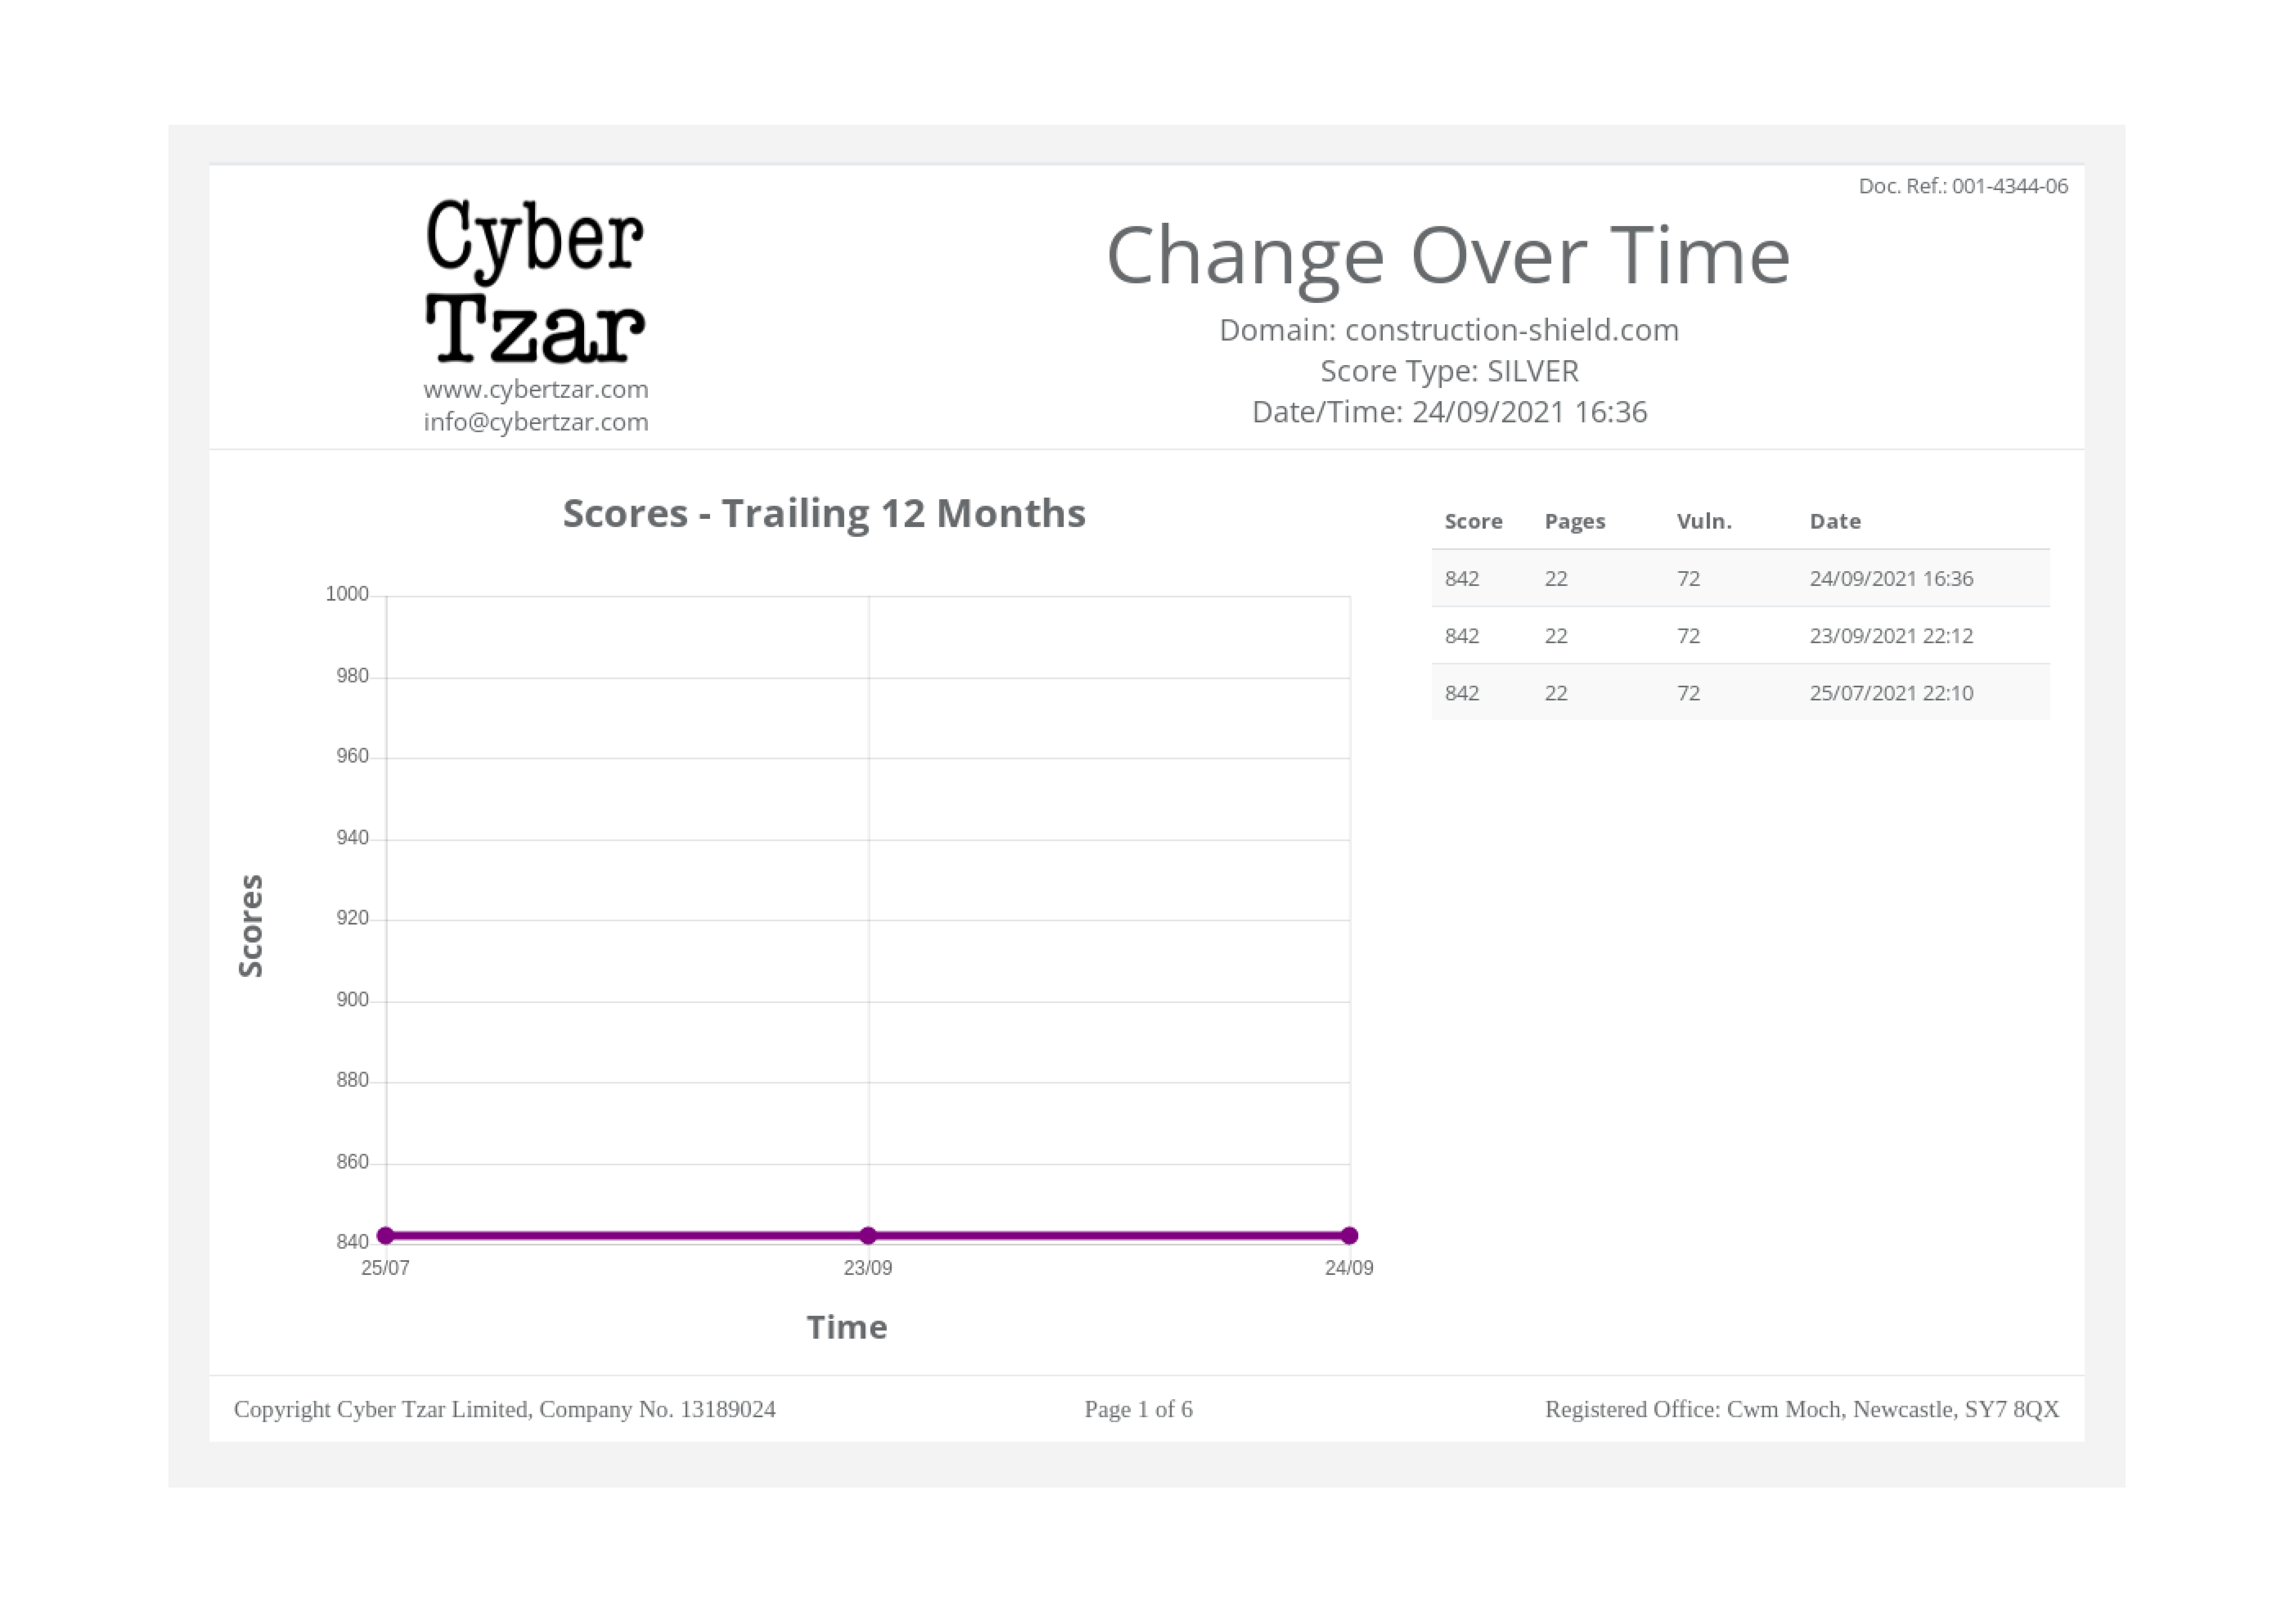
|
Article: The UNC2529 Triple Double: A Trifecta Phishing Campaign - published over 5 years ago.
Content: In December 2020, Mandiant observed a widespread, global phishing campaign targeting numerous organizations across an array of industries. Mandiant tracks this threat actor as UNC2529. Based on the considerable infrastructure employed, tailored phishing lures and the professionally coded sophistication of the malware, this threat actor appears expe...
http://www.fireeye.com/blog/threat-research/2021/05/unc2529-triple-double-trifecta-phishing-campaign.html
Published: 2021 05 04 14:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: In December 2020, Mandiant observed a widespread, global phishing campaign targeting numerous organizations across an array of industries. Mandiant tracks this threat actor as UNC2529. Based on the considerable infrastructure employed, tailored phishing lures and the professionally coded sophistication of the malware, this threat actor appears expe...
http://www.fireeye.com/blog/threat-research/2021/05/unc2529-triple-double-trifecta-phishing-campaign.html
Published: 2021 05 04 14:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: The UNC2529 Triple Double: A Trifecta Phishing Campaign - published over 5 years ago. Content: In December 2020, Mandiant observed a widespread, global phishing campaign targeting numerous organizations across an array of industries. Mandiant tracks this threat actor as UNC2529. Based on the considerable infrastructure employed, tailored phishing lures and the professionally coded sophistication of the malware, this threat actor appears expe... http://www.fireeye.com/blog/threat-research/2021/05/unc2529-triple-double-trifecta-phishing-campaign.html Published: 2021 05 04 14:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Check Your Pulse: Suspected APT Actors Leverage Authentication Bypass Techniques and Pulse Secure Zero-Day - published over 5 years ago.
Content: Executive Summary Mandiant recently responded to multiple security incidents involving compromises of Pulse Secure VPN appliances. This blog post examines multiple, related techniques for bypassing single and multifactor authentication on Pulse Secure VPN devices, persisting across upgrades, and maintaining access through webshells. The i...
http://www.fireeye.com/blog/threat-research/2021/04/suspected-apt-actors-leverage-bypass-techniques-pulse-secure-zero-day.html
Published: 2021 04 20 14:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Executive Summary Mandiant recently responded to multiple security incidents involving compromises of Pulse Secure VPN appliances. This blog post examines multiple, related techniques for bypassing single and multifactor authentication on Pulse Secure VPN devices, persisting across upgrades, and maintaining access through webshells. The i...
http://www.fireeye.com/blog/threat-research/2021/04/suspected-apt-actors-leverage-bypass-techniques-pulse-secure-zero-day.html
Published: 2021 04 20 14:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Check Your Pulse: Suspected APT Actors Leverage Authentication Bypass Techniques and Pulse Secure Zero-Day - published over 5 years ago. Content: Executive Summary Mandiant recently responded to multiple security incidents involving compromises of Pulse Secure VPN appliances. This blog post examines multiple, related techniques for bypassing single and multifactor authentication on Pulse Secure VPN devices, persisting across upgrades, and maintaining access through webshells. The i... http://www.fireeye.com/blog/threat-research/2021/04/suspected-apt-actors-leverage-bypass-techniques-pulse-secure-zero-day.html Published: 2021 04 20 14:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: Shining a Light on DARKSIDE Ransomware Operations - published over 5 years ago.
Content: Update (May 14): Mandiant has observed multiple actors cite a May 13 announcement that appeared to be shared with DARKSIDE RaaS affiliates by the operators of the service. This announcement stated that they lost access to their infrastructure, including their blog, payment, and CDN servers, and would be closing their service. Decrypter...
http://www.fireeye.com/blog/threat-research/2021/05/shining-a-light-on-darkside-ransomware-operations.html
Published: 2021 05 11 21:30:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Update (May 14): Mandiant has observed multiple actors cite a May 13 announcement that appeared to be shared with DARKSIDE RaaS affiliates by the operators of the service. This announcement stated that they lost access to their infrastructure, including their blog, payment, and CDN servers, and would be closing their service. Decrypter...
http://www.fireeye.com/blog/threat-research/2021/05/shining-a-light-on-darkside-ransomware-operations.html
Published: 2021 05 11 21:30:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Shining a Light on DARKSIDE Ransomware Operations - published over 5 years ago. Content: Update (May 14): Mandiant has observed multiple actors cite a May 13 announcement that appeared to be shared with DARKSIDE RaaS affiliates by the operators of the service. This announcement stated that they lost access to their infrastructure, including their blog, payment, and CDN servers, and would be closing their service. Decrypter... http://www.fireeye.com/blog/threat-research/2021/05/shining-a-light-on-darkside-ransomware-operations.html Published: 2021 05 11 21:30:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Crimes of Opportunity: Increasing Frequency of Low Sophistication Operational Technology Compromises - published over 5 years ago.
Content: Attacks on control processes supported by operational technology (OT) are often perceived as necessarily complex. This is because disrupting or modifying a control process to cause a predictable effect is often quite difficult and can require a lot of time and resources. However, Mandiant Threat Intelligence has observed simpler attacks, where acto...
http://www.fireeye.com/blog/threat-research/2021/05/increasing-low-sophistication-operational-technology-compromises.html
Published: 2021 05 25 14:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: Attacks on control processes supported by operational technology (OT) are often perceived as necessarily complex. This is because disrupting or modifying a control process to cause a predictable effect is often quite difficult and can require a lot of time and resources. However, Mandiant Threat Intelligence has observed simpler attacks, where acto...
http://www.fireeye.com/blog/threat-research/2021/05/increasing-low-sophistication-operational-technology-compromises.html
Published: 2021 05 25 14:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Crimes of Opportunity: Increasing Frequency of Low Sophistication Operational Technology Compromises - published over 5 years ago. Content: Attacks on control processes supported by operational technology (OT) are often perceived as necessarily complex. This is because disrupting or modifying a control process to cause a predictable effect is often quite difficult and can require a lot of time and resources. However, Mandiant Threat Intelligence has observed simpler attacks, where acto... http://www.fireeye.com/blog/threat-research/2021/05/increasing-low-sophistication-operational-technology-compromises.html Published: 2021 05 25 14:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Re-Checking Your Pulse: Updates on Chinese APT Actors Compromising Pulse Secure VPN Devices - published over 5 years ago.
Content: On April 20, 2021, Mandiant published detailed results of our investigations into compromised Pulse Secure devices by suspected Chinese espionage operators. This blog post is intended to provide an update on our findings, give additional recommendations to network defenders, and discuss potential implications for U.S.-China strategic relations. ...
http://www.fireeye.com/blog/threat-research/2021/05/updates-on-chinese-apt-compromising-pulse-secure-vpn-devices.html
Published: 2021 05 27 17:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
Content: On April 20, 2021, Mandiant published detailed results of our investigations into compromised Pulse Secure devices by suspected Chinese espionage operators. This blog post is intended to provide an update on our findings, give additional recommendations to network defenders, and discuss potential implications for U.S.-China strategic relations. ...
http://www.fireeye.com/blog/threat-research/2021/05/updates-on-chinese-apt-compromising-pulse-secure-vpn-devices.html
Published: 2021 05 27 17:00:00
Received: 2021 06 06 09:05:11
Feed: FireEye Blog
Source: FireEye Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Re-Checking Your Pulse: Updates on Chinese APT Actors Compromising Pulse Secure VPN Devices - published over 5 years ago. Content: On April 20, 2021, Mandiant published detailed results of our investigations into compromised Pulse Secure devices by suspected Chinese espionage operators. This blog post is intended to provide an update on our findings, give additional recommendations to network defenders, and discuss potential implications for U.S.-China strategic relations. ... http://www.fireeye.com/blog/threat-research/2021/05/updates-on-chinese-apt-compromising-pulse-secure-vpn-devices.html Published: 2021 05 27 17:00:00 Received: 2021 06 06 09:05:11 Feed: FireEye Blog Source: FireEye Blog Category: Cyber Security Topic: Cyber Security |
Article: Posh-Sysmon Module for Creating Sysmon Configuration Files - published over 9 years ago.
Content: Why a PowerShell ModuleSysmon configuration can be complex in addition to hard to maintain by hand. For this purpose I created a module called Posh-Sysmon some time ago to aid in the creation and maintenance of configuration files. The module was initially written after the release of version 2.0 and has been maintained and expanded as new version have been ...
https://www.darkoperator.com/blog/2017/2/17/posh-sysmon-powershell-module-for-creating-sysmon-configuration-files
Published: 2017 02 20 11:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: Why a PowerShell ModuleSysmon configuration can be complex in addition to hard to maintain by hand. For this purpose I created a module called Posh-Sysmon some time ago to aid in the creation and maintenance of configuration files. The module was initially written after the release of version 2.0 and has been maintained and expanded as new version have been ...
https://www.darkoperator.com/blog/2017/2/17/posh-sysmon-powershell-module-for-creating-sysmon-configuration-files
Published: 2017 02 20 11:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Posh-Sysmon Module for Creating Sysmon Configuration Files - published over 9 years ago. Content: Why a PowerShell ModuleSysmon configuration can be complex in addition to hard to maintain by hand. For this purpose I created a module called Posh-Sysmon some time ago to aid in the creation and maintenance of configuration files. The module was initially written after the release of version 2.0 and has been maintained and expanded as new version have been ... https://www.darkoperator.com/blog/2017/2/17/posh-sysmon-powershell-module-for-creating-sysmon-configuration-files Published: 2017 02 20 11:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Home Lab - VPN - published over 9 years ago.
Content: Since our lab is isolated from the home network behind the router we need a way to access the VM's inside from our research systems. To access the systems behind the router we can use a VPN. With VyOS we have 2 options:L2TP/IPSec - Native support on Windows and OS X. Linux client support can be tricky.OpenVPN - Requires third party client installed, works we...
https://www.darkoperator.com/blog/2017/2/5/home-lab-vpn
Published: 2017 03 09 11:50:29
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: Since our lab is isolated from the home network behind the router we need a way to access the VM's inside from our research systems. To access the systems behind the router we can use a VPN. With VyOS we have 2 options:L2TP/IPSec - Native support on Windows and OS X. Linux client support can be tricky.OpenVPN - Requires third party client installed, works we...
https://www.darkoperator.com/blog/2017/2/5/home-lab-vpn
Published: 2017 03 09 11:50:29
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Home Lab - VPN - published over 9 years ago. Content: Since our lab is isolated from the home network behind the router we need a way to access the VM's inside from our research systems. To access the systems behind the router we can use a VPN. With VyOS we have 2 options:L2TP/IPSec - Native support on Windows and OS X. Linux client support can be tricky.OpenVPN - Requires third party client installed, works we... https://www.darkoperator.com/blog/2017/2/5/home-lab-vpn Published: 2017 03 09 11:50:29 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
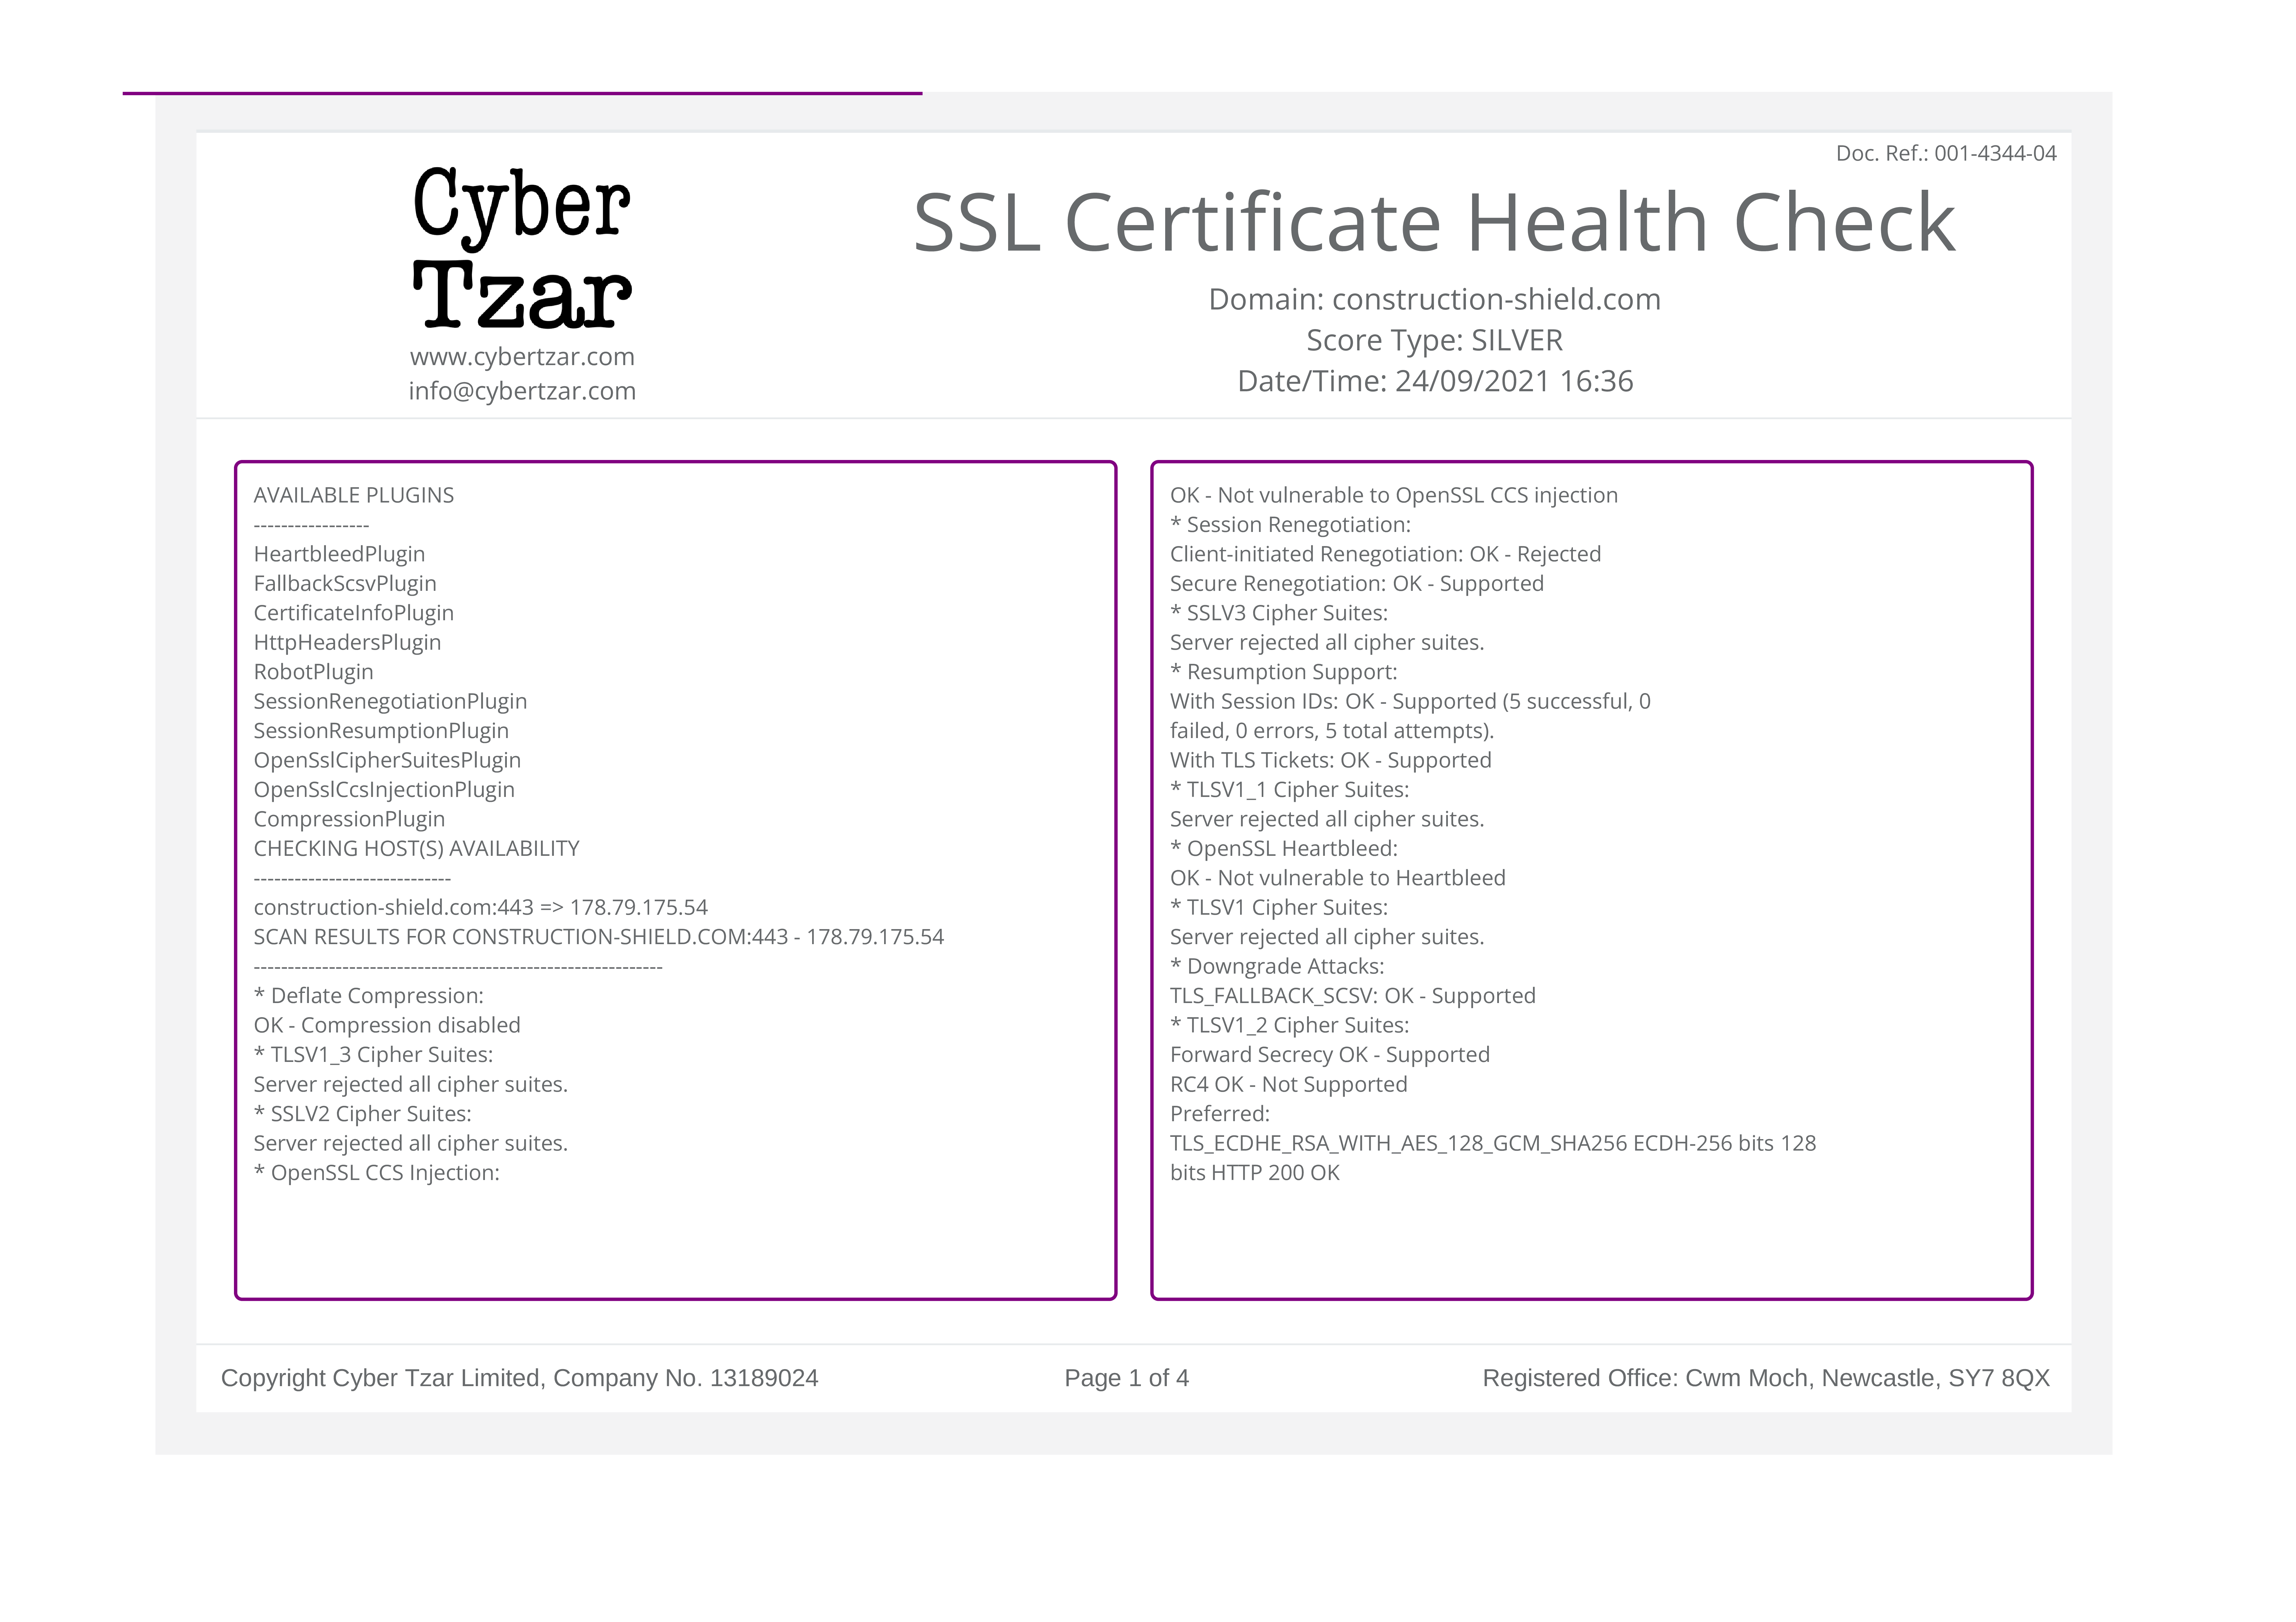
|
Article: How Much Your Org Reaction to a Tweet Says? - published over 9 years ago.
Content: Recently Tavis Ormandy a well known vulnerability researcher from Google made a tweet about a vulnerability he and researcher Natalie Silvanovich from Google Project Zero found on the Windows OS that could be wormable. ...
https://www.darkoperator.com/blog/2017/5/7/how-much-your-org-reaction-to-a-tweet-says
Published: 2017 05 07 21:51:27
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: Recently Tavis Ormandy a well known vulnerability researcher from Google made a tweet about a vulnerability he and researcher Natalie Silvanovich from Google Project Zero found on the Windows OS that could be wormable. ...
https://www.darkoperator.com/blog/2017/5/7/how-much-your-org-reaction-to-a-tweet-says
Published: 2017 05 07 21:51:27
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: How Much Your Org Reaction to a Tweet Says? - published over 9 years ago. Content: Recently Tavis Ormandy a well known vulnerability researcher from Google made a tweet about a vulnerability he and researcher Natalie Silvanovich from Google Project Zero found on the Windows OS that could be wormable. ... https://www.darkoperator.com/blog/2017/5/7/how-much-your-org-reaction-to-a-tweet-says Published: 2017 05 07 21:51:27 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
Article: WanaCry Shows a Operational and Human Problem - published over 9 years ago.
Content: This last couple of day the headline has been the WannaCry ransomeware worm. I have seen many discussion about the technical aspects of it, about the disclosure of the vulnerability and debates of who is at fault for its widespread effect (Microsoft, NSA, Shadow Brokers ..etc). Yet the big elephant in the room remains that this is history that will repeat it...
https://www.darkoperator.com/blog/2017/5/14/wanacry-a-operational-and-business-problem
Published: 2017 05 15 01:53:31
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: This last couple of day the headline has been the WannaCry ransomeware worm. I have seen many discussion about the technical aspects of it, about the disclosure of the vulnerability and debates of who is at fault for its widespread effect (Microsoft, NSA, Shadow Brokers ..etc). Yet the big elephant in the room remains that this is history that will repeat it...
https://www.darkoperator.com/blog/2017/5/14/wanacry-a-operational-and-business-problem
Published: 2017 05 15 01:53:31
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: WanaCry Shows a Operational and Human Problem - published over 9 years ago. Content: This last couple of day the headline has been the WannaCry ransomeware worm. I have seen many discussion about the technical aspects of it, about the disclosure of the vulnerability and debates of who is at fault for its widespread effect (Microsoft, NSA, Shadow Brokers ..etc). Yet the big elephant in the room remains that this is history that will repeat it... https://www.darkoperator.com/blog/2017/5/14/wanacry-a-operational-and-business-problem Published: 2017 05 15 01:53:31 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
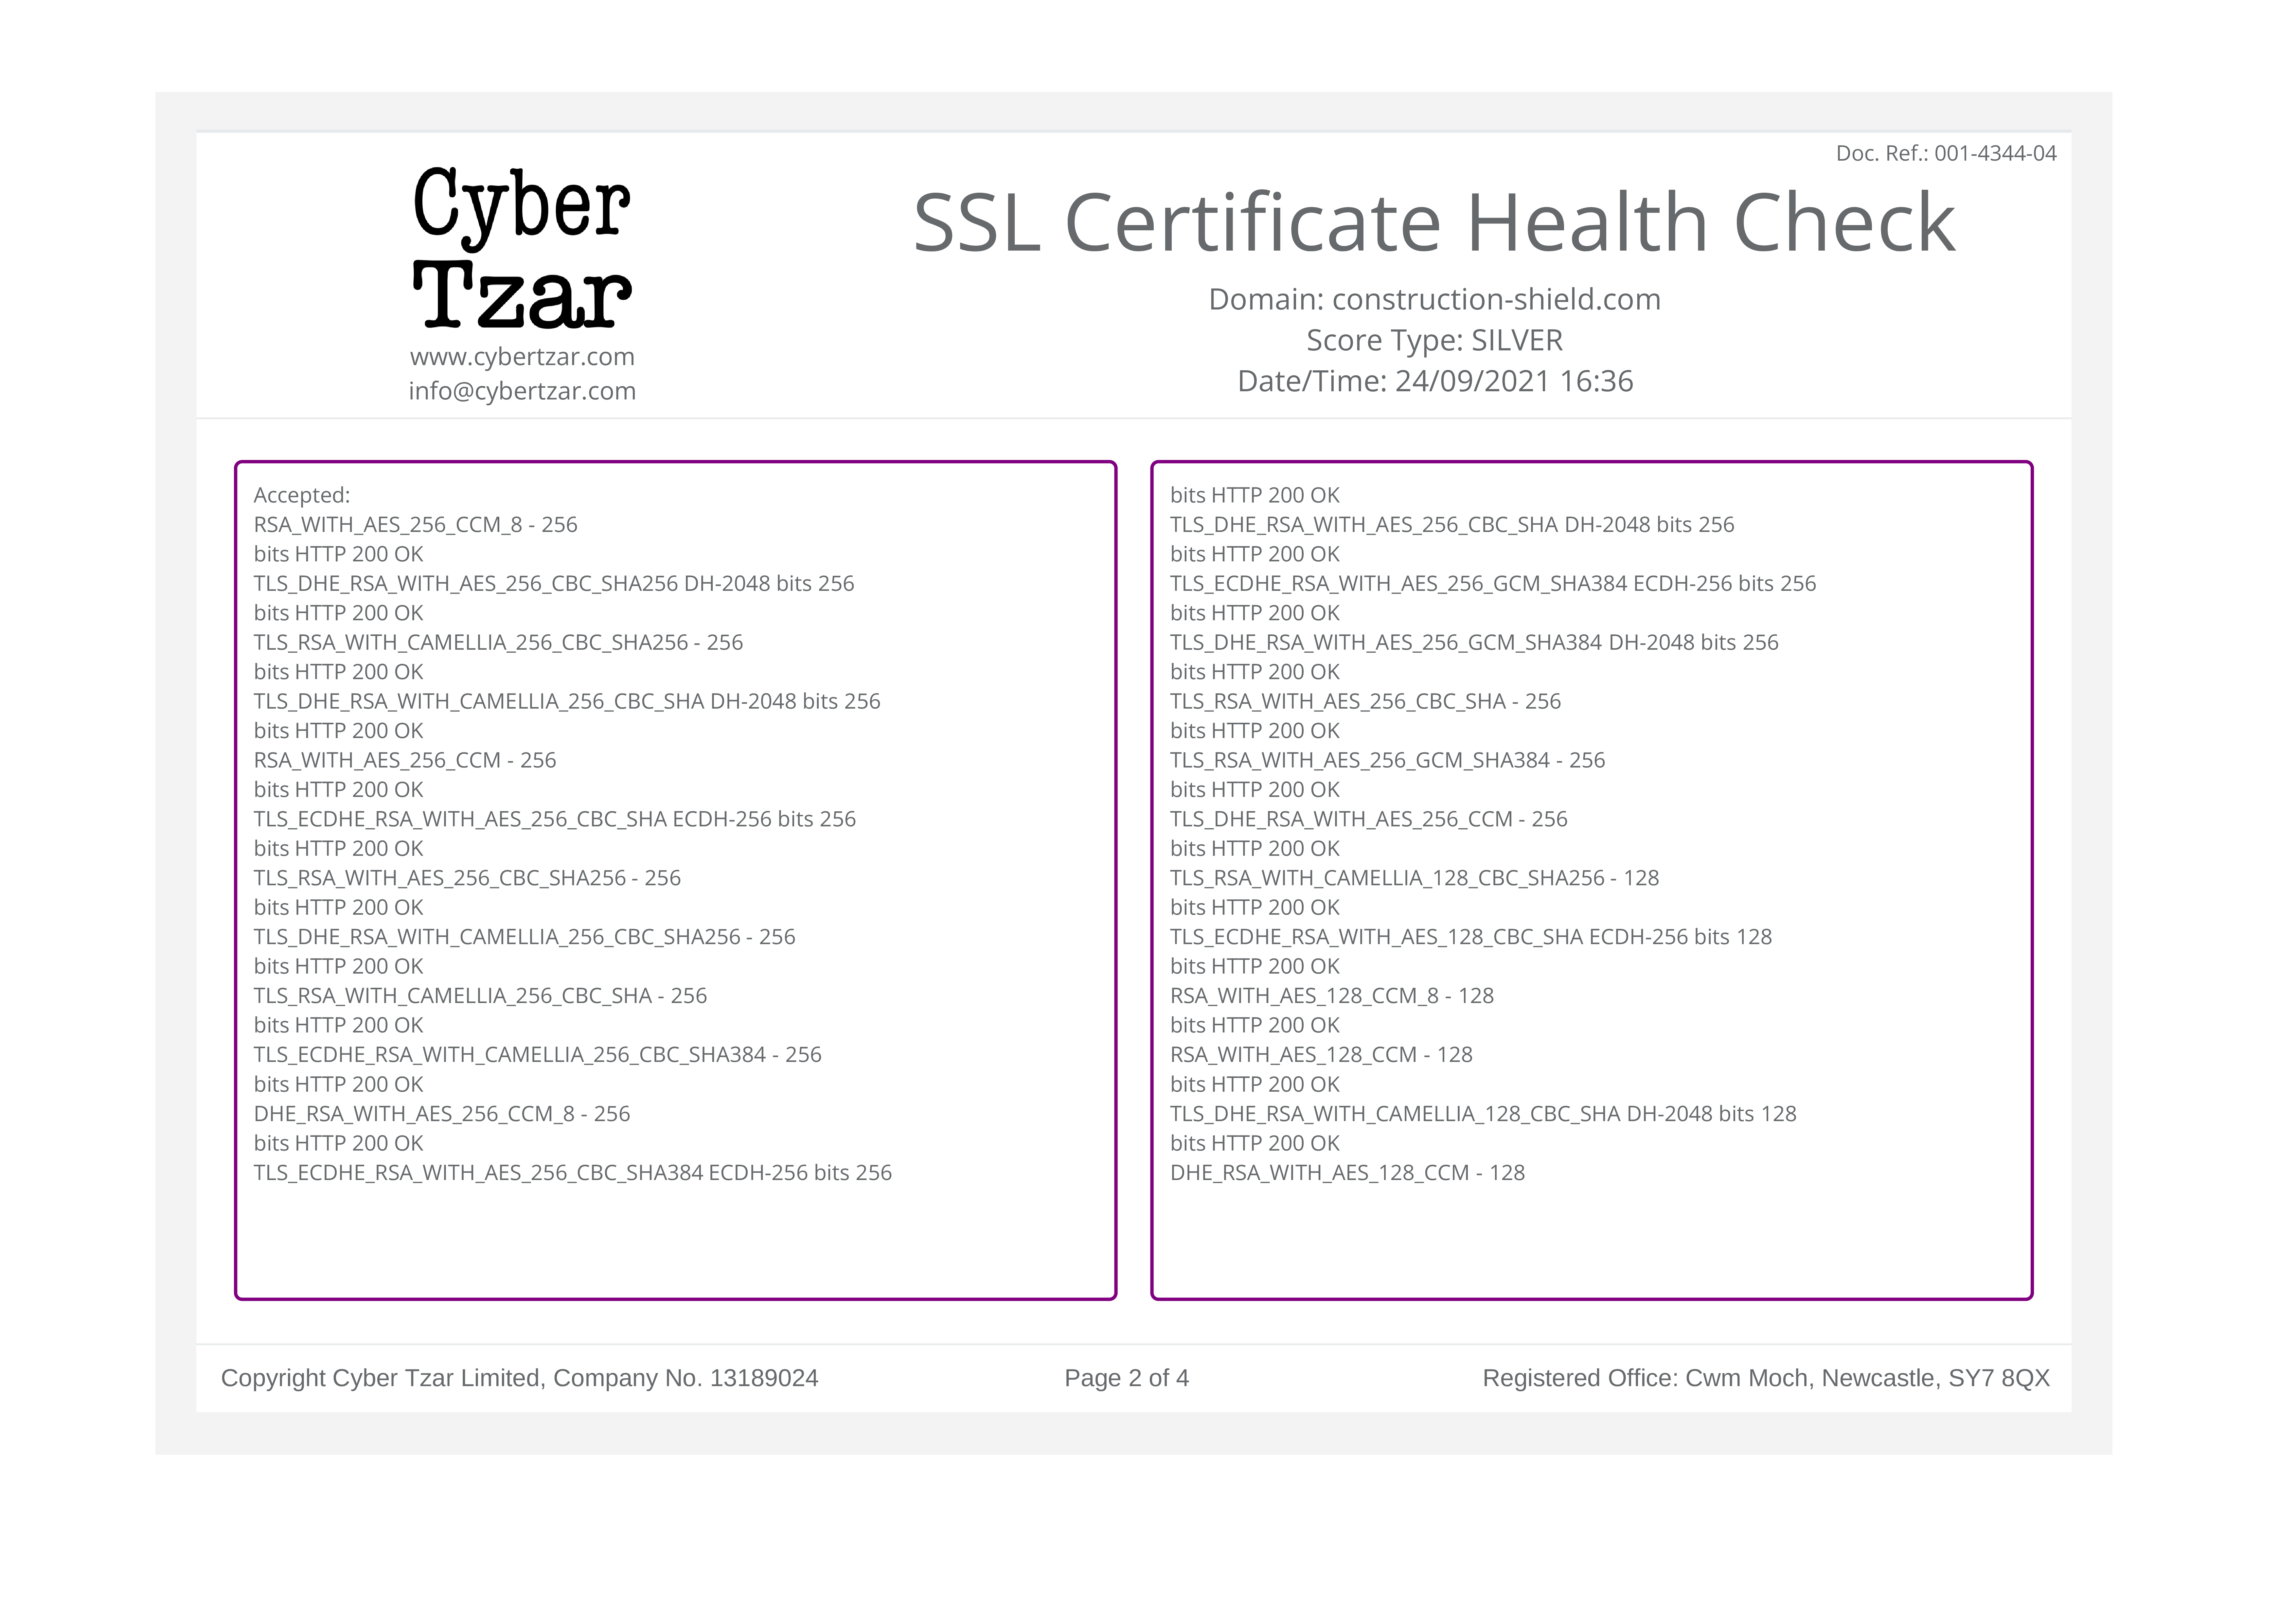
|
Article: Basics of Tracking WMI Activity - published about 9 years ago.
Content: WMI (Windows Management Instrumentation) has been part of the Windows Operating System since since Windows 2000 when it was included in the OS. The technology has been of great value to system administrators by providing ways to pull all types of information, configure components and take action based on state of several components of the OS. Due to this fle...
https://www.darkoperator.com/blog/2017/10/14/basics-of-tracking-wmi-activity
Published: 2017 10 16 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: WMI (Windows Management Instrumentation) has been part of the Windows Operating System since since Windows 2000 when it was included in the OS. The technology has been of great value to system administrators by providing ways to pull all types of information, configure components and take action based on state of several components of the OS. Due to this fle...
https://www.darkoperator.com/blog/2017/10/14/basics-of-tracking-wmi-activity
Published: 2017 10 16 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Basics of Tracking WMI Activity - published about 9 years ago. Content: WMI (Windows Management Instrumentation) has been part of the Windows Operating System since since Windows 2000 when it was included in the OS. The technology has been of great value to system administrators by providing ways to pull all types of information, configure components and take action based on state of several components of the OS. Due to this fle... https://www.darkoperator.com/blog/2017/10/14/basics-of-tracking-wmi-activity Published: 2017 10 16 12:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
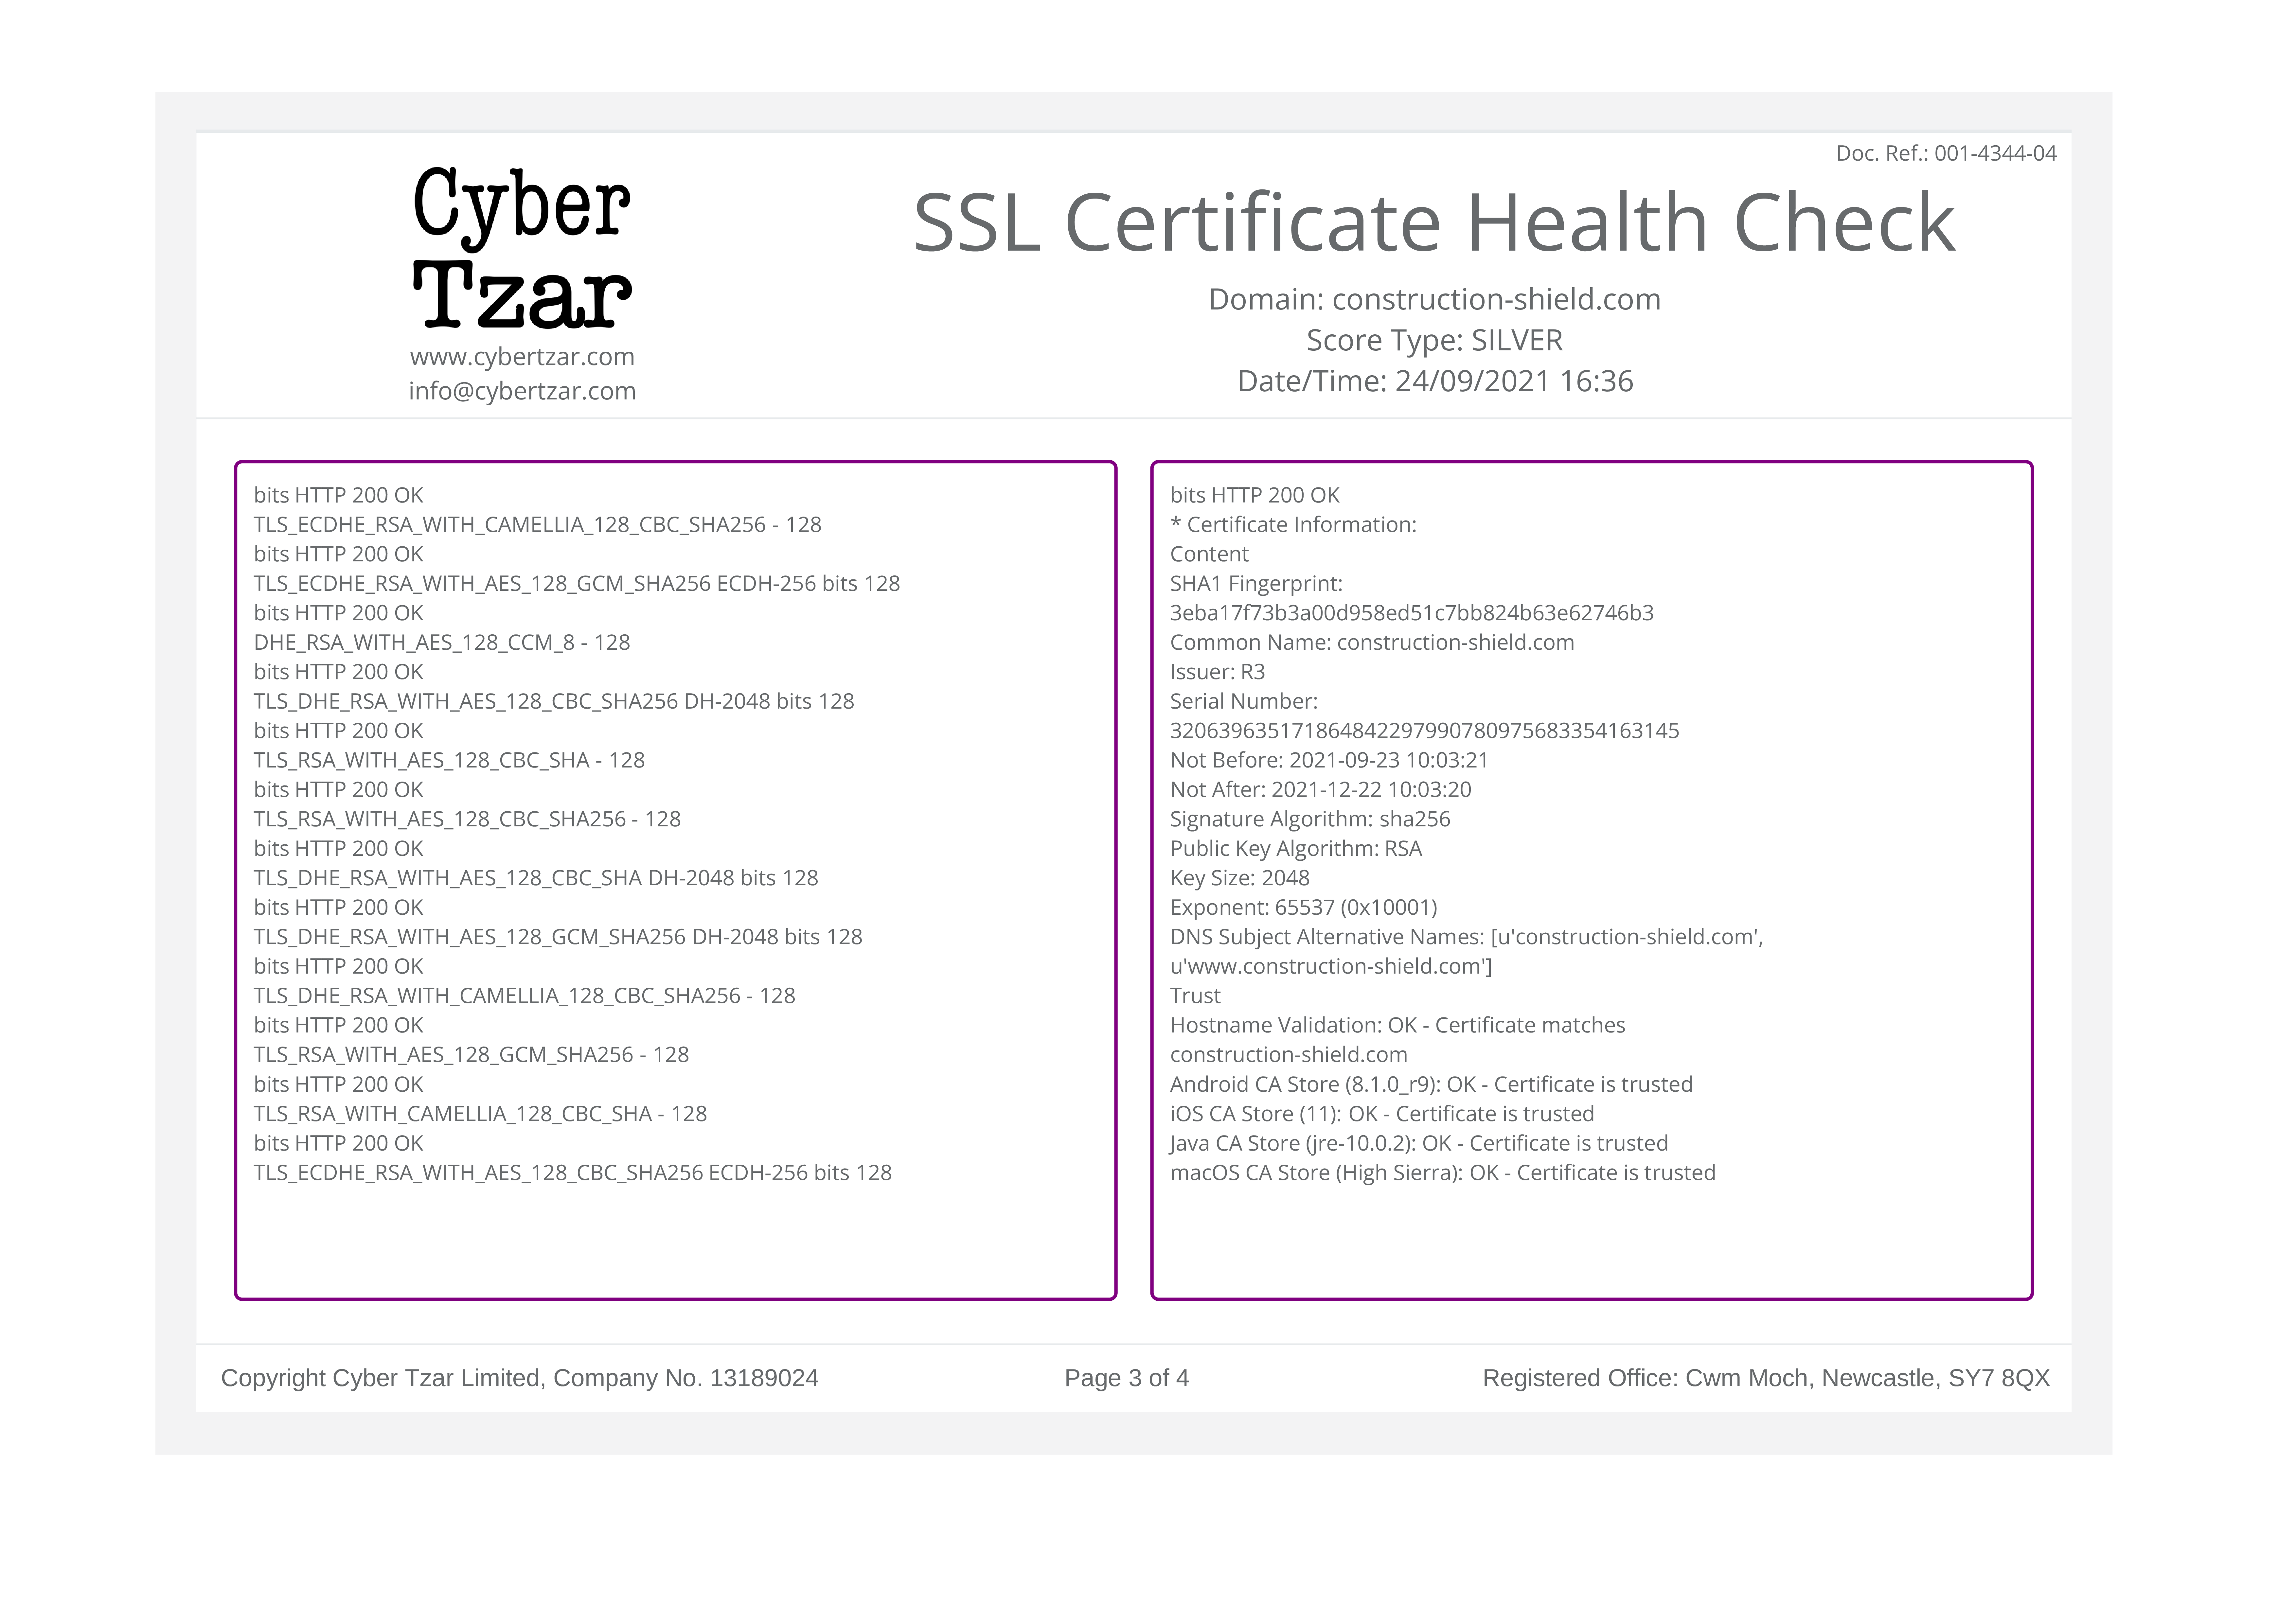
|
Article: Sysinternals Sysmon 6.10 Tracking of Permanent WMI Events - published about 9 years ago.
Content: In my previous blog post I covered how Microsoft has enhanced WMI logging in the latest versions of their client and server operating systems. WMI Permanent event logging was also added in version 6.10 specific events for logging permanent event actions. The new events are:Event ID 19: WmiEvent (WmiEventFilter activity detected). When a WMI event filter is r...
https://www.darkoperator.com/blog/2017/10/15/sysinternals-sysmon-610-tracking-of-permanent-wmi-events
Published: 2017 10 18 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: In my previous blog post I covered how Microsoft has enhanced WMI logging in the latest versions of their client and server operating systems. WMI Permanent event logging was also added in version 6.10 specific events for logging permanent event actions. The new events are:Event ID 19: WmiEvent (WmiEventFilter activity detected). When a WMI event filter is r...
https://www.darkoperator.com/blog/2017/10/15/sysinternals-sysmon-610-tracking-of-permanent-wmi-events
Published: 2017 10 18 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Sysinternals Sysmon 6.10 Tracking of Permanent WMI Events - published about 9 years ago. Content: In my previous blog post I covered how Microsoft has enhanced WMI logging in the latest versions of their client and server operating systems. WMI Permanent event logging was also added in version 6.10 specific events for logging permanent event actions. The new events are:Event ID 19: WmiEvent (WmiEventFilter activity detected). When a WMI event filter is r... https://www.darkoperator.com/blog/2017/10/15/sysinternals-sysmon-610-tracking-of-permanent-wmi-events Published: 2017 10 18 12:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
Article: Update to Pentest Metasploit Plugin - published about 9 years ago.
Content: I recently update my Metasploit Pentest Plugin . I added 2 new commands to the plugin and fixed issues when printing information as a table. The update are small ones.Lets take a look at the changes for the plugin. We can start by loading the plugin in a Metasploit Framework session.msf > load pentest ___ _ _ ___ _ ...
https://www.darkoperator.com/blog/2017/10/17/update-to-pentest-metasploit-plugin
Published: 2017 10 19 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: I recently update my Metasploit Pentest Plugin . I added 2 new commands to the plugin and fixed issues when printing information as a table. The update are small ones.Lets take a look at the changes for the plugin. We can start by loading the plugin in a Metasploit Framework session.msf > load pentest ___ _ _ ___ _ ...
https://www.darkoperator.com/blog/2017/10/17/update-to-pentest-metasploit-plugin
Published: 2017 10 19 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Update to Pentest Metasploit Plugin - published about 9 years ago. Content: I recently update my Metasploit Pentest Plugin . I added 2 new commands to the plugin and fixed issues when printing information as a table. The update are small ones.Lets take a look at the changes for the plugin. We can start by loading the plugin in a Metasploit Framework session.msf > load pentest ___ _ _ ___ _ ... https://www.darkoperator.com/blog/2017/10/17/update-to-pentest-metasploit-plugin Published: 2017 10 19 12:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
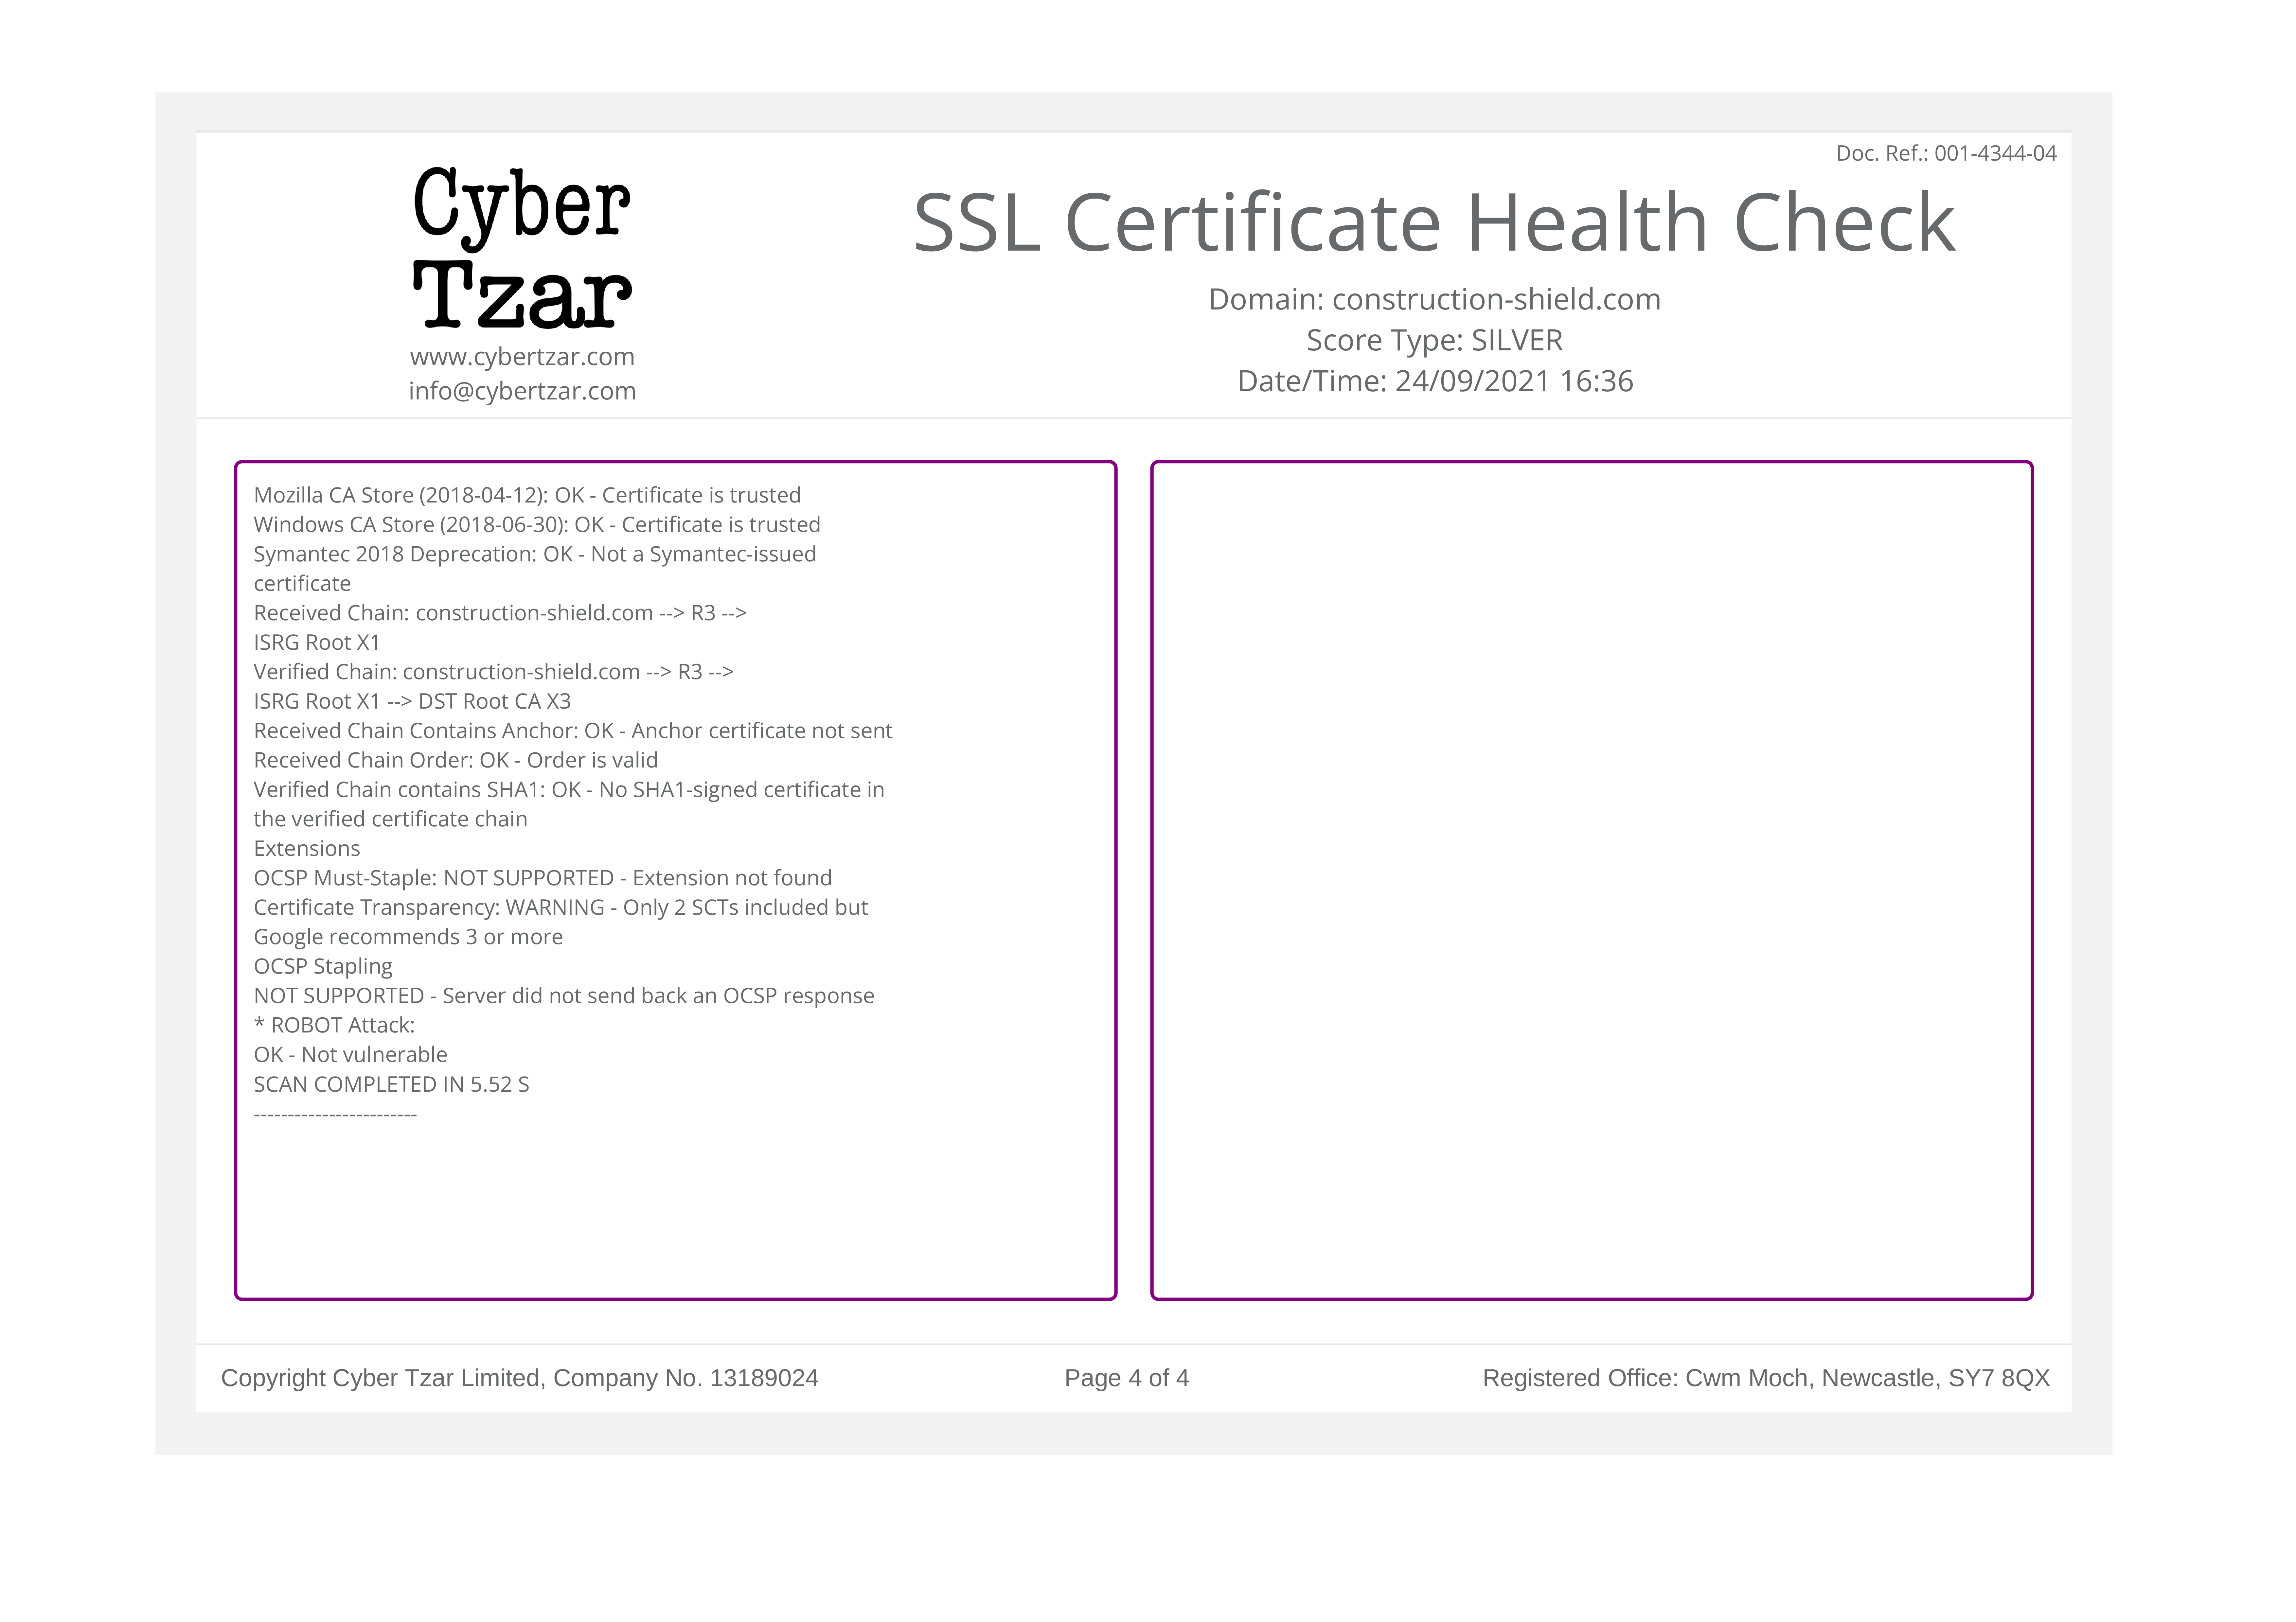
|
Article: Basics of The Metasploit Framework API - IRB Setup - published about 9 years ago.
Content: Those of you who have taken my "Automating Metasploit Framework" class all this material should not be new. I have decided to start making a large portion of the class available here in the blog as a series. On this post I will cover the basics of setting up IRB so we can start exploring in a general sense the Metasploit Framework API. The API is extensive a...
https://www.darkoperator.com/blog/2017/10/21/basics-of-the-metasploit-framework-irb-setup
Published: 2017 10 23 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: Those of you who have taken my "Automating Metasploit Framework" class all this material should not be new. I have decided to start making a large portion of the class available here in the blog as a series. On this post I will cover the basics of setting up IRB so we can start exploring in a general sense the Metasploit Framework API. The API is extensive a...
https://www.darkoperator.com/blog/2017/10/21/basics-of-the-metasploit-framework-irb-setup
Published: 2017 10 23 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Basics of The Metasploit Framework API - IRB Setup - published about 9 years ago. Content: Those of you who have taken my "Automating Metasploit Framework" class all this material should not be new. I have decided to start making a large portion of the class available here in the blog as a series. On this post I will cover the basics of setting up IRB so we can start exploring in a general sense the Metasploit Framework API. The API is extensive a... https://www.darkoperator.com/blog/2017/10/21/basics-of-the-metasploit-framework-irb-setup Published: 2017 10 23 12:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Switching Ruby Version in RVM for Metasploit Development - published about 9 years ago.
Content: If you have setup a development environment with RVM to do development in Metasploit Framework you are bound to encounter that the Metasploit team has changed preferred Ruby versions.carlos@ubuntu:/opt$ cd metasploit-framework/ ruby-2.4.2 is not installed. To install do: 'rvm install ruby-2.4.2' You get a useful message that mentions the RVM command you need...
https://www.darkoperator.com/blog/2017/10/22/switching-ruby-version-in-rvm-for-metasploit-development
Published: 2017 10 25 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: If you have setup a development environment with RVM to do development in Metasploit Framework you are bound to encounter that the Metasploit team has changed preferred Ruby versions.carlos@ubuntu:/opt$ cd metasploit-framework/ ruby-2.4.2 is not installed. To install do: 'rvm install ruby-2.4.2' You get a useful message that mentions the RVM command you need...
https://www.darkoperator.com/blog/2017/10/22/switching-ruby-version-in-rvm-for-metasploit-development
Published: 2017 10 25 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Switching Ruby Version in RVM for Metasploit Development - published about 9 years ago. Content: If you have setup a development environment with RVM to do development in Metasploit Framework you are bound to encounter that the Metasploit team has changed preferred Ruby versions.carlos@ubuntu:/opt$ cd metasploit-framework/ ruby-2.4.2 is not installed. To install do: 'rvm install ruby-2.4.2' You get a useful message that mentions the RVM command you need... https://www.darkoperator.com/blog/2017/10/22/switching-ruby-version-in-rvm-for-metasploit-development Published: 2017 10 25 12:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
Article: Windows Defender Exploit Guard ASR VBScript/JS Rule - published about 9 years ago.
Content: Microsoft has been adding to Windows 10 the features of the Enhanced Mitigation Experience Toolkit (EMET) in to the OS. On the 1709 release they added more features and expanded on them as part of Windows Defender Exploit Guard One of the features of great interest for me is Attack Surface Reduction. I have used this feature in EMET with great success as a m...
https://www.darkoperator.com/blog/2017/11/6/windows-defender-exploit-guard-asr-vbscriptjs-rule
Published: 2017 11 07 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: Microsoft has been adding to Windows 10 the features of the Enhanced Mitigation Experience Toolkit (EMET) in to the OS. On the 1709 release they added more features and expanded on them as part of Windows Defender Exploit Guard One of the features of great interest for me is Attack Surface Reduction. I have used this feature in EMET with great success as a m...
https://www.darkoperator.com/blog/2017/11/6/windows-defender-exploit-guard-asr-vbscriptjs-rule
Published: 2017 11 07 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Windows Defender Exploit Guard ASR VBScript/JS Rule - published about 9 years ago. Content: Microsoft has been adding to Windows 10 the features of the Enhanced Mitigation Experience Toolkit (EMET) in to the OS. On the 1709 release they added more features and expanded on them as part of Windows Defender Exploit Guard One of the features of great interest for me is Attack Surface Reduction. I have used this feature in EMET with great success as a m... https://www.darkoperator.com/blog/2017/11/6/windows-defender-exploit-guard-asr-vbscriptjs-rule Published: 2017 11 07 12:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Windows Defender Exploit Guard ASR Obfuscated Script Rule - published about 9 years ago.
Content: On this blog post I will cover my testing of the Attack Surface Reduction rule for Potentially Obfuscated Scripts. This is one of the features that intrigued me the most. One obfuscates the scripts for several reasons:Bypass detection controls like AV, automatic log analysis and other controls. Hinder analysis of the script to determine its purpose and actio...
https://www.darkoperator.com/blog/2017/11/8/windows-defender-exploit-guard-asr-obfuscated-script-rule
Published: 2017 11 08 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: On this blog post I will cover my testing of the Attack Surface Reduction rule for Potentially Obfuscated Scripts. This is one of the features that intrigued me the most. One obfuscates the scripts for several reasons:Bypass detection controls like AV, automatic log analysis and other controls. Hinder analysis of the script to determine its purpose and actio...
https://www.darkoperator.com/blog/2017/11/8/windows-defender-exploit-guard-asr-obfuscated-script-rule
Published: 2017 11 08 12:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Windows Defender Exploit Guard ASR Obfuscated Script Rule - published about 9 years ago. Content: On this blog post I will cover my testing of the Attack Surface Reduction rule for Potentially Obfuscated Scripts. This is one of the features that intrigued me the most. One obfuscates the scripts for several reasons:Bypass detection controls like AV, automatic log analysis and other controls. Hinder analysis of the script to determine its purpose and actio... https://www.darkoperator.com/blog/2017/11/8/windows-defender-exploit-guard-asr-obfuscated-script-rule Published: 2017 11 08 12:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Windows Defender Exploit Guard ASR Rules for Office - published almost 9 years ago.
Content: On this blog post I continue looking at the ASR rules, this time I'm looking at the ASR rules for Office. The ASR rules for office are:Block Office applications from creating child processesBlock Office applications from creating executable contentBlock Office applications from injecting code into other processesBlock Win32 API calls from Office macroThese ...
https://www.darkoperator.com/blog/2017/11/11/windows-defender-exploit-guard-asr-rules-for-office
Published: 2017 11 14 11:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: On this blog post I continue looking at the ASR rules, this time I'm looking at the ASR rules for Office. The ASR rules for office are:Block Office applications from creating child processesBlock Office applications from creating executable contentBlock Office applications from injecting code into other processesBlock Win32 API calls from Office macroThese ...
https://www.darkoperator.com/blog/2017/11/11/windows-defender-exploit-guard-asr-rules-for-office
Published: 2017 11 14 11:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Windows Defender Exploit Guard ASR Rules for Office - published almost 9 years ago. Content: On this blog post I continue looking at the ASR rules, this time I'm looking at the ASR rules for Office. The ASR rules for office are:Block Office applications from creating child processesBlock Office applications from creating executable contentBlock Office applications from injecting code into other processesBlock Win32 API calls from Office macroThese ... https://www.darkoperator.com/blog/2017/11/11/windows-defender-exploit-guard-asr-rules-for-office Published: 2017 11 14 11:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
Article: Some Comments and Thoughts on Tradecraft - published almost 9 years ago.
Content: I have been writing a series on the new Windows Defender Exploit Guard features on Attack Surface Reduction where I cover my research on it. I'm researching the controls to add the information in to my personal playbook. Surprisingly in conversations with some Red Teamers I know they dismissed the information as it is a Blue/Defense technology. These comment...
https://www.darkoperator.com/blog/2017/11/20/some-comments-and-thoughts-on-tradecraft
Published: 2017 11 20 11:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: I have been writing a series on the new Windows Defender Exploit Guard features on Attack Surface Reduction where I cover my research on it. I'm researching the controls to add the information in to my personal playbook. Surprisingly in conversations with some Red Teamers I know they dismissed the information as it is a Blue/Defense technology. These comment...
https://www.darkoperator.com/blog/2017/11/20/some-comments-and-thoughts-on-tradecraft
Published: 2017 11 20 11:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Some Comments and Thoughts on Tradecraft - published almost 9 years ago. Content: I have been writing a series on the new Windows Defender Exploit Guard features on Attack Surface Reduction where I cover my research on it. I'm researching the controls to add the information in to my personal playbook. Surprisingly in conversations with some Red Teamers I know they dismissed the information as it is a Blue/Defense technology. These comment... https://www.darkoperator.com/blog/2017/11/20/some-comments-and-thoughts-on-tradecraft Published: 2017 11 20 11:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Operational Look at Sysinternals Sysmon 6.20 Update - published almost 9 years ago.
Content: Sysmon has been a game changer for many organizations allowing their teams to fine tune their detection of malicious activity when combined with tools that aggregate and correlate events. A new version of Symon was recently released. Version 6.20 fixes bugs and adds new features. Some the of the note worthy changes for me are:Enhancements in WMI Logging. Ab...
https://www.darkoperator.com/blog/2017/11/24/operational-look-at-sysinternals-sysmon-620-update
Published: 2017 11 27 11:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: Sysmon has been a game changer for many organizations allowing their teams to fine tune their detection of malicious activity when combined with tools that aggregate and correlate events. A new version of Symon was recently released. Version 6.20 fixes bugs and adds new features. Some the of the note worthy changes for me are:Enhancements in WMI Logging. Ab...
https://www.darkoperator.com/blog/2017/11/24/operational-look-at-sysinternals-sysmon-620-update
Published: 2017 11 27 11:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Operational Look at Sysinternals Sysmon 6.20 Update - published almost 9 years ago. Content: Sysmon has been a game changer for many organizations allowing their teams to fine tune their detection of malicious activity when combined with tools that aggregate and correlate events. A new version of Symon was recently released. Version 6.20 fixes bugs and adds new features. Some the of the note worthy changes for me are:Enhancements in WMI Logging. Ab... https://www.darkoperator.com/blog/2017/11/24/operational-look-at-sysinternals-sysmon-620-update Published: 2017 11 27 11:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Rebuilding My Playbook .. Knowledge Base - published almost 9 years ago.
Content: I find myself in the situation where I lost my personal playbook by user error. I accidentally deleted the VM where I ran xWiki where it was kept and did not realized the mistake until days later. Even if painful to rebuild it is a good opportunity to think on how to better organize it and put it in a more flexible format. I Initially called my collection o...
https://www.darkoperator.com/blog/2017/12/10/nmba1hrmndda8m3eo7ipoh7bxvphz4
Published: 2017 12 13 11:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: I find myself in the situation where I lost my personal playbook by user error. I accidentally deleted the VM where I ran xWiki where it was kept and did not realized the mistake until days later. Even if painful to rebuild it is a good opportunity to think on how to better organize it and put it in a more flexible format. I Initially called my collection o...
https://www.darkoperator.com/blog/2017/12/10/nmba1hrmndda8m3eo7ipoh7bxvphz4
Published: 2017 12 13 11:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Rebuilding My Playbook .. Knowledge Base - published almost 9 years ago. Content: I find myself in the situation where I lost my personal playbook by user error. I accidentally deleted the VM where I ran xWiki where it was kept and did not realized the mistake until days later. Even if painful to rebuild it is a good opportunity to think on how to better organize it and put it in a more flexible format. I Initially called my collection o... https://www.darkoperator.com/blog/2017/12/10/nmba1hrmndda8m3eo7ipoh7bxvphz4 Published: 2017 12 13 11:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
Article: Operating Offensively Against Sysmon - published about 8 years ago.
Content: Sysmon is a tool written by Mark Russinovich that I have covered in multiple blog post and even wrote a PowerShell module called Posh-Sysmon to help with the generation of configuration files for it. Its main purpose is for the tracking of potentially malicious activity on individual hosts and it is based on the same technology as Procmon. It differs from ot...
https://www.darkoperator.com/blog/2018/10/5/operating-offensively-against-sysmon
Published: 2018 10 08 10:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: Sysmon is a tool written by Mark Russinovich that I have covered in multiple blog post and even wrote a PowerShell module called Posh-Sysmon to help with the generation of configuration files for it. Its main purpose is for the tracking of potentially malicious activity on individual hosts and it is based on the same technology as Procmon. It differs from ot...
https://www.darkoperator.com/blog/2018/10/5/operating-offensively-against-sysmon
Published: 2018 10 08 10:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Operating Offensively Against Sysmon - published about 8 years ago. Content: Sysmon is a tool written by Mark Russinovich that I have covered in multiple blog post and even wrote a PowerShell module called Posh-Sysmon to help with the generation of configuration files for it. Its main purpose is for the tracking of potentially malicious activity on individual hosts and it is based on the same technology as Procmon. It differs from ot... https://www.darkoperator.com/blog/2018/10/5/operating-offensively-against-sysmon Published: 2018 10 08 10:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Being Grateful at Heilderburg - published over 7 years ago.
Content: Recently while in the bar of the Crown Plaza in Heidelberg for the Troopers conference I became aware of the number of how grateful I should be for what I have in this industry. For what I’m grateful for is not technical or recognition but of the group of people in the industry, I have the honor to call friends. I would like to share some of them in this blo...
https://www.darkoperator.com/blog/2019/3/24/being-grateful-at-heilderburg
Published: 2019 03 25 01:06:52
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: Recently while in the bar of the Crown Plaza in Heidelberg for the Troopers conference I became aware of the number of how grateful I should be for what I have in this industry. For what I’m grateful for is not technical or recognition but of the group of people in the industry, I have the honor to call friends. I would like to share some of them in this blo...
https://www.darkoperator.com/blog/2019/3/24/being-grateful-at-heilderburg
Published: 2019 03 25 01:06:52
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Being Grateful at Heilderburg - published over 7 years ago. Content: Recently while in the bar of the Crown Plaza in Heidelberg for the Troopers conference I became aware of the number of how grateful I should be for what I have in this industry. For what I’m grateful for is not technical or recognition but of the group of people in the industry, I have the honor to call friends. I would like to share some of them in this blo... https://www.darkoperator.com/blog/2019/3/24/being-grateful-at-heilderburg Published: 2019 03 25 01:06:52 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
|
Article: Getting DNS Client Cached Entries with CIM/WMI - published almost 7 years ago.
Content: What is DNS CacheThe DNS cache maintains a database of recent DNS resolution in memory. This allows for faster resolution of hosts that have been queried in the recent past. To keep this cache fresh and reduce the chance of stale records the time of items in the cache is of 1 day on Windows clients. The DNS Client service in Windows is the one that manages t...
https://www.darkoperator.com/blog/2020/1/14/getting-dns-client-cached-entries-with-cimwmi
Published: 2020 02 03 10:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
Content: What is DNS CacheThe DNS cache maintains a database of recent DNS resolution in memory. This allows for faster resolution of hosts that have been queried in the recent past. To keep this cache fresh and reduce the chance of stale records the time of items in the cache is of 1 day on Windows clients. The DNS Client service in Windows is the one that manages t...
https://www.darkoperator.com/blog/2020/1/14/getting-dns-client-cached-entries-with-cimwmi
Published: 2020 02 03 10:00:00
Received: 2021 06 06 09:05:08
Feed: Blog
Source: Blog
Category: Cyber Security
Topic: Cyber Security
|
Article: Getting DNS Client Cached Entries with CIM/WMI - published almost 7 years ago. Content: What is DNS CacheThe DNS cache maintains a database of recent DNS resolution in memory. This allows for faster resolution of hosts that have been queried in the recent past. To keep this cache fresh and reduce the chance of stale records the time of items in the cache is of 1 day on Windows clients. The DNS Client service in Windows is the one that manages t... https://www.darkoperator.com/blog/2020/1/14/getting-dns-client-cached-entries-with-cimwmi Published: 2020 02 03 10:00:00 Received: 2021 06 06 09:05:08 Feed: Blog Source: Blog Category: Cyber Security Topic: Cyber Security |
All Articles
Ordered by Date Received
Page:
<<
<
10,553 (of 10,737)
>
>>
Total Articles in this collection: 536,867
- "All Articles" links back to the front page, effectivly the Planet "Home Page"; shows all articles, with no selections, or groupings.
- Default date ordering is by "Received Date" (due to not all RSS feeds having a "Published Date").
- Only Published Date selections use the articles Published Date.
- The first page always shows fifty items plus from zero to up to a remaining forty-nine items, before they are commited permently to the next page.
- All subsequent pages show fifty items.
- Pagination is in reverse ordering (so that pages are permamenent links, aka "permalinks", to their content).
- "<<" moves you to the first page (aka newest articles)
- ">>" moves you to the last page (aka oldest articles)
- "<" moves you to the previous page (aka newer articles)
- ">" moves you to the next page (aka older articles)
- Return to the top of this page Go Now
