Welcome to our
Cyber Security News Aggregator
.Cyber Tzar
provide acyber security risk management
platform; including automated penetration tests and risk assesments culminating in a "cyber risk score" out of 1,000, just like a credit score.
First slide label
Some representative placeholder content for the first slide.
Second slide label
Some representative placeholder content for the second slide.
Third slide label
Some representative placeholder content for the third slide.
Cbrutekrag - Penetration Tests On SSH Servers Using Brute Force Or Dictionary Attacks. Written In C
published on 2023-05-16 12:30:00 UTC by UnknownContent:
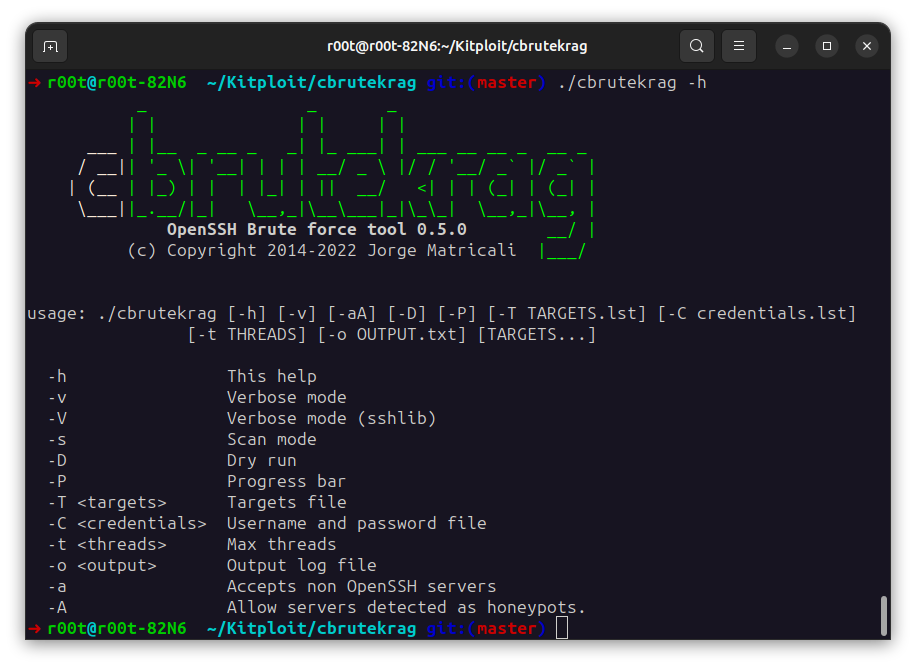
Penetration tests on SSH servers using dictionary attacks. Written in C.
brute krag means "brute force" in afrikáans
Disclaimer
This tool is for ethical testing purpose only.
cbrutekrag and its owners can't be held responsible for misuse by users.
Users have to act as permitted by local law rules.
Requirements
cbrutekrag uses libssh - The SSH Library (http://www.libssh.org/)
Build
Requirements:
makegcccompilerlibssh-dev
git clone --depth=1 https://github.com/matricali/cbrutekrag.git
cd cbrutekrag
make
make install
Static build
Requirements:
cmakegcccompilermakelibssl-devlibz-dev
git clone --depth=1 https://github.com/matricali/cbrutekrag.git
cd cbrutekrag
bash static-build.sh
make install
Run
OpenSSH Brute force tool 0.5.0 __/ | (c) Copyright 2014-2022 Jorge Matricali |___/ usage: ./cbrutekrag [-h] [-v] [-aA] [-D] [-P] [-T TARGETS.lst] [-C combinations.lst] [-t THREADS] [-o OUTPUT.txt] [TARGETS...] -h This help -v Verbose mode -V Verbose mode (sshlib) -s Scan mode -D Dry run -P Progress bar -T <targets> Targets file -C <combinations> Username and password file -t <threads> Max threads -o <output> Output log file -a Accepts non OpenSSH servers -A Allow servers detected as honeypots." dir="auto">
$ cbrutekrag -h
       _                _       _
      | |              | |     | |
  ___ | |__  _ __ _   _| |_ ___| | ___ __ __ _  __ _
 / __|| '_ \| '__| | | | __/ _ \ |/ / '__/ _` |/ _` |
| (__ | |_) | |  | |_| | ||  __/   <| | | (_| | (_| |
 \___||_.__/|_|   \__,_|\__\___|_|\_\_|  \__,_|\__, |
          OpenSSH Brute force tool 0.5.0        __/ |
      (c) Copyright 2014-2022 Jorge Matricali  |___/


usage: ./cbrutekrag [-h] [-v] [-aA] [-D] [-P] [-T TARGETS.lst] [-C combinations.lst]
		[-t THREADS] [-o OUTPUT.txt] [TARGETS...]

  -h                This help
  -v                Verbose mode
  -V                Verbose mode (sshlib)
  -s                Scan mode
  -D                Dry run
  -P                Progress bar
  -T <targets>      Targets file
  -C <combinations> Username and password file  -t <threads>      Max threads
  -o <output>       Output log file
  -a                Accepts non OpenSSH servers
  -A                Allow servers detected as honeypots.
Example usages
cbrutekrag -T targets.txt -C combinations.txt -o result.log
cbrutekrag -s -t 8 -C combinations.txt -o result.log 192.168.1.0/24
Supported targets syntax
- 192.168.0.1
- 10.0.0.0/8
- 192.168.100.0/24:2222
- 127.0.0.1:2222
Combinations file format
root root
root password
root $BLANKPASS$
https://www.kitploit.com/2023/05/cbrutekrag-penetration-tests-on-ssh.html
Published: 2023 05 16 12:30:00
Received: 2023 05 25 13:45:06
Feed: PenTest and Hacking Tools - powered by FeedBurner
Source: PenTest and Hacking Tools - powered by FeedBurner
Category: News
Topic: Security Tooling
Views: 19
