Welcome to our
Cyber Security News Aggregator
.Cyber Tzar
provide acyber security risk management
platform; including automated penetration tests and risk assesments culminating in a "cyber risk score" out of 1,000, just like a credit score.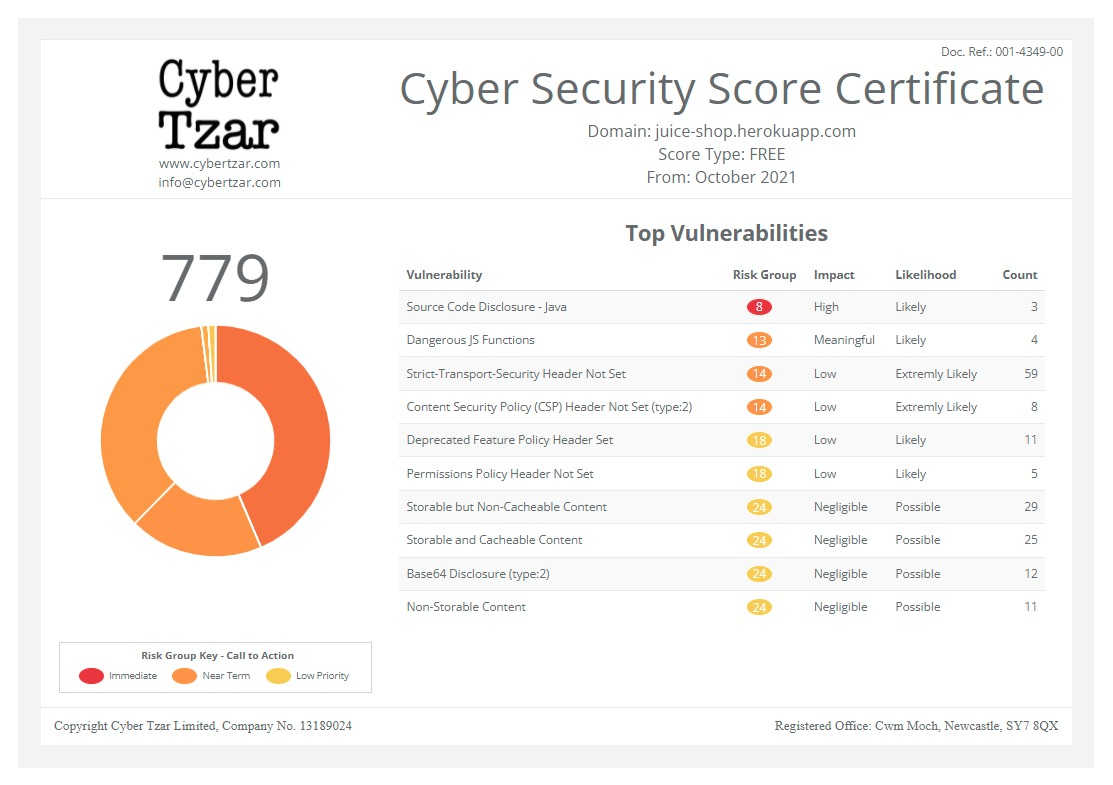
First slide label
Some representative placeholder content for the first slide.
Second slide label
Some representative placeholder content for the second slide.
Third slide label
Some representative placeholder content for the third slide.
The Classics Return: Vulnerable E-Mail Scripts, (Wed, Nov 4th)
published on 2026-11-04 13:24:13 UTC byContent:
One of the early web application vulnerabilities I remember was CVE-2000-0411 [CVE]. This was a simple vulnerability in a CGI-bin script used to send e-mail. The vulnerability was pretty straightforward: Adding additional parameters to the URL leaked environment variables. Other vulnerabilities allowed setting the "To" address and were heavily abused by spammers. And if parameters were passed directly to the sendmail binary, similar vulnerabilities could allow arbitrary code execution.
https://isc.sans.edu/diary/rss/33488
Published: 2026 11 04 13:24:13
Received: 2026 11 05 17:12:30
Feed: SANS Internet Storm Center, InfoCON: green
Source: SANS Internet Storm Center, InfoCON: green
Category: Alerts
Topic: Vulnerabilities
Views: 0
