Cyber Security News Aggregator
.Cyber Tzar
provide acyber security risk management
platform; including automated penetration tests and risk assesments culminating in a "cyber risk score" out of 1,000, just like a credit score.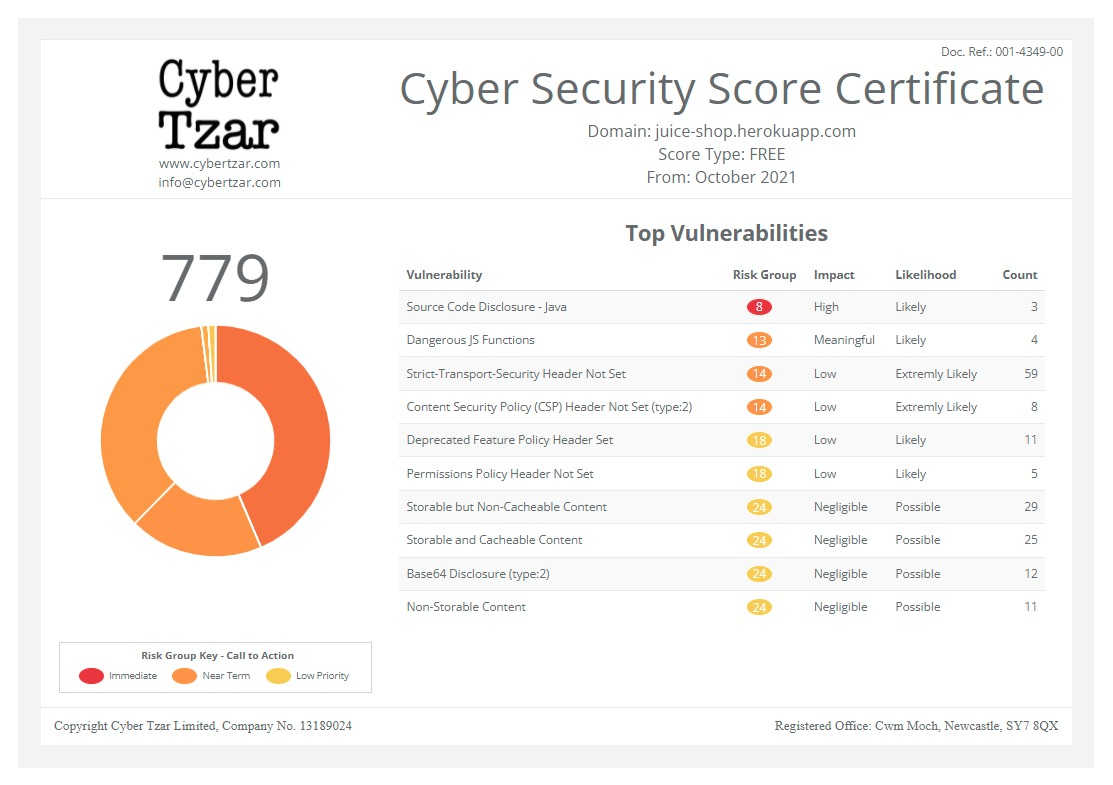
First slide label
Some representative placeholder content for the first slide.
Second slide label
Some representative placeholder content for the second slide.
Third slide label
Some representative placeholder content for the third slide.
TightVNC Viewer Pre-auth RCE
published on 2026-10-29 14:09:08 UTC by /u/SSDisclosureContent:
What if a VNC server could make your viewer believe it had a ~4 GB framebuffer… while actually allocating only 128 KB?
That’s the core of this TightVNC vulnerability.
A malicious server can announce a crafted 32768 × 32769 screen at 32bpp, causing the framebuffer size calculation to overflow. The allocation wraps down to 128 KB, but the viewer continues using the original, much larger dimensions when calculating pixel writes.
The result is a server-controlled out-of-bounds write in the viewer.
It’s a good example of how a relatively small integer-overflow mistake can become a powerful memory-corruption primitive when different parts of the application disagree about the true size of a buffer.
[link] [comments]
https://www.reddit.com/r/netsec/comments/1xil17j/tightvnc_viewer_preauth_rce/
Published: 2026 10 29 14:09:08
Received: 2026 11 05 17:18:09
Feed: /r/netsec - Information Security News and Discussion
Source: /r/netsec - Information Security News and Discussion
Category: Cyber Security
Topic: Cyber Security
Views: 0
