Welcome to our
Cyber Security News Aggregator
.Cyber Tzar
provide acyber security risk management
platform; including automated penetration tests and risk assesments culminating in a "cyber risk score" out of 1,000, just like a credit score.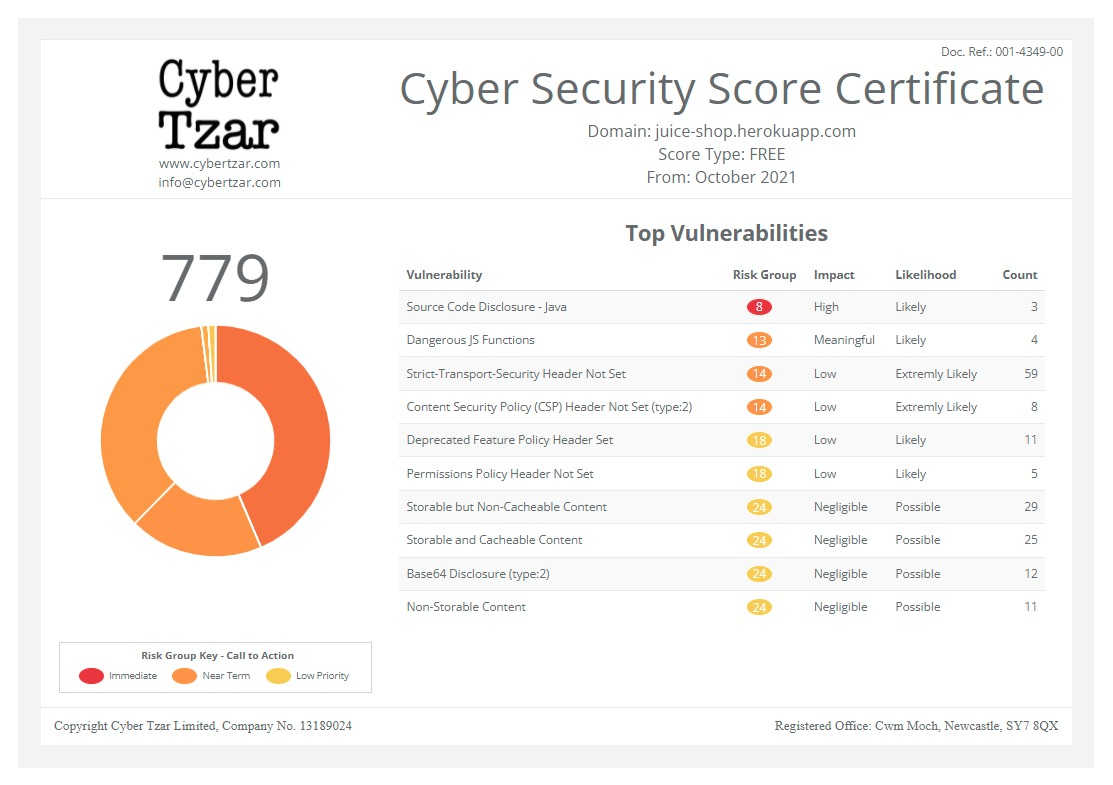
First slide label
Some representative placeholder content for the first slide.
Second slide label
Some representative placeholder content for the second slide.
Third slide label
Some representative placeholder content for the third slide.
Forwarded Without Question: How Web Frameworks Overtrust the Forwarded Header
published on 2026-11-06 10:34:37 UTC by /u/luryusContent:
Many common web frameworks like Spring and Ruby on Rails trust the Forwarded header by default, even though most proxies don't actually have any support for it. This makes apps vulnerable to request hostname or client IP address spoofing in the default configurations.
I've been researching how the Forwarded header is supported across frameworks and proxies. Rails and Spring recently shipped fixes following my research. There are still other frameworks that need application configuration changes to be secure.
[link] [comments]
https://www.reddit.com/r/netsec/comments/1xp9n79/forwarded_without_question_how_web_frameworks/
Published: 2026 11 06 10:34:37
Received: 2026 11 06 10:37:58
Feed: /r/netsec - Information Security News and Discussion
Source: /r/netsec - Information Security News and Discussion
Category: Cyber Security
Topic: Cyber Security
Views: 0
