Welcome to our
Cyber Security News Aggregator
.Cyber Tzar
provide acyber security risk management
platform; including automated penetration tests and risk assesments culminating in a "cyber risk score" out of 1,000, just like a credit score.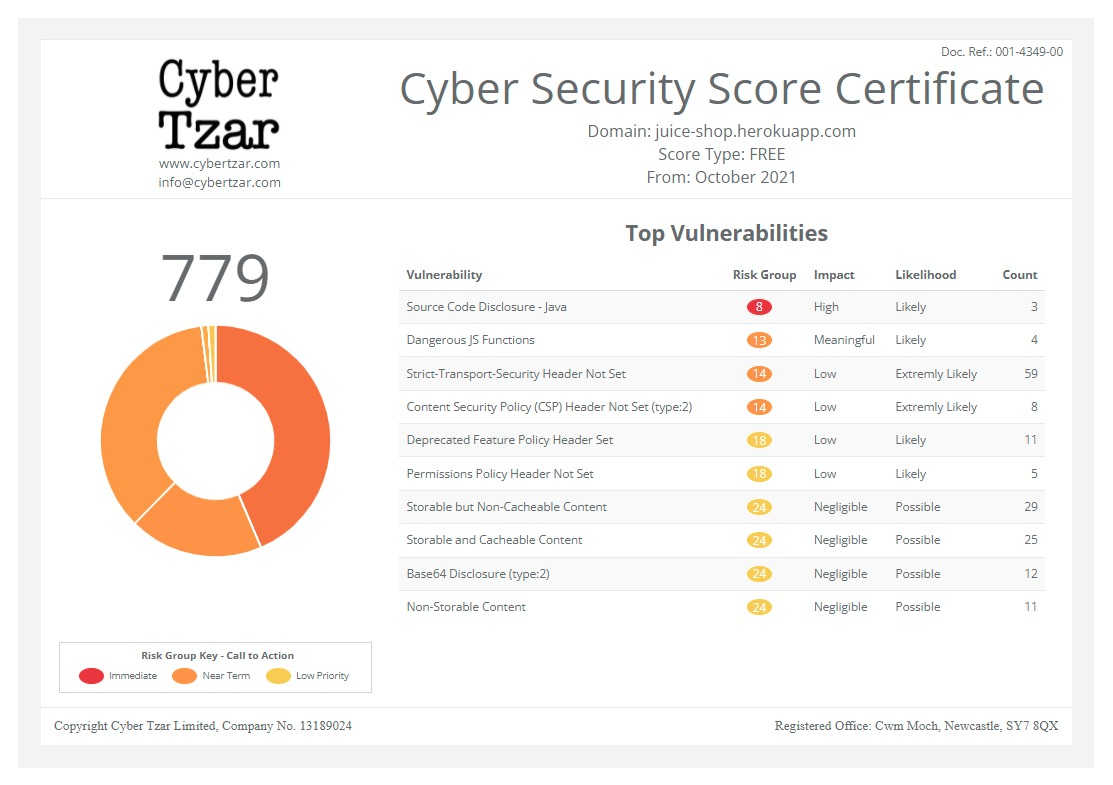
First slide label
Some representative placeholder content for the first slide.
Second slide label
Some representative placeholder content for the second slide.
Third slide label
Some representative placeholder content for the third slide.
Third-party risk management in critical infrastructure: NIS2, NERC CIP-013, CIRCIA, and the ...
published on 2026-11-15 09:54:06 UTC byContent:
... (Cyber Security - Supply Chain Risk Management) requires a documented supply chain cyber security risk management plan for high and medium impact ...
https://www.rescana.com/learn/industries/critical-infrastructure/
Published: 2026 11 15 09:54:06
Received: 2026 11 15 13:00:54
Feed: Google Alert – "cyber security"
Source: Google Alert
Category: News
Topic: Cyber Security
Views: 10
