Cyber Security News Aggregator
.Cyber Tzar
provide acyber security risk management
platform; including automated penetration tests and risk assesments culminating in a "cyber risk score" out of 1,000, just like a credit score.
First slide label
Some representative placeholder content for the first slide.
Second slide label
Some representative placeholder content for the second slide.
Third slide label
Some representative placeholder content for the third slide.
Java4Shell (CVE-2026-114938): What Is Confirmed, Who Is Exposed, and How to Hunt It
published on 2026-11-17 23:11:32 UTC by MayureshContent:
Java4Shell (CVE-2026-114938) is a heap out-of-bounds write in the x86_64 HotSpot Base64 decoder that uses AVX-512 VBMI. Oracle fixed it on November 17, 2026 and scored it CVSS 3.1 8.1 (AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H), component Compiler. It affects Oracle Java SE 17, 21, 25 and 27, the 8u511 performance build, and GraalVM. Standard Java 8 and Java 11 are not affected. It is not in CISA KEV (catalog 2026.11.17, released 2026-11-17T17:53:15Z) yet. In this post we see the root cause, read from the OpenJDK fix commit itself, and what it means for exposure. Two findings that matter for defenders – Java 21, 25 and 27 reach the vulnerable code with much shorter input than Java 17. Just over 31 characters instead of over 128 and hosts on Intel Skylake-SP and Cascade Lake, which have AVX-512 but not VBMI are not affected.
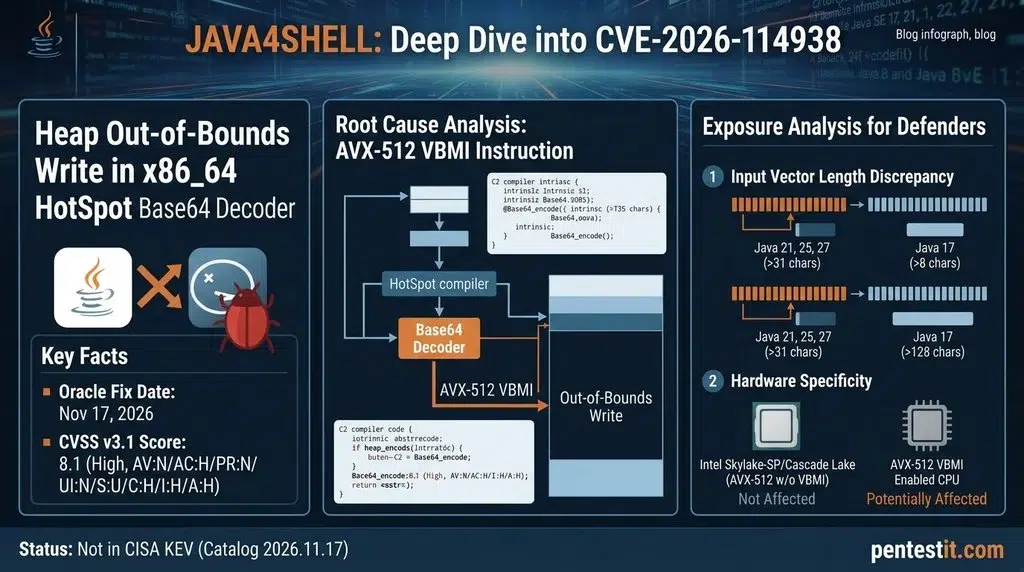
CVE-2026-114938 (Java4Shell)
- Unauthenticated heap out-of-bounds write, Oracle CVSS 3.1 8.1, Calif CVSS 4.0 9.2
- Java 21, 25 and 27 reach it with input over 31 characters
- October 2026 builds are on Oracle's affected list
- Needs x86_64 with AVX-512 VBMI and a JIT-compiled decoder
- Code execution claimed by Calif, not reproduced in public
- Not in CISA KEV 2026.11.17, no exploitation reported
Patch this week
outcome: Move to Oracle 17.0.21.1, 21.0.13.1, 25.0.5.1 or 27.0.1.1, or your vendor's build with JDK-8393212
outcome: Until then, -XX:-UseBASE64Intrinsics
Confirmed by Oracle and the OpenJDK fix
If you patched Java in October, you are still exposed to Oracle’s November Java SE fixes. Oracle lists 8u511, 11.0.33, 17.0.21, 21.0.13, 25.0.5 and 27.0.1 as affected.
What is confirmed about Java4Shell (CVE-2026-114938), and what is only reported?
The flaw, its scope and its root cause are now confirmed by Oracle and by the OpenJDK fix. Code execution is still only Calif’s claim, and nobody has reported exploitation.
| Claim | Status | Source |
|---|---|---|
| Calif found and reported Java4Shell | Confirmed. Oracle credits Quang Luong of Calif.io, and separately Albert Yang | Oracle advisory |
| CVE-2026-114938 is one of Oracle’s 11 Java SE fixes | Confirmed. CVSS 3.1 8.1, component Compiler | Oracle advisory |
| Heap out-of-bounds write in the AVX-512 Base64 decoder | Confirmed by the fix, JDK-8393212 | jdk17u commit 8ea73158af |
| 62-byte overflow | Reproduced independently on Intel Ice Lake | Upwind |
| CVSS 4.0 score of 9.2 | Calif’s score; Oracle uses CVSS 3.1 and scores 8.1 | Calif |
| Remote code execution and a Heartbleed-style memory read | Claimed by Calif and CISA. Upwind reproduced the overflow but not code execution | Calif, Upwind, CISA |
| A 65-byte input triggers it | Half right. A 65-byte input (64 plus a 1-byte tail) reaches the bug on Java 21 and 25, where the minimum is over 31; on Java 17 the minimum is over 128 | My inference of the fix, below |
| “Java 17 only” | Wrong. Oracle lists 17, 21, 25, 27 and 8u511b33-perf | Oracle advisory |
| Exploited in the wild | No. Not in CISA KEV 2026.11.17, no reports | CISA KEV |
| Public proof of concept | None found on November 17 | Searches on GitHub and the web |
The name “Java2Shell” also circulates. No primary source uses it. Calif’s name for the bug is Java4Shell.
Before the patch, several write-ups stated “Java 17 only” as fact, and it was wrong. The reported 65-byte trigger was half right: it works on Java 21 and 25, not on Java 17. Oracle has not assigned a CWE yet. My inference from the fix, is CWE-191 (integer underflow) leading to CWE-787 (out-of-bounds write).
Which Java versions and platforms are affected by Java4Shell?
Oracle lists Java SE 17, 21, 25 and 27, the 8u511 performance build, and GraalVM as affected by CVE-2026-114938. Standard Java 8 and Java 11 are not on the list, because they do not have the AVX-512 Base64 decoder.
| Product range | Affected software | Fixed build (Oracle patch number) | Minimum input length to reach the bug |
|---|---|---|---|
| Java SE 27 | 27.0.1.0.3 | 27.0.1.1 (Patch 40239622) | Not checked; same code lineage as 25 |
| Java SE 25 | 25.0.5.0.3 | 25.0.5.1 (Patch 40239624) | Over 31 characters |
| Java SE 21 | 21.0.13.0.3 | 21.0.13.1 (Patch 40239626) | Over 31 characters |
| Java SE 17 | 17.0.21.0.3 (code present since 17.0.6) | 17.0.21.1 (Patch 40239631) | Over 128 characters |
| Java SE 8 Enterprise Performance Pack | 8u511b33-perf | 8u513-perf (Patch 40239685) | Not checked |
| Oracle GraalVM for JDK | 17.0.21.0.3, 21.0.13.0.3 | 17.0.21.1, 21.0.13.1 | Not checked |
| Oracle GraalVM Enterprise Edition | 21.3.20.0.3 | 21.3.20.1 | Not checked |
| Java SE 11 | Not affected | 11.0.33.1 fixes other November CVEs | No AVX-512 decoder |
| Java SE 8 | Not affected | 8u513 fixes other November CVEs | No AVX-512 decoder |
| Java SE 7 (Market Driven Support) | Not affected | 7u523 fixes CVE-2026-114939, CVE-2026-114944 and CVE-2026-114946 only | Not applicable |
The affected builds come from the Oracle advisory’s Java SE risk matrix. The fixed builds and patch numbers come from Oracle’s Java SE patch availability document, CPU435, which needs a My Oracle Support login. I confirmed the OpenJDK side myself: the jdk17u tag jdk-17.0.21.1-ga contains the fix. The minimum lengths are from my reading of the jdk17u, jdk21u and jdk25u source.med the OpenJDK side myself: the jdk17u tag jdk-17.0.21.1-ga contains the fix. The minimum lengths are from my understanding of the jdk17u, jdk21u and jdk25u source.
The CPU decides exposure as much as the version does. The vulnerable code runs only on x86_64 CPUs with AVX-512 VBMI: Intel Ice Lake server and later, and AMD Zen 4 and later. Intel Skylake-SP and Cascade Lake have AVX-512 but no VBMI, so they skip it. AVX2-only machines and ARM servers such as AWS Graviton are not affected; the fix touches only the x86 stub.
OpenJDK distributions from Temurin, Corretto, Zulu, Microsoft and Red Hat ship on their own schedules. Look for JDK-8393212 in your vendor’s release notes rather than matching Oracle’s version numbers.
What is the root cause of Java4Shell?
The AVX-512 VBMI Base64 decoder in HotSpot computes a negative output size when a malformed input ends with a padded tail of 1 to 3 characters. The negative size turns its 64-byte write mask into all ones, so the decoder stores 64 bytes past the point where it should store almost nothing. The OpenJDK fix is just four lines long. The fix is JDK-8393212, “Base64 optimization improvements”, committed to jdk17u on November 12, 2026 as 8ea73158af, a backport of mainline commit e56f69c725f8. It adds one check at the start of the decoder’s final-fragment path in stubGenerator_x86_64.cpp:
__ BIND(L_finalBit);
// Now have 1 to 63 bytes left to decode

// A padded Base64 tail shorter than one complete block is handled by Java.
__ cmpl(length, 4);
__ jcc(Assembler::less, L_bruteForce);
Here is what happens without that check, from my reading of the same file:
bzhiqbuilds the store mask from the output size. With -1 or -2 as the bit index, it clears nothing, so all 64 mask bits stay set. The masked storeevmovdqubthen writes all 64 bytes of the vector register into the destination array.ver enters the vector loop that write-ups describe as the bug. It would take the stub’s scalar loop, or a padding path in the Java caller. Either the trigger size is wrong, or the bug is not in the vector code. I cannot tell which until the fix commit is public.- The vector path runs only on CPUs with AVX-512 VBMI, for non-MIME input longer than 128 bytes on Java 17. On Java 21 and 25 the same entry check is
cmpl(length, 31), so input longer than 31 bytes is enough. - The decoder consumes the input in 64-byte blocks. Whatever is left, 1 to 63 bytes, goes to
L_finalBit. - It sets the output size to (length / 4) * 3. For a tail of 1 to 3 bytes that is 0.
- If the last byte is
=, theL_paddingcode subtracts 1 from the output size, and 1 more if the byte before it is also=. The size becomes -1 or -2.
The Java caller passes the raw input length to the intrinsic, not a length rounded to a multiple of 4, so a malformed tail reaches the stub. A valid Base64 never has a tail of 1 to 3 characters, which is why Upwind saw no overflow from valid input in 300,000 runs. Intel’s AVX-512 decoder, JDK-8268276, was committed in mainline JDK 18 and was backported to 17.0.6 build 03 (JDK-8268276, backport review). A separate data-loss bug in the same stub, JDK-8321599, was fixed in January 2024 (integration notice). Java4Shell sat in this path for about four years on Java 17.
How long was Java4Shell in Java 17?
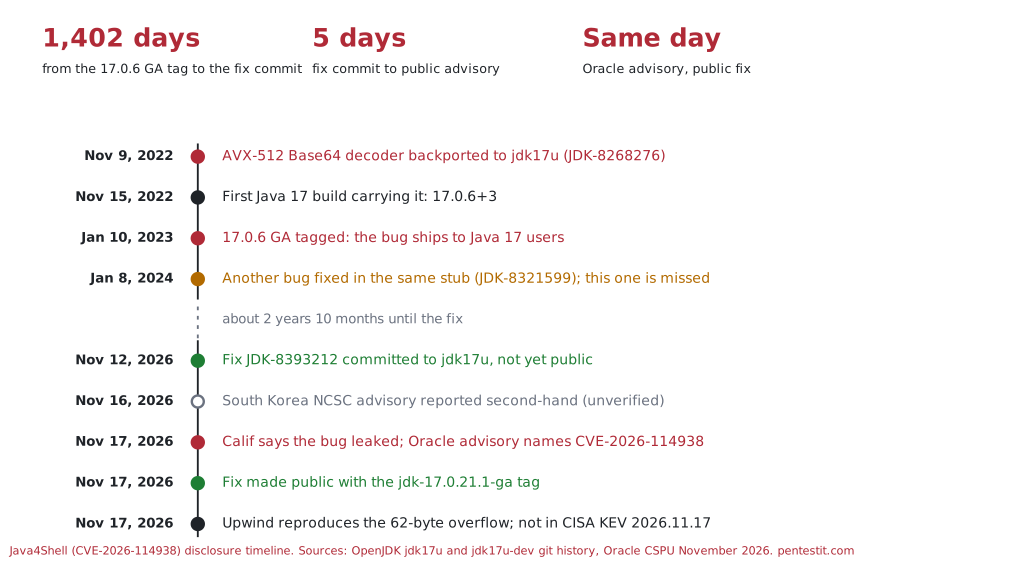
Java4Shell shipped in Java 17 builds for 1,402 days, from the 17.0.6 GA tag on January 10, 2023 to the fix commit on November 12, 2026. The fix then stayed private for 5 days. Calif’s leak statement, Oracle’s advisory and the public fix all landed on November 17, 2026.
[pt_bars title="Java4Shell timeline in days" caption="Source: OpenJDK jdk17u and jdk17u-dev git history, Oracle CSPU November 2026"]
group: max=1464
red+bold: Backport commit to fix commit = 1464 | Nov 9, 2022 to Nov 12, 2026
red: 17.0.6 GA tag to fix commit = 1402 | Jan 10, 2023 to Nov 12, 2026
amber: Missed bug fix in the same stub to fix commit = 1039 | JDK-8321599, Jan 8, 2024
green: Fix commit to public advisory = 5 | Nov 12 to Nov 17, 2026
grey: Calif leak statement to public fix = 0 | both Nov 17, 2026
[/pt_bars]| Date | Event | Source |
|---|---|---|
| November 17, 2026 | Upwind reproduces the 62-byte overflow; CVE-2026-114938 not in CISA KEV 2026.11.17 | Upwind, KEV file |
| November 17, 2026 | Fix made public with the jdk-17.0.21.1-ga tag; earlier that day the public jdk-17.0.21.1+1 tag did not contain it | My checks of openjdk/jdk17u |
| November 17, 2026 | Calif says the bug leaked; Oracle’s advisory names CVE-2026-114938 | Calif on X, Oracle |
| November 16, 2026 | South Korea NCSC advisory, reported second-hand and unverified | Endor Labs |
| November 12, 2026 | Fix JDK-8393212 committed to jdk17u (8ea73158af) | Commit |
| Not public | Calif reports the bug to Oracle | Oracle credits Calif.io and Albert Yang; no date given |
| January 8, 2024 | Data-loss bug JDK-8321599 fixed in the same stub; Java4Shell missed | jdk17u-dev commit 1f95796210 |
| January 10, 2023 | 17.0.6 GA tagged: the bug ships | jdk17u-dev tag jdk-17.0.6-ga |
| November 15, 2022 | First Java 17 build with the decoder: 17.0.6+3 | jdk17u-dev tag jdk-17.0.6+3 |
| November 9, 2022 | AVX-512 Base64 decoder backported to jdk17u (JDK-8268276) | jdk17u-dev commit 07050b000c |
This is how the timeline looks:
How would a Java4Shell attack work?
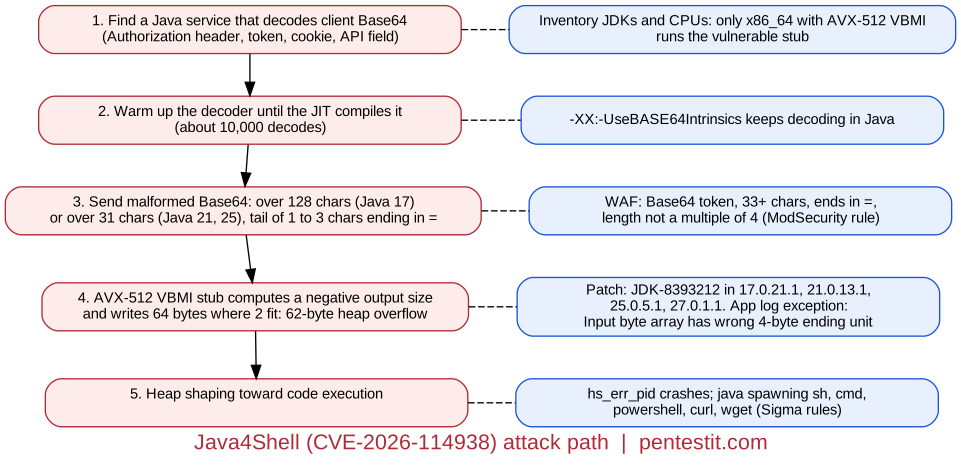
An attacker sends malformed Base64 to a Java service until the JIT compiles the decoder, then triggers a 62-byte heap overflow. Code execution is Calif’s claim alone.
- Find a target: Any Java service that decodes client-supplied Base64 with
java.util.Base64: Authorization headers, tokens, cookies, API fields. Enterprise applications such as Jenkins, Jira and Keycloak need to be checked for. - Warm up the decoder. The vulnerable code is a JIT intrinsic, so the decoder must be compiled first. A busy authentication endpoint is already warm.
- Send the trigger. Malformed Base64 over 128 characters on Java 17, or over 31 on Java 21 and 25, ending in
=with a length that is not a multiple of 4. - Corrupt the heap. The decoder writes 64 bytes where it should write almost nothing.
- Reach code execution. Calif says the overflow leads to remote code execution and a Heartbleed-style memory read.
Which hosts can reach the Java4Shell code execution?
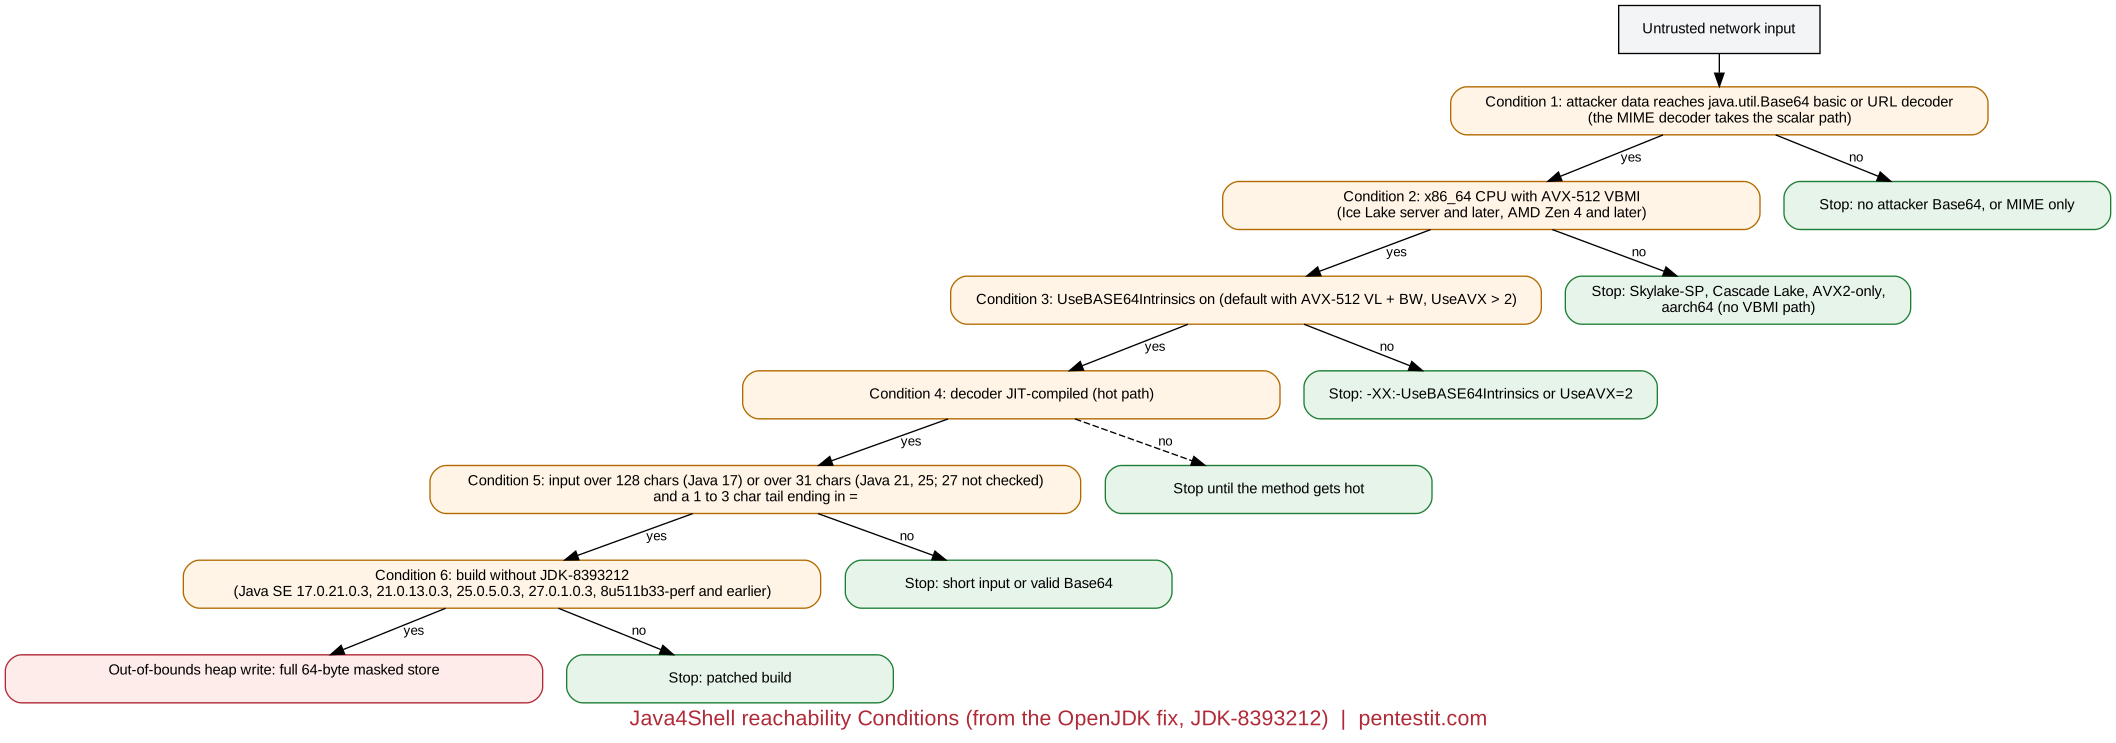
A host is exposed only if the following conditions are met and each one has an exit that stops the attack. The CPU gate removes many older servers outright, and the JVM flag gate is a mitigation you control today.
| Condition | Question | Exit that stops the attack | Basis |
|---|---|---|---|
| 1 | Does attacker data reach the java.util.Base64 basic or URL decoder? | No attacker Base64, or only the MIME decoder, which takes the scalar path | Stub entry checks isMIME |
| 2 | Is it an x86_64 CPU with AVX-512 VBMI? | Skylake-SP, Cascade Lake, AVX2-only x86 and aarch64 never run the vector path | Vector code sits inside the VBMI branch |
| 3 | Is UseBASE64Intrinsics on? It defaults on with UseAVX > 2 and AVX-512 VL plus BW | -XX:-UseBASE64Intrinsics or -XX:UseAVX=2 | vm_version_x86.cpp; |
| 4 | Has the JIT compiled the decoder? | Cold code runs the Java implementation | Needs about 10,000 decodes |
| 5 | Is the input over 128 characters (Java 17) or over 31 (Java 21, 25), with a 1 to 3 character tail ending in =? | Short input or valid Base64 | Stub entry check and the fix |
| 6 | Is the build missing JDK-8393212? | Patched build | Oracle risk matrix, jdk17u tag jdk-17.0.21.1-ga |
A login or token endpoint decodes Base64 on every request, so it is compiled soon after startup, and an attacker can warm up a quiet endpoint with ordinary requests. Condition 5 is where Java 21 and later differ most from Java 17: a malformed 33-character token in a Basic authentication header already clears it.
What detections work for Java4Shell?
The fix tells us the exact input shape, so request-level detection is now possible. A Base64 token that ends in = but whose length is not a multiple of 4 is always invalid, and it is the shape that reaches the bug. I tested the pattern below against 7,980 valid Base64 strings with no matches, and it matched all 1,656 malformed samples I generated.
ModSecurity (java4shell_modsecurity.conf). Regex tested in Python; not yet run on a ModSecurity engine.
SecRule REQUEST_HEADERS:Authorization "@rx (?i)^(?:basic|bearer)\s+(?:[A-Za-z0-9+/_-]{4}){8,}[A-Za-z0-9+/_=-]{0,2}=$" \
    "id:1146938,phase:1,log,pass,t:none,\
    msg:'Possible Java4Shell (CVE-2026-114938) malformed Base64 in Authorization header',\
    tag:'CVE-2026-114938',severity:'CRITICAL'"
SecRule ARGS|REQUEST_COOKIES "@rx ^(?:[A-Za-z0-9+/_-]{4}){8,}[A-Za-z0-9+/_=-]{0,2}=$" \
    "id:1146939,phase:2,log,pass,t:none,t:urlDecodeUni,\
    msg:'Possible Java4Shell (CVE-2026-114938) malformed Base64 in parameter or cookie',\
    tag:'CVE-2026-114938',severity:'CRITICAL'"
The rules log and pass. Switch pass to deny once you have watched them for a day; valid Base64 never has this shape, so the only other hits should be buggy clients.
Is the Java4Shell checker on GitHub reliable?
The public Java4Shell checker ashrafzaryouh/CVE-2026-114938 is safe to run but gives the wrong answer on Java 21, 25 and 27. It scores 51 out of 100 on my PoC repository reliability score. It gets Java 17 right and passes affected newer releases with exit code 0. The score is the one I use for every CVE: 50 points for content, 30 for provenance, 20 for hygiene, with each block scored only on the indicators that apply. Exploit repositories get a safety status and never a score. Stars are never scored. I graded commit 89a7485 on November 17, 2026, the current HEAD.
[pt_bod caption="PoC repository reliability score, graded November 17, 2026"]
[pt_bod_case title="ashrafzaryouh/CVE-2026-114938" tier="mid" verdict="51 / 100" call="Safe to run, wrong on Java 21 and later" heading="h3"]
low: Safety status clear: no binaries, no network code, only runs java -version
high: Lab: Java 21, 25 and 27 affected builds marked REVIEW, exit code 0
high: No check for AVX-512 VBMI or UseBASE64Intrinsics
mid: Content 20 of 45, provenance 6 of 20, hygiene 10 of 10
mid: Coverage 9 of 15 indicators; owner age and organization not checked
outcome: Use it for Java 17 inventory only, and update its version table
[/pt_bod_case]
[/pt_bod]
Classification. A scanner of the installed-package kind: one Python file that finds Java binaries, runs java -version on each and grades the version string. It has no network code and no exploit code. Its README is preliminary and still says the root cause is unconfirmed.
How the 51 breaks down.
| Information | Points Earned | Reason |
|---|---|---|
| Content (scanner) | 20 of 45 | Lab accuracy partial 15 of 30; fixed build cited for Java 17 only 5 of 10; no distribution backport caveat 0 of 5. The “both CVEs” indicator does not apply |
| Provenance | 6 of 20 | Origin unclear 6 of 10, since I traced this repository alone and not against other repositories; all four commits carry GitHub’s web-flow signature, not the owner’s key, 0 of 5; one author 0 of 5. Owner account age and organization were not checked |
| Hygiene | 10 of 10 | No prebuilt binaries; no download piped into a shell. No dependencies, workflows or push history to grade |
The weights do not change the picture: the score ranges from 47 to 58 under 70/20/10, 40/40/20, 40/30/30 and equal weights. Content stays under half, so the score cap of content plus 20 (64 here) does not bind.
Java4Shell FAQ
What is Java4Shell (CVE-2026-114938)? Java4Shell is a heap out-of-bounds write in the x86_64 HotSpot Base64 decoder that uses AVX-512 VBMI, found and reported by Calif. Oracle fixed it on November 17, 2026 and scored it CVSS 3.1 8.1. A malformed Base64 input makes the decoder write 64 bytes where almost none fit.
Which Java versions are affected by Java4Shell? Oracle lists Java SE 17.0.21.0.3, 21.0.13.0.3, 25.0.5.0.3, 27.0.1.0.3, 8u511b33-perf, GraalVM for JDK 17.0.21.0.3 and 21.0.13.0.3, and GraalVM Enterprise Edition 21.3.20.0.3. Standard Java 8 and Java 11 are not affected. On Java 17 the code has been present since 17.0.6.
Is Java4Shell being exploited? No exploitation has been reported. CVE-2026-114938 is not in CISA KEV catalog version 2026.11.17, and no public proof of concept was found on November 17, 2026.
How do I fix Java4Shell? Upgrade to Oracle Java 17.0.21.1, 21.0.13.1, 25.0.5.1 or 27.0.1.1, the 8u513 Enterprise Performance Pack, Oracle GraalVM for JDK 17.0.21.1 or 21.0.13.1, or GraalVM Enterprise Edition 21.3.20.1, or to an OpenJDK vendor build whose release notes list JDK-8393212, then restart every JVM.
Is there a workaround for Java4Shell? Add the JVM option -XX:-UseBASE64Intrinsics. It turns off the vulnerable AVX-512 decoder so Base64 decoding runs in Java. Upwind tested it clean on every affected version. It is not Oracle guidance, and it slows Base64 decoding.
How do I check if a server is exposed to Java4Shell? Check that the CPU reports avx512vbmi in /proc/cpuinfo, that java -XX:+PrintFlagsFinal shows UseBASE64Intrinsics set to true, and that the Java build is on Oracle’s affected list. Intel Skylake-SP and Cascade Lake servers have no VBMI and are not exposed.
Why is Java 21 easier to reach than Java 17? The vulnerable vector path starts at inputs longer than 31 bytes on Java 21 and 25, against longer than 128 bytes on Java 17. A short malformed token in an Authorization header is enough on the newer releases.
Is there a public Java4Shell PoC or exploit on GitHub? In the searches I ran on November 17, 2026, I did not find a public Java4Shell trigger or exploit. The repositories I found are defensive: version checkers such as ashrafzaryouh/CVE-2026-114938, a BigFix scanner, and a runtime patch from Xint. Read any script before you run it.
Is the ashrafzaryouh CVE-2026-114938 checker reliable? It is safe to run and correct for Java 17, but it marks affected Java 21, 25 and 27 builds as REVIEW and exits with code 0, and it does not check for AVX-512 VBMI. It scores 51 out of 100 on my PoC repository reliability score.
https://pentestit.com/java4shell-cve-2026-114938-detection-mitigation/
Published: 2026 11 17 23:11:32
Received: 2026 11 18 01:47:59
Feed: PenTestIT
Source: PenTestIT
Category: News
Topic: Security Tooling
Views: 2
