Cyber Security News Aggregator
.Cyber Tzar
provide acyber security risk management
platform; including automated penetration tests and risk assesments culminating in a "cyber risk score" out of 1,000, just like a credit score.
First slide label
Some representative placeholder content for the first slide.
Second slide label
Some representative placeholder content for the second slide.
Third slide label
Some representative placeholder content for the third slide.
AI Pentesting Frameworks: Abuse, Lineage, Fingerprints
published on 2026-11-14 20:48:23 UTC by MayureshContent:
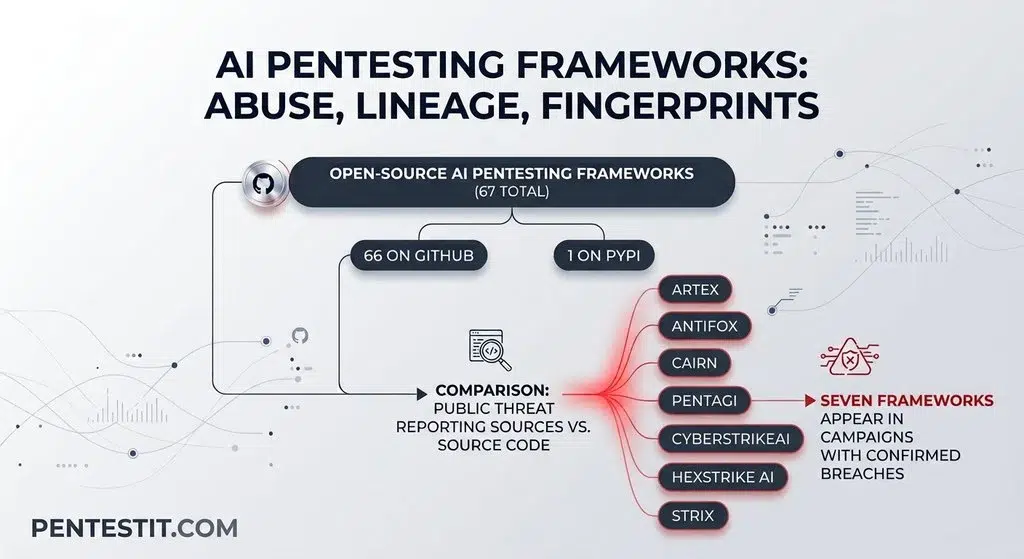
Frameworks like ARTEX interested me early on and lately have been hogging my news feed for obvious reasons. I set out to find additional such open source frameworks. This is the result – I found 67 open-source AI pentesting frameworks, 66 on GitHub and one on PyPI. I then compared them against public threat reporting sources and against their own source code. Seven frameworks already appear in campaigns with confirmed breaches. Eight of these repositories carry ARTEX’s code, one of them under a new name, and every ARTEX copy I could check still sends a common “user-agent: norma/0.4“. As of 13 November 2026, Shodan’s index held 1,558 IP addresses serving ARTEX’s icon and name, and most exposed ARTEX consoles still carry its original Chinese title.
This is Part 1 of a large series. It covers all 66 repositories and their forks at the level of evidence, code lineage and fingerprints. Later parts go deeper on the frameworks with abuse evidence. I wrote about scoring proof-of-concept repositories earlier in Quantitative Scoring of GitHub PoCs for Safe Detection Engineering; this series reuses the provenance parts of that method.
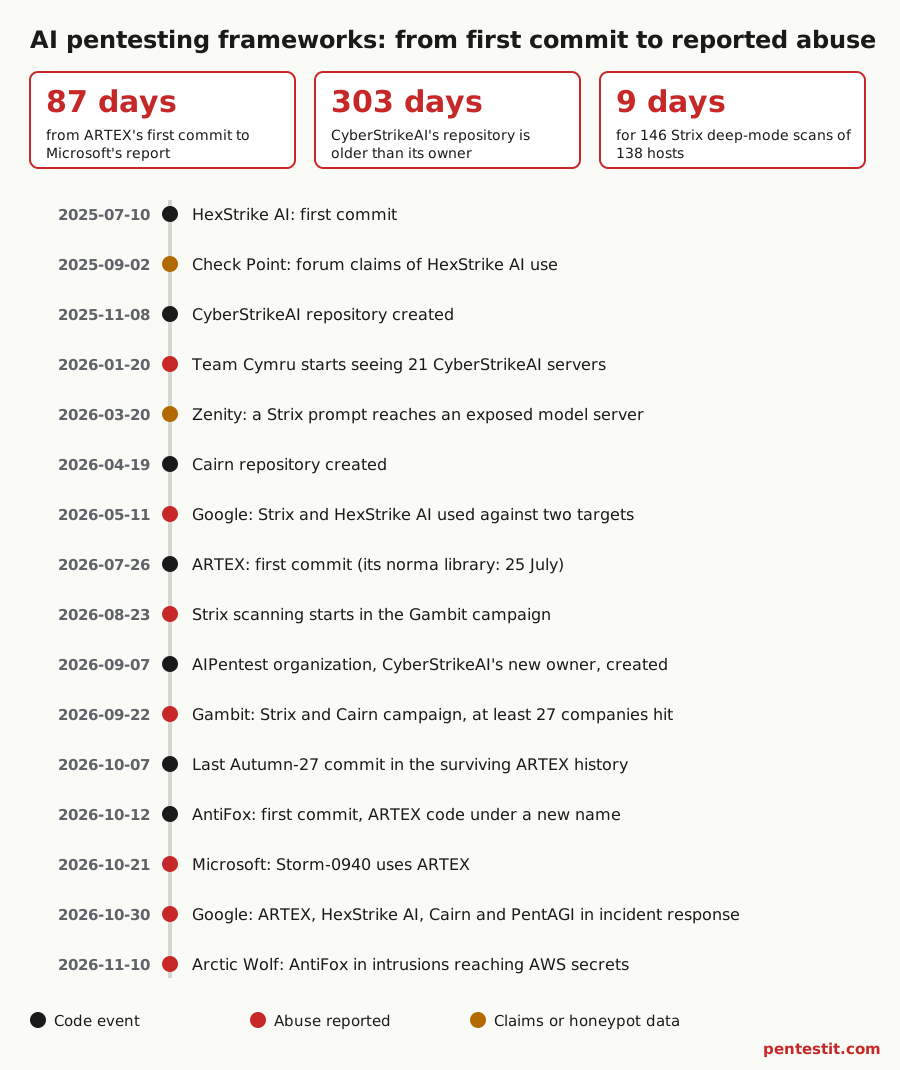
Which AI pentesting frameworks have attackers used?
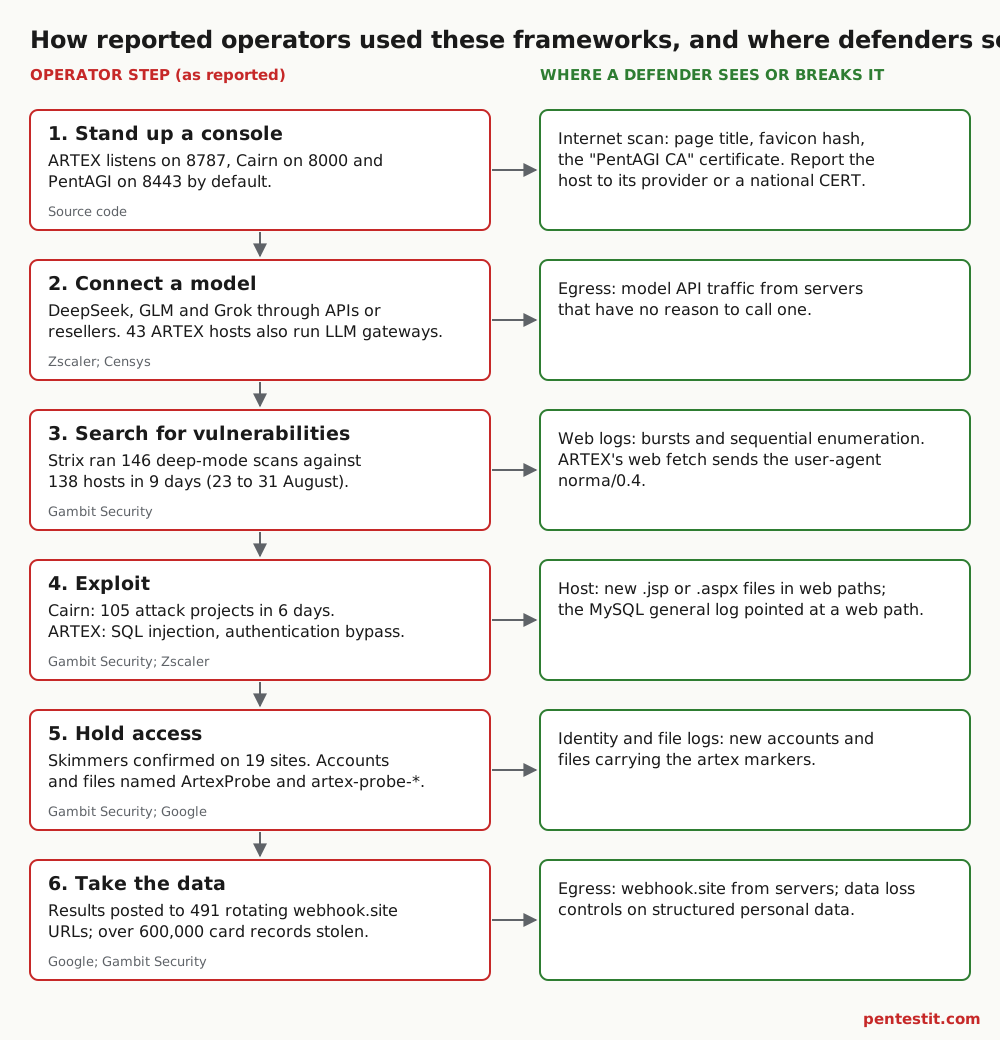
The abuse searches were mostly in English, so reporting in Chinese, Russian or other languages may be missing. I cloned all 66 repositories and read them at pinned commits between 9 and 12 November 2026 and counted exposed consoles with Shodan, keeping counts only and no IP addresses. Seven frameworks appear in campaigns where the reporting vendor confirms breaches: ARTEX, AntiFox, Cairn, PentAGI, CyberStrikeAI, HexStrike AI and Strix. CrowdStrike saw a malicious framework built from PentestGPT. I found no public abuse reporting for 56 of the 66 repositories, or for Villager.
Public abuse evidence across 66 AI pentesting framework repositories
ARTEX
- Microsoft ties it to Storm-0940 and the ConnectWise supply chain compromise
- CrowdStrike, Google, Wiz and Zscaler report further campaigns, the earliest from late August 2026
- The upstream repository was taken down in October 2026; forks and copies remain
- 1,558 IP addresses served its icon and name on Shodan on 13 November 2026
Used in confirmed breaches
Confirmed intrusion. The reports concern the original Autumn-27 release, which eight public repositories carry, one under another name.
Hunt norma/0.4 in web and proxy logs
Cairn
- Gambit Security saw 105 Cairn attack projects between 10 and 15 September 2026
- Google lists Cairn among frameworks seen in Mandiant incident response
- 41 IP addresses served its console on Shodan on 13 November 2026, nearly all on port 8000
Used in confirmed breaches
Confirmed intrusion. Gambit's campaign compromised at least 27 companies.
Find exposed consoles on port 8000
PentAGI
- Google reports a customized build of open-source PentAGI against Asian telecommunications firms
- Google says most of that activity stopped at scanning; some reached intrusion and persistence
- 495 IP addresses carried its page title on Shodan on 13 November 2026
Used in confirmed breaches
Confirmed intrusion through a customized build.
Find the PentAGI CA certificate
CyberStrikeAI
- Team Cymru found it on a server used in the FortiGate campaign
- Team Cymru saw 21 servers running it between January and February 2026
- Censys counts 70 hosts that run it next to ARTEX
- 220 IP addresses showed its title and icon on Shodan on 13 November 2026
Used in confirmed breaches
Confirmed intrusion: Team Cymru tied a CyberStrikeAI server to the FortiGate campaign Amazon reported.
Watch for servers running it
Strix
- Gambit Security saw 146 deep-mode runs against 138 hosts, 23 to 31 August 2026
- Strix found the vulnerabilities; Cairn did the exploitation
- Google saw a suspected PRC-nexus actor run Strix against two targets
Used in a breach campaign
Used in a campaign with confirmed breaches, in a reconnaissance role.
Look for deep-mode scan bursts
HexStrike AI
- Google and Mandiant saw threat actors abuse it in incident response engagements (October 2026)
- Google earlier saw a suspected PRC-nexus actor use it against a Japanese technology firm
- Zenity saw its 150-tool definition sent to an exposed model server
- Check Point's 2025 report covers forum claims, not observed intrusions
Used in confirmed breaches
Confirmed intrusion. Google's October report names it with ARTEX and CAIRN in incident response, without describing a HexStrike intrusion in detail.
Check model servers for its tool set
AntiFox
- Arctic Wolf tied Alibaba Cloud hosts running AntiFox to a compromised IIS server and a production AWS secret read (10 November 2026)
- Arctic Wolf lists its console title and port 8787, the same values its code sets
- 145 IP addresses served its icon and name on Shodan on 13 November 2026
Used in confirmed breaches
Confirmed intrusion. AntiFox is ARTEX's code under a new name, so the ARTEX hunts apply to it.
Find consoles titled AntiFox on port 8787
PentestGPT
- CrowdStrike says one actor's framework was derived from PentestGPT
- That actor targeted at least 15 healthcare entities in Argentina
Derived build abused
Abuse of a derived build, not of PentestGPT as published.
Treat derived builds as separate tools
Gambit names Strix here: (Gambit Security). For CyberStrikeAI, Team Cymru found the CyberStrikeAI banner on an IP address that Amazon had shared from a campaign against FortiGate devices, and saw 21 IP addresses running CyberStrikeAI between 20 January and 26 February 2026.
Whose code is inside these frameworks?
Three code families account for most of the “inspiration” in this set. I traced them by comparing distinctive code lines across all 66 repositories and by reading each repository’s commit history.
The ARTEX family
Eight repositories carry ARTEX’s code to a large extent. The original, by the developer Autumn-27, was taken down in October 2026 (Google). BaaRai/ARTEX is an English translation fork. Its history holds Autumn-27’s commits from 26 July to 7 October 2026, then BaaRai’s own from 8 October. GitHub does not mark it as a fork, but its README does. The other seven share between 45% and 89% of their distinctive code lines with earlier members of the family. Google also names a commercial version – ARTEX PRO. Since it is not public and I did not have access, it is not in this study.
| Repository Name | Unique shared lines | norma library evidence |
|---|---|---|
| BaaRai/ARTEX | Carries the original history | BaaRai/Norma v0.4.6 |
| acheong08/artex | 86.5% | Original Autumn-27/norma v0.4.3 |
| ijlalhaider313/ARTEX | 78.7% | Copy inside the repository (third_party/norma) |
| 2561769445/ycode-auto-pentest | 84.0% | Original Autumn-27/norma v0.4.3 |
| chu0119/Pojun | 75.3% | chu0119/Norma v0.4.4 |
| F0ran9/forang | 76.8% | A local path outside the repository |
| cskwork/scopeweaver | 50.1% | Copy inside the repository (third_party/norma) |
| AntiFox-AI/antifox | 59.8% | Copied in and renamed engine/; no norma dependency listed |
ycode’s first commit describes it as further development of ARTEX 0.3.23, and it carried a compiled artex.exe until a later commit removed it.
AntiFox: ARTEX under another name
AntiFox-AI/antifox presents itself as its own platform. Its history starts with a single commit on 12 October 2026, days after the ARTEX repository came down, followed by ten more through 31 October. The words ARTEX, Autumn-27 and BaaRai appear nowhere in its code. The code says otherwise. 59% of its distinctive code lines, norma excluded, also appear in Autumn-27’s last ARTEX commit, against at most 4.2% for any framework outside the family. 25 of its top-level folders and files have the same names as BaaRai’s ARTEX. Its console listens on port 8787, as ARTEX does, and its demo data is timestamped 26 July 2026, the date of ARTEX’s first commit.
norma/0.4: mystery behind the user-agent
Wiz listed the “User-Agent: norma/0.4” among its Storm-0940 indicators (Wiz). It comes from norma, which its README calls a general-purpose agent harness SDK in Go. Autumn-27 wrote it with a first commit dated 25 July 2026, one day before ARTEX’s, and ARTEX depends on it. The library’s web fetch tool sets norma/0.4 on each request and on its retry. The original ARTEX, at its last surviving commit of 7 October 2026, turns that tool on for its chat, main, planner and worker agents. I found the same value in every norma copy I could check: BaaRai’s v0.4.6, chu0119’s v0.4.4, the copies two forks keep in their repositories and AntiFox’s renamed copy. The library’s search tool sets a fixed Firefox 128 user-agent of its own.
So norma/0.4 identifies an agent built on norma, not ARTEX itself. In this set of 66 repositories, only the ARTEX family uses norma. I could not search the rest of GitHub for other projects built on it, so read a hit as a norma-based agent, with ARTEX and its copies as the known users. A search of ARTEX’s own repository does not find norma/0.4. The other ARTEX indicators that vendors published are a different case. ReconProbe/1.0, the ArtexProbe account name, artex-probe-* file names and webhook.site do not appear anywhere in the full commit histories of the eight ARTEX-family repositories. I read that as the model or the operator producing them at run time, which makes them campaign specific indicators and not framework fingerprints.
Hunt for user-agents starting with norma/0. in web server and proxy logs. A hit from the internet means a norma-based agent fetched your site. A hit leaving your network means one is running inside it. Two Sigma rules for this are in my Sigma rule repository.
The OpenCode family
CyberStrikeus/CyberStrike is built on the history of OpenCode, an open-source AI coding agent. Its first commit, dated 21 March 2025, exists in the OpenCode repository. s0ld13rr/pentestcode imported OpenCode’s code in a single first commit: 372 of its files mention opencode and its support link points to OpenCode’s Discord server. The two share 61% of PentestCode’s distinctive lines but no history and no authors. Each took its code from OpenCode on its own. A third, FrancescoStabile/numasec, shares about 41% of its distinctive lines with both and nothing with the rest of the set. Its history also starts from a single import, and seven of its files mention opencode.
PentestGPT and its forks
YasodGinige/AutoPentester starts from the same first commit as GreyDGL/PentestGPT, so it is a PentestGPT fork by history. It has changed enough that only 11.8% of its distinctive lines still match.
Which fingerprints exist in the code that runs?
I checked console fingerprints for these frameworks against their source code: page titles, favicon hashes computed the way Shodan computes them, the one certificate field, default ports and user-agents. 58 exist in the code at its current commit, and each is in the fingerprints CSV with the file it comes from. The table shows the ones for frameworks with reported use. Four others need a warning before you rely on them.
| Framework | Fingerprint | Value | Where in the source |
|---|---|---|---|
| PentAGI | page title | PentAGI | frontend/index.html |
| PentAGI | TLS certificate issuer | PentAGI CA | frontend/scripts/generate-ssl.ts |
| Strix | page title | Strix Results | strix/interface/viewer/frontend/index.html |
| PentAGI | favicon hash (Shodan MurmurHash3) | -1596753120 | frontend/public/favicon/favicon.ico |
| PentAGI | default port | 8443 | default listen port, .env.example |
| Cairn | default port | 8000 | default –port, cli.py |
| ARTEX family and AntiFox | default port | 8787 | default console port, docker-compose.yml |
| HexStrike AI | default port | 8888 | default port, hexstrike_server.py |
| HexStrike AI | User-agent | HexStrike-HTTP-Framework/1.0 (Advanced Security Testing) | hexstrike_server.py, line 13287 |
| HexStrike AI | User-agent | HexStrike-BrowserAgent/1.0 (Security Testing) | hexstrike_server.py, line 13644 |
| ARTEX family and AntiFox | user-agent (web fetch) | norma/0.4 | norma tool/webfetch.go lines 188 and 195 (AntiFox: engine/tool/webfetch.go) |
| Strix, and Cybermes (ships a copy of Strix) | favicon hash (Shodan MurmurHash3) | -566184040 | .github/logo.png; docs/images/logo.png; docs/logo/strix.png |
| ARTEX family (ARTEX, ScopeWeaver and two ARTEX forks) | favicon hash (Shodan MurmurHash3) | -576220750 | web/src/app/favicon.ico |
| ARTEX family (ARTEX, ScopeWeaver, Pojun and two ARTEX forks) | favicon hash (Shodan MurmurHash3) | -1898746557 | web/src/app/icon.png |
| AntiFox | favicon hash (Shodan MurmurHash3) | -1356779733 | web/src/app/icon.png |
| Cairn | page title | Cairn | cairn/src/cairn/server/static/index.html |
| Cairn | favicon hash (Shodan MurmurHash3) | 762324858 | cairn/src/cairn/server/static/favicon.svg |
| CyberStrikeAI | page title | CyberStrikeAI | web/templates/index.html |
| CyberStrikeAI | favicon hash (Shodan MurmurHash3) | -1349384020 | web/static/favicon.ico |
| CyberStrikeAI | User-agent | Mozilla/5.0 (compatible; CyberStrikeAI-WebShell/1.0) | internal/handler/webshell.go, line 799 |
| CyberStrikeAI | Certificate | Subject and issuer CN=CyberStrikeAI | internal/app/main_server_tls.go, line 114 |
| CyberStrikeAI | Beacon header | X-Implant-Token with X-Session-Token | internal/c2/payload_templates/beacon.go.tmpl, line 375 |
| ARTEX family | page title | ARTEX — Autonomous Penetration Testing Console | web/src/config/app-config.ts (ARTEX and acheong08/artex; earlier commits: ARTEX — 自主渗透测试控制台) |
| AntiFox | page title | AntiFox — 自主渗透测试控制台 | web/src/config/app-config.ts |
| Cairn | HTML string | intentChipGlow | cairn/src/cairn/server/static/index.html |
One page title that circulates without a project name, “pentest-ai · dashboard”, belongs to 0xSteph/pentest-ai, which sets it in api/static/index.html.
Villager: one listener, and test addresses
Villager is not on GitHub. Cyberspike distributes it as the Python package villager, and Straiker counted 10,030 downloads by 11 September 2025 and reported no confirmed threat actor use. Straiker listed four ports and a Cyberspike model endpoint as indicators. I downloaded the release that was current on Straiker’s publication date, 0.1.dev38, and the latest, 0.2.1rc1. In both, the villager command starts one server, bound to all interfaces on port 37695. Port 25989 appears only as a hardcoded private address the MCP client connects to, port 1611 only in a test file nothing imports, the Cyberspike endpoint only in a unit test, and port 8080 not at all. Straiker may have looked at parts outside the package, such as its Kali container images.
The PentestCode favicon is OpenCode’s icon
PentestCode’s web interface serves favicon hash -196523122. The icon behind it is OpenCode’s: OpenCode’s web application serves the same file through a symbolic link, and PentestCode kept that link unchanged. A favicon search for PentestCode therefore also returns any web interface built on OpenCode that keeps the icon.
Do not use favicon hash -196523122 alone to find PentestCode. Pair it with the page title, or expect to find OpenCode instances.
Weak, stale and shared fingerprints
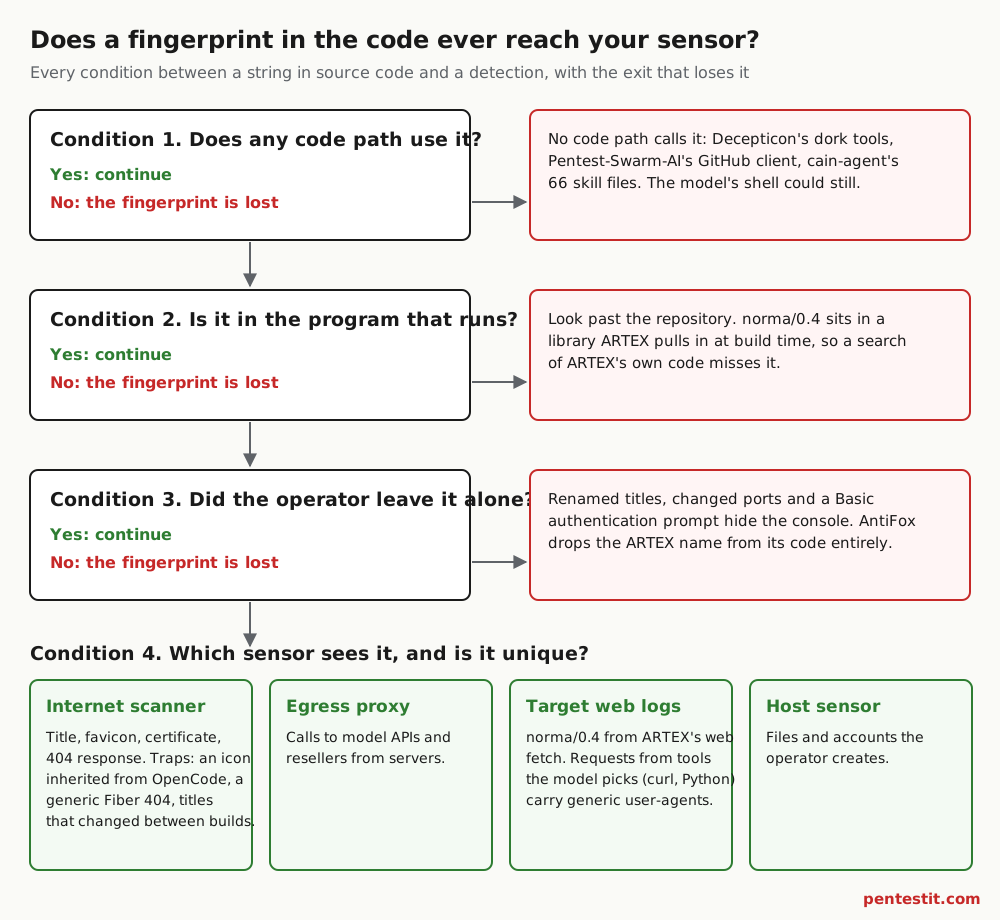
- Pentest-Swarm-AI answers unknown paths with a JSON error whose message reads Cannot GET /. That text comes from the Fiber web framework (Fiber v2.52.12, router.go line 149), so any Fiber application with a similar error handler returns the same body.
- LuaN1aoAgent’s older title, 鸾鸟Agent, left its source code on 21 July 2026. Current builds use 鸾鸟渗透智能体 · Agent Workbench.
- Strix’s favicon hash comes from its logo, and the same file ships inside Cybermes, which carries a copy of Strix.
- CyberStrike’s server defaults to port 4096. Port 8888 appears in its code only as a listener inside its attack skills, so a CyberStrike console on 8888 means an operator chose that port.
Code that exists but is not invoked
Some code is present but no code path calls it, so the framework itself never sends its strings to a network or a log. I confirmed six cases. Pentest-Swarm-AI’s GitHub search client is never constructed outside its own file and tests. cain-agent has 66 top-level files under skills/, and its loader reads only SKILL.md files. CAI ships a ReverseShellClient class with a listener in src/cai/tools/command_and_control/command_and_control.py, and nothing imports that module; CAI’s agents import only its sibling sshpass module, so no CAI code opens the listener. Decepticon’s Ghidra tool has a request helper, _mcp_get, that nothing calls. Decepticon is the instructive case. Its exploiter agent’s docstring says the agent gets the full research tool bundle, which includes the dork tools. The agent’s actual tool list is four lookup tools plus its shell tools, and no agent code uses that bundle. If you write detections from documentation, check them against the code. For the Python repositories I found these with Vulture, a dead-code finder, and then checked each hit manually, because tools that a framework registers by decorator or loads from a folder look unused to it.
The sixth case is ARTEX’s own, and it comes with a warning. ARTEX’s enrichment engine, enrich/enrich.go, fetches a site with the user-agent artex-enrich/1.0, and every worker is handed that engine. Across the full histories of all eight ARTEX-family repositories, no shipped code calls the function that sends that request; the only call is in one ScopeWeaver test. Pojun renamed the string pojun-enrich/1.0 and AntiFox antifox-enrich/1.0. Yet WorkOS listed artex-enrich/1.0 among the strings it saw in its October 2026 incident (Cloud Security Alliance). The agent that reached WorkOS ran a build in which that call exists, and that build is not in any public history I could read. That is the best argument for keeping a string in your hunts even when nothing in the public code calls it.
Uncalled is not the same as impossible. These agents have a shell tool, and the model can run any file on disk with it, such as CAI’s command_and_control.py. Treat these strings as unlikely to appear, and do not build a rule that assumes they never will.
A user-agent that depends on the model provider
CyberStrikeus/CyberStrike sets the user-agent cyberstrike/ followed by its version on requests to its model provider, unless the provider is Anthropic, in which case it sends no user-agent of its own. When the provider is CyberStrike’s own service, it sends X-CyberStrike-Project, X-CyberStrike-Session, X-CyberStrike-Request and X-CyberStrike-Client headers instead. FrancescoStabile/numasec does the same with numasec/ and its version, without the Anthropic exception. Both copied the pattern from OpenCode. A CyberStrike operator who uses Claude never sends that user-agent, so a rule keyed on it misses them.
How many of these consoles are exposed on the internet?
On 13 November 2026, Shodan’s index held 1,558 IP addresses serving ARTEX’s icon and name, 495 carrying PentAGI’s page title, 220 carrying CyberStrikeAI’s title and icon, 145 carrying AntiFox’s and 41 serving Cairn’s console. I searched Shodan with fingerprints from the source code and counted distinct IP addresses, because Shodan’s own totals count services: one server on two ports counts twice. Each framework gets one count, from a query that matches only that framework, and I never add overlapping queries. Every query and both days’ results are in the exposure CSV.
As we know, only some of Shodan’s index is fresh as the data behind these counts is collected in the 30 days before the search, the oldest on 14 October. For ARTEX, 1,404 of 1,807 records were collected in the last seven days, so most of those consoles were up within a week of the search.
IP addresses serving AI pentesting framework consoles, 13 November 2026
A count of IP addresses is not a count of attackers. These frameworks are public, so researchers, red teams, students and honeypots run them too. Treat this as a match as a lead to check against your own logs and not as a verdict. Do send abuse reports to the hosting provider or a national CERT. The country columns in the CSV show where a server is hosted, not who runs it.
Most exposed ARTEX consoles run the original Chinese build
ARTEX’s console title was ARTEX — 自主渗透测试控制台 from its first commit on 26 July 2026 until commit e233c02 translated it to ARTEX — Autonomous Penetration Testing Console on 8 October 2026. On 13 November, the Chinese title was on 1,849 IP addresses and the English one on 136. AntiFox kept the Chinese words in its own title and accounts for 145 of them by icon and name, which still leaves well over a thousand IP addresses serving a build from before the translation.
The split by port comes from Shodan’s count interface a day earlier, on 12 November, which counts services. ARTEX’s icon was on 1,619 services, and 1,070 of them answered on port 8787, ARTEX’s default console port. Another 178 answered on port 8790, which appears in no ARTEX-family code, so I do not know why that port is common. Four repositories besides ARTEX ship the same icon (ScopeWeaver, Pojun and two ARTEX forks), which is why I count the icon only together with ARTEX in the title.
Do forks change what defenders should look for?
Some do. The 66 repositories have 2,333 forks between them, and 43 are at least 20 commits ahead of their parent and were pushed after 1 September 2026. I read the 13 strongest forks of the six frameworks with reported use and compared each fork’s changes with the fingerprints in this post.
| Fork | What it adds | What changes for detection |
|---|---|---|
| Shennnnnnnnnn/Cairn | A rebuilt Node server and more harness integrations | The uvicorn server and the –port default of 8000 are gone, and the exact title Cairn becomes titles such as Cairn · goal. A search for the title Cairn plus the uvicorn server header misses it. |
| rightevil/Cairn | A portable desktop tray application | The desktop build requires the server on 127.0.0.1:8000, so a default install is not internet-facing. |
| AnkioTomas/strix | A web console with emailed and exported reports | A new page titled Strix with its own favicon route, a fingerprint the upstream project does not have. |
| angelosk/hexstrike-ai | Security fixes, optional API token authentication and a Docker stack | Adds the user-agent Mozilla/5.0 (Windows NT 10.0; Win64; x64) HexStrike/7.0. With a token set, probes of port 8888 no longer reach the API. |
| zSkallywag/pentagiSLM | Support for small local language models; syncs with upstream daily | Keeps every PentAGI fingerprint. A local model means no traffic to a model provider. |
| wxcvm/ARTEX | A Windows desktop build and Markdown report export | Adds a user-agent override for model-provider requests only. Web fetch still sends norma/0.4 through BaaRai’s norma v0.4.4. |
| ramon-victor/CyberStrikeAI | An English translation and a Burp Suite plugin | Adds the user-agents CyberStrikeAI/1.7.11 and CyberStrikeAI-Docker-build. |
| samirhvbr/strix | 240 commits of maintenance, including masking of credentials in its activity view | No change to the Strix fingerprints. |
Do GitHub stars tell you whether a framework is trustworthy?
No. Across the 66 repositories, the rank correlation between stars and four provenance signals combined is 0.21, which is weak. The signals: whether the code is original, owner account age, organization status and commits signed with the committer’s own key. I publish them as facts per repository and not as a ranking, because a ranking of offensive tools tells a defender nothing useful.
To let you recompute the correlation, the repositories CSV has the points behind each signal. Origin: 10 for original code, 8 for code that reuses another project, 6 for code derived from an upstream that is gone, 4 for a copy with changes. Signing: 5 for any own-key signed commit among the latest 100. Owner age: 5 for an account a year or older, 3 for a younger one. Organization: 5 for a verified organization, 3 for any other organization, 2 for a user who belongs to a public organization. They add up to a maximum of 25.
Provenance signals across 66 repositories
Account age barely separates these projects, because 56 of the 66 owners are older than a year. Signing does. Only 11 repositories have any own-key signed commit among their latest 100. Among the seven frameworks with confirmed breaches, only PentAGI signs, with 93 of its latest 100 commits. AntiFox’s owner account is 34 days old and none of its commits are signed.
What should defenders hunt for first?
- The “User-Agent: norma/0.4” in web server and proxy logs, for anything built on norma, which includes every ARTEX copy and AntiFox.
- Exposed consoles, using fingerprints that exist in the code: ARTEX’s favicon hash -1898746557 with ARTEX in the title, CyberStrikeAI’s favicon hash -1349384020 with its title, the string intentChipGlow for Cairn, PentAGI’s favicon hash -1596753120 and its PentAGI CA certificate issuer, and RedAmon’s favicon hash 964522141. Run these against your own address space first. Expect renamed builds and forks to miss them: one Cairn fork drops the exact Cairn title and the uvicorn server, and a Strix fork adds a console titled Strix.
- Model API traffic from servers that should not call a model. Zscaler lists DeepSeek, Zhipu, xAI and Anthropic API endpoints in the ARTEX campaign it studied. A PentAGI fork built for small local models sends none.
- User-agents from forks as well as originals: Mozilla/5.0 (Windows NT 10.0; Win64; x64) HexStrike/7.0 from a HexStrike AI fork, and values starting with CyberStrikeAI/ from CyberStrikeAI and its forks.
- Campaign artifacts from the reports, treated as campaign artifacts: ArtexProbe accounts, artex-probe-* files and webhook.site traffic. They are not in ARTEX’s code, so the next campaign can drop them.
- ARTEX’s enrichment “User-agent artex-enrich/1.0“, and its renamed forms pojun-enrich/1.0 and antifox-enrich/1.0. No public build calls the code that sends it, but WorkOS saw it in a real incident.
For behavior-based rules, MalwareMustDie published an ARTEX detection pack for Sigma, KQL, Suricata, Snort, osquery and YARA under the Detection Rule License (MalwareMustDie). Its behavior rules, such as machine-speed recon chains and self-correcting retries, complement the code fingerprints here. Check its tiers against the code before acting on them. Several strings it rates as unique to ARTEX, among them Mozilla/5.0 (ARTEX), ArtExVerify/1.0 and X-ARTX-KEY, appear in none of the eight public ARTEX-family histories, and its realm=”ARTEX” login header comes from the ycode fork, not from ARTEX. Treat those as campaign indicators that the next operator can change.
Sigma rule
To get you started, here are a couple of rules I authored:
- norma Agent Library Web Fetch User-Agent (ARTEX Family) in Proxy Logs – https://github.com/mayur-esh/sigma-rules/blob/main/generic/proxy_artex_norma_useragent.yml
- norma Agent Library Web Fetch User-Agent (ARTEX Family) in Web Server Logs – https://github.com/mayur-esh/sigma-rules/blob/main/generic/web_artex_norma_useragent.yml
- ARTEX Family Enrichment User-Agent in Web Server Logs – https://github.com/mayur-esh/sigma-rules/blob/main/generic/web_artex_enrich_useragent.yml
- ARTEX Family Enrichment User-Agent in Proxy Logs – https://github.com/mayur-esh/sigma-rules/blob/main/generic/proxy_artex_enrich_useragent.yml
All 67 AI pentesting frameworks in this study
Grouped by evidence, sorted by name within each group. Stars and owner data are from the GitHub API between 9 and 12 November 2026. Expand a group to see its rows.
Reported use (10)
| Repository | Language | Stars | Commit history | Origin | Owner account | Own-key signed commits (latest 100) | Abuse evidence |
|---|---|---|---|---|---|---|---|
| 0x4m4/hexstrike-ai | Python | 13,483 | 2025-07-10 to 2026-08-03 | Original | User, 3.7 years | 0 of 63 | Used in a campaign with confirmed breaches |
| agent0ai/agent-zero | Python | 19,814 | 2024-06-10 to 2026-11-01 | Original | Organization, 1.4 years; repository is older than this account | 0 of 100 | Threat actor experimentation reported |
| AIPentest/CyberStrikeAI | Go | 8,520 | 2025-11-08 to 2026-11-08 | Original | Organization, 63 days; repository is older than this account | 0 of 100 | Used in a campaign with confirmed breaches |
| AntiFox-AI/antifox | Go | 561 | 2026-10-12 to 2026-10-31 | ARTEX code under a new name | User, 34 days | 0 of 11 | Used in a campaign with confirmed breaches |
| BaaRai/ARTEX | Go | 1,891 | 2026-07-26 to 2026-11-09 | Translation fork of the removed ARTEX upstream | User, 3.6 years | 0 of 100 | Used in a campaign with confirmed breaches |
| GreyDGL/PentestGPT | Python | 16,355 | 2023-02-27 to 2026-07-14 | Original | User, 5.8 years | 2 of 100 | A malicious build derived from it was used |
| oritera/Cairn | Python | 5,006 | 2026-04-19 to 2026-09-07 | Original | Organization, 205 days | 0 of 70 | Used in a campaign with confirmed breaches |
| samugit83/redamon | Python | 3,351 | 2025-12-29 to 2026-11-09 | Original | User, 3.8 years | 0 of 100 | Seen on hosts that run ARTEX |
| usestrix/strix | Python | 74,719 | 2025-08-08 to 2026-11-10 | Original | Organization, 2.0 years | 0 of 100 | Used in a campaign with confirmed breaches |
| vxcontrol/pentagi | Go | 33,816 | 2026-03-26 to 2026-10-23 | Original | Verified organization, 8.5 years | 93 of 100 | Used in a campaign with confirmed breaches |
Other ARTEX-family copies (6)
| Repository | Language | Stars | Commit history | Origin | Owner account | Own-key signed commits (latest 100) | Abuse evidence |
|---|---|---|---|---|---|---|---|
| 2561769445/ycode-auto-pentest | Go | 9 | 2026-10-26 to 2026-10-27 | ARTEX family (84% of lines from the original) | User, 4.0 years | 0 of 3 | None found |
| acheong08/artex | Go | 5 | 2026-07-26 to 2026-10-09 | ARTEX family (86% of lines from the original) | User, 8.8 years | 0 of 100 | None found |
| chu0119/Pojun | Go | 92 | 2026-07-26 to 2026-11-07 | ARTEX family (75% of lines from the original) | User, 6.4 years | 0 of 100 | None found |
| cskwork/scopeweaver | Go | 955 | 2026-07-26 to 2026-11-04 | ARTEX family (50% of lines from the original) | User, 5.9 years | 0 of 100 | None found |
| F0ran9/forang | Go | 9 | 2026-10-28 to 2026-11-09 | ARTEX family (76% of lines from the original) | User, 4.6 years | 0 of 100 | None found |
| ijlalhaider313/ARTEX | Go | 0 | 2026-07-26 to 2026-10-11 | ARTEX family (78% of lines from the original) | User, 3.9 years | 0 of 100 | None found |
No public abuse evidence found (50)
| Repository | Language | Stars | Commit history | Origin | Owner account | Own-key signed commits (latest 100) | Abuse evidence |
|---|---|---|---|---|---|---|---|
| 0xrdi/echidna | Python | 5 | 2026-08-08 to 2026-08-08 | Original | User, 4.1 years | 0 of 2 | None found |
| 0xSteph/pentest-ai | Python | 1,819 | 2026-04-04 to 2026-11-03 | Original | User, 351 days | 0 of 100 | None found |
| 0xSteph/pentest-ai-agents | Shell | 2,433 | 2026-03-28 to 2026-08-16 | Original | User, 351 days | 0 of 56 | None found |
| aielte-research/HackSynth | Python | 321 | 2024-11-27 to 2025-06-24 | Original | Organization, 6.7 years | 1 of 5 | None found |
| aliasrobotics/cai | Python | 9,854 | 2026-08-22 to 2026-08-22 | Original | Organization, 9.7 years | 0 of 1 | None found |
| antoninoLorenzo/AI-OPS | Python | 171 | 2024-06-08 to 2026-10-14 | Original | User, 5.0 years | 0 of 100 | None found |
| Armur-Ai/Pentest-Swarm-AI | Go | 3,173 | 2024-04-17 to 2026-11-03 | Original | Verified organization, 3.9 years | 0 of 100 | None found |
| arthurgervais/mapta | HTML | 129 | 2025-08-28 to 2025-08-28 | Original | User, 12.2 years | 0 of 2 | None found |
| ASCIT31/Dark-Moon | Python | 1,212 | 2025-10-29 to 2026-10-27 | Original | Organization, 5.1 years | 2 of 100 | None found |
| berylliumsec/nebula | Python | 1,154 | 2023-09-30 to 2026-11-09 | Original | Organization, 4.3 years | 0 of 100 | None found |
| bhavsec/autopentest-ai | Python | 248 | 2026-02-11 to 2026-02-22 | Original | User, 11.4 years | 0 of 11 | None found |
| BitterSecurity/Decepticon | Python | 6,575 | 2026-03-18 to 2026-11-09 | Original | Organization, 1.5 years | 0 of 100 | None found |
| bugbasesecurity/pentest-copilot | TypeScript | 1,555 | 2025-03-16 to 2026-08-14 | Original | Organization, 5.0 years | 0 of 98 | None found |
| BugTraceAI/BugTraceAI | Shell | 371 | 2026-02-11 to 2026-10-19 | Original | Organization, 340 days | 0 of 100 | None found |
| cdxiaodong/cain-agent | Python | 946 | 2026-03-18 to 2026-10-14 | Original | User, 5.5 years | 0 of 100 | None found |
| chainreactors/cyber-harness | Go | 397 | 2026-05-08 to 2026-11-09 | Original | Organization, 4.6 years | 0 of 100 | None found |
| CyberStrikeus/CyberStrike | TypeScript | 3,489 | 2025-03-21 to 2026-11-09 | Built on OpenCode's history | Organization, 285 days | 0 of 100 | None found |
| cylabcyberautonomy/Incalmo | Python | 149 | 2025-05-05 to 2026-11-02 | Original | Organization, 249 days; repository is older than this account | 0 of 100 | None found |
| Dizzy-K/AutoPT | Python | 50 | 2026-03-28 to 2026-06-01 | Original | User, 7.1 years | 0 of 95 | None found |
| dreadnode/ares | Rust | 103 | 2026-04-15 to 2026-10-28 | Original | Verified organization, 16.3 years | 0 of 100 | None found |
| Echidna-Pentest/Echidna | JavaScript | 65 | 2023-07-31 to 2025-08-24 | Original | Organization, 3.4 years | 0 of 100 | None found |
| elder-plinius/T3MP3ST | TypeScript | 6,999 | 2026-07-02 to 2026-09-07 | Original | User, 3.5 years | 13 of 100 | None found |
| FrancescoStabile/numasec | TypeScript | 834 | 2026-02-06 to 2026-05-09 | Built on OpenCode code (single import) | User, 4.5 years | 0 of 100 | None found |
| gadievron/raptor | Python | 3,991 | 2025-11-21 to 2026-11-09 | Original | User, 1.3 years | 100 of 100 | None found |
| GH05TCREW/pentestagent | Python | 3,276 | 2025-05-15 to 2026-11-08 | Original | User, 2.1 years | 1 of 100 | None found |
| ipa-lab/hackingBuddyGPT | Python | 1,316 | 2023-04-26 to 2026-10-24 | Original | Organization, 7.0 years | 1 of 100 | None found |
| irraz/vulnerator-ai | Python | 274 | 2026-10-14 to 2026-11-09 | Original | User, 6.5 years | 0 of 100 | None found |
| JoasASantos/NeuroSploit | Rust | 1,518 | 2025-08-16 to 2026-11-09 | Original | User, 8.9 years | 0 of 100 | None found |
| JuliusHenke/autopentest | Python | 75 | 2024-06-06 to 2026-08-22 | Original | User, 10.0 years | 93 of 100 | None found |
| KeygraphHQ/shannon | TypeScript | 51,588 | 2025-10-03 to 2026-11-06 | Original | Organization, 2.1 years | 0 of 100 | None found |
| KHenryAegis/VulnBot | Python | 223 | 2025-01-20 to 2026-11-08 | Original | User, 7.1 years | 0 of 9 | None found |
| martian56/redcell | Python | 358 | 2026-08-02 to 2026-10-06 | Original | User, 3.0 years | 0 of 100 | None found |
| MythicAgents/sage | Python | 36 | 2025-04-03 to 2026-10-23 | Original | Organization, 6.1 years | 100 of 100 | None found |
| N1nEmAn/sapper-v2 | Python | 1,809 | 2026-10-30 to 2026-11-09 | Original | User, 4.0 years | 0 of 18 | None found |
| pensarai/apex | TypeScript | 324 | 2025-10-07 to 2026-11-09 | Original | Organization, 3.4 years | 0 of 100 | None found |
| PentesterFlow/agent | TypeScript | 1,448 | 2026-05-31 to 2026-08-31 | Original | User, 1.1 years | 0 of 53 | None found |
| pikpikcu/airecon | Python | 1,089 | 2026-03-05 to 2026-10-11 | Original | User, 6.8 years | 0 of 100 | None found |
| r74tech/virga | Go | 8 | 2025-12-10 to 2026-11-09 | Original | User, 7.0 years | 0 of 44 | None found |
| s0ld13rr/pentestcode | TypeScript | 946 | 2026-07-08 to 2026-11-05 | Built on OpenCode code (single import) | User, 6.3 years | 0 of 100 | None found |
| SanMuzZzZz/LuaN1aoAgent | TypeScript | 1,468 | 2025-12-05 to 2026-09-15 | Original | User, 5.3 years | 0 of 100 | None found |
| SHAdd0WTAka/Zen-Ai-Pentest | Python | 504 | 2026-01-29 to 2026-08-01 | Original | User, 1.4 years | 0 of 100 | None found |
| Stanford-Trinity/ARTEMIS | Rust | 550 | 2025-11-29 to 2025-12-31 | Original | Organization, 1.3 years; repository is older than this account | 1 of 4 | None found |
| stratosphereips/aracne | Python | 19 | 2025-10-17 to 2026-06-17 | Original | Verified organization, 11.8 years | 0 of 12 | None found |
| straylabs-ai/deadend-cli | Python | 327 | 2025-07-22 to 2026-08-07 | Original | Organization, 298 days; repository is older than this account | 0 of 100 | None found |
| Vasco0x4/AIDA | JavaScript | 509 | 2026-01-31 to 2026-09-15 | Original | User, 6.6 years | 0 of 100 | None found |
| xalgorix/xalgorix | Go | 1,323 | 2026-03-30 to 2026-11-08 | Original | Organization, 102 days; repository is older than this account | 0 of 100 | None found |
| YasodGinige/AutoPentester | Python | 94 | 2023-02-27 to 2026-09-25 | Fork of PentestGPT by history (11.8% of lines still shared) | User, 8.7 years | 0 of 100 | None found |
| yohannesgk/blacksmith | TypeScript | 269 | 2025-12-24 to 2026-10-23 | Original | User, 3.7 years | 0 of 59 | None found |
| zakirkun/guardian-cli | Python | 1,935 | 2025-12-22 to 2026-06-28 | Original | User, 6.7 years | 0 of 38 | None found |
| Zyrexnn/Cybermes | Python | 1,013 | 2026-08-19 to 2026-09-16 | Original | User, 2.3 years | 0 of 100 | None found |
Not on GitHub (1)
| Framework | Where it is distributed | Releases | Listener in the shipped code | Abuse evidence |
|---|---|---|---|---|
| Villager (Cyberspike) | PyPI package villager | 19 releases, 23 July to 15 September 2025 | Port 37695, all interfaces | None found; Straiker reports no confirmed threat actor use |
Download the full data: all 66 repositories (CSV), the 58 fingerprints found in source code (CSV), the 60 Shodan exposure counts (CSV) and the 13 forks I read (CSV).
Frequently asked questions
What is an AI pentesting framework?
An AI pentesting framework is software that lets a language model plan and run penetration testing steps, such as scanning, testing for vulnerabilities and exploiting them, with little human input. Many wrap existing tools such as nmap and sqlmap. The 67 in this post are public: 66 on GitHub and one on PyPI, so attackers can download them too.
Which open-source AI pentesting frameworks have attackers used?
Primary reporting ties seven to campaigns with confirmed breaches: ARTEX, Cairn, PentAGI, CyberStrikeAI, HexStrike AI and Strix. Google and Mandiant name HexStrike AI among frameworks seen in incident response. CrowdStrike reports a malicious framework derived from PentestGPT. I found no public abuse reporting for 56 of the 66 repositories I checked.
What is the norma/0.4 user-agent?
norma/0.4 is the user-agent the norma agent library sets on web fetch requests. ARTEX depends on norma, so ARTEX, its forks and the renamed copy AntiFox send it when their agent fetches a page. Wiz reported it in Storm-0940 activity. Any other agent built on norma would send it too, so treat a hit as a norma-based agent.
What is AntiFox?
AntiFox is an AI pentesting platform on GitHub whose code is ARTEX’s under a new name. About 59% of its distinctive code lines come from the original ARTEX, and it carries ARTEX’s norma library in a renamed folder and sends the same norma/0.4 user-agent. Arctic Wolf tied hosts running it to intrusions that reached a production AWS secret.
How many ARTEX consoles are exposed on the internet?
On 13 November 2026, Shodan’s index held 1,558 IP addresses serving ARTEX’s icon with ARTEX in the page title, most on port 8787. 1,849 addresses carry the original Chinese console title and 136 the English title added on 8 October 2026, so most exposed consoles run a build from before the translation.
Can I find exposed PentestCode servers with favicon hash -196523122?
Not on its own. The icon behind that hash is OpenCode’s, and PentestCode serves it unchanged through the same symbolic link OpenCode uses. A favicon search therefore also finds other web interfaces built on OpenCode. Pair the hash with PentestCode’s page title before you treat a match as PentestCode.
Do GitHub stars show whether an AI pentesting framework is trustworthy?
No. Across 66 repositories, the rank correlation between stars and four provenance signals combined is 0.21, which is weak. Only 11 repositories have any commit signed with the committer’s own key among their latest 100. Check lineage, owner history and signing directly instead of reading stars.
Do forks of AI pentesting frameworks change their fingerprints?
Some do. One Cairn fork drops the exact Cairn page title and the uvicorn server that a title search relies on. A Strix fork adds a web console titled Strix, and a HexStrike AI fork adds its own user-agent. The ARTEX forks I checked still send norma/0.4, so that hunt still works.
Why do some fingerprints in framework code rarely show up in logs?
Some code ships with a framework but no code path calls it, so the framework never sends its strings. I confirmed six such cases. The model can still run those files through its shell tool, so treat them as unlikely, not impossible. Other fingerprints break when an operator renames a console or changes its port.
https://pentestit.com/ai-pentesting-frameworks-abuse-lineage-fingerprints/
Published: 2026 11 14 20:48:23
Received: 2026 11 20 07:48:29
Feed: PenTestIT
Source: PenTestIT
Category: News
Topic: Security Tooling
Views: 3
