Cyber Security News Aggregator
.Cyber Tzar
provide acyber security risk management
platform; including automated penetration tests and risk assesments culminating in a "cyber risk score" out of 1,000, just like a credit score.
First slide label
Some representative placeholder content for the first slide.
Second slide label
Some representative placeholder content for the second slide.
Third slide label
Some representative placeholder content for the third slide.
sshole (CVE-2026-123158): OpenSSH musl Password Bypass Root Cause, Detection and Mitigation
published on 2026-11-06 07:29:14 UTC by MayureshContent:
CVE-2026-123158 (“sshole”) lets an unauthenticated attacker log into any OpenSSH account whose /etc/shadow password field is exactly * by sending a 257 to 1024 byte password. It only works when sshd is linked against musl libc, runs without PAM, has PasswordAuthentication yes, and at least one other local account holds a $5$ or $6$ hash. Fix: OpenSSH 10.6p2 or your distribution backport, then restart sshd.
Upgrading the package does not replace the running daemon. Restart sshd, then confirm with readlink /proc/<sshd pid>/exe that the binary is not marked (deleted).
CVE-2026-123158 at a glance
This CVE was published 2026-11-05 by MITRE as CNA. These are the details:
| Field | Value |
|---|---|
| Type and CWE | Password authentication bypass. MITRE: CWE-394 (Unexpected Status Code or Return Value). Red Hat: CWE-303 (Incorrect Implementation of Authentication Algorithm). |
| CVSS v4 | None published by MITRE, NVD, GitHub or Red Hat. I do not know the v4 vector. |
| CVSS v3.1 | 8.1 High, CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H. Network reachable, no credentials, no user action, full impact. AC:H reflects that the account and hash layout on the target must line up. |
| CISA SSVC (Vulnrichment) | Exploitation: active (changed from poc on Nov 9, 2026). Automatable: no. Technical Impact: total. |
| Precondition | musl libc sshd, no PAM (or UsePAM no), PasswordAuthentication yes, a reachable account with shadow field *, and a separate account with a $5$/$6$ hash. |
| Exploited in the wild | Yes. GreyNoise saw the first attempt on Nov 5 at 18:34 UTC and the first success on Nov 7 at 00:46 UTC, on its own sensors; no real organization is confirmed compromised. In CISA KEV since Nov 9, 2026 (catalogVersion 2026.11.10). The BOD 26-04 due date was Nov 12, 2026, with forensic triage required. Known ransomware use: unknown. |
| Fixed builds | Upstream OpenSSH 10.6p2. Alpine: edge 10.6_p2-r0, 3.24 10.3_p1-r2, 3.23 10.2_p1-r1, 3.22 10.0_p1-r11, 3.21 9.9_p2-r1, 3.20 9.7_p1-r6, 3.19 9.6_p1-r3, 3.18 9.3_p2-r4, 3.17 9.1_p1-r7, 3.16 9.0_p1-r6. |
| Vendor workaround | PasswordAuthentication no and restart sshd, or use openssh-server-pam with UsePAM yes. |
CISA’s KEV listing requires forensic triage, not only patching. Before you upgrade or restart a host that had password logins on, copy /var/log/messages* and the authorized_keys files.
In brief, these are the affected software and platforms:
Alpine host running openssh-server
- sshd linked against musl, built without PAM
- PasswordAuthentication yes (OpenSSH default)
- an account with shadow field *
- another account with a $5$ or $6$ hash
Exploitable
Any password of 257 to 1024 bytes logs in as the * account
Patch and restart today
Debian, Ubuntu, RHEL with PAM
- glibc or libxcrypt never return a bare *
- PAM handles the password check
Not affected
Vendor statements and the OpenSSH release say not affected
No action for this CVE
- The Alpine tiny-cloud
alpineuser becomes root. Official AWS, Azure and qcow2 tiny-cloud images from 3.18.11 through 3.24.3 shipalpinewith a*field and passwordlessdoas. They are safe until any$6$hash is added to the box, for example a console password or ahashed_passwdin user-data. After that, one connection gives a shell, anddoasgives root. - “Patched” may still mean vulnerable. Hosts upgraded in April 2026 to OpenSSH 10.3 for the certificate principals bypass (CVE-2026-35414) are still exposed here, as is upstream 10.6p1. Only 10.6p2 or the Alpine revisions in the table are fixed. Spectrum reports that
apk upgrade opensshupgrades only the meta-package and leavesopenssh-serverat the vulnerable revision; Alpine’s advisory usesapk upgrade -U -a. - Logs show a normal login. sshd never logs password length. The only host signal is
Accepted password for <user>where<user>has no password. If the attacker reached root throughdoas, they can edit/var/log/messages.
Components: sshd password path in auth-passwd.c and openbsd-compat/xcrypt.c. musl crypt() SHA-256/SHA-512 backends. Endpoint: SSH userauth “password” method on the listening port. Embedded Buildroot, Yocto and OpenWrt builds: affected only if they ship OpenSSH (not Dropbear), without PAM, with matching accounts.
Root cause: sys_auth_passwd() compares a musl error string to a shadow sentinel
The bug is a collision of one byte. musl’s crypt() returns "*" on failure, and * is also what /etc/shadow stores for an account with no password. sys_auth_passwd() in auth-passwd.c compares the two with strcmp() and accepts.
- The client sends a password-method userauth request.
auth_password()rejects anything overMAX_PASSWORD_LEN(1024) and passes the rest tosys_auth_passwd(). That cap is why the window ends at 1024 bytes. shadow_pw()returns the target’s stored field,*. It is too short to hold a salt, so sshd asksxcrypt()to pick one.xcrypt()callspick_salt(), added in 2016 for the user-enumeration timing fix (CVE-2016-6210). It walks the password database and borrows the salt from the first$-style hash.- With a
$5$or$6$salt, musl routes to its SHA-crypt code, which caps the key atKEY_MAX256 bytes. A 257 byte or longer key fails, and musl returns"*". strcmp("*", "*") == 0. Authentication succeeds.
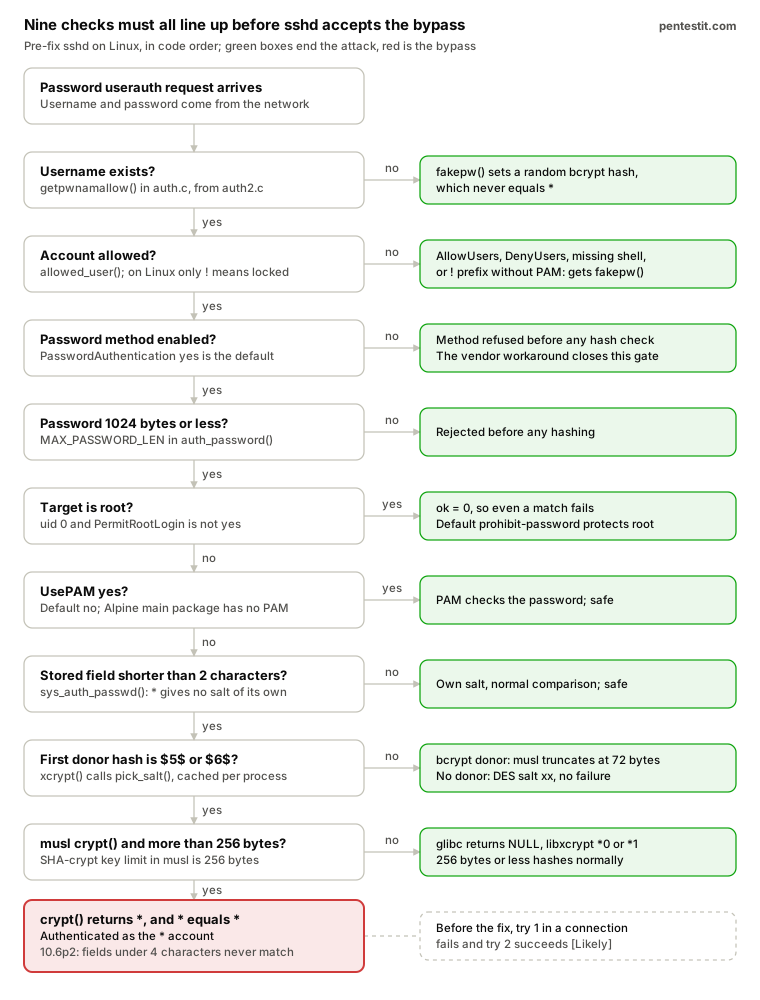
Why it breaks only here: glibc returns NULL and libxcrypt returns "*0"/"*1", not just "*". With PAM active, sshd never calls sys_auth_passwd(). A ! field, or !$6$…, never equals *. If the first borrowed hash is bcrypt, musl truncates at 72 bytes instead of failing.
CVE-2026-123158 patch (commit 4353fdc)
This patch spans across three files, 34 additions and 17 deletions.
/* auth-passwd.c */
+#define MIN_PASSWORD_HASH_LEN 4
 #define MAX_PASSWORD_LEN 1024
 ...
-  char *pw_password = authctxt->valid ? shadow_pw(pw) : pw->pw_passwd;
+  char *pw_password = authctxt->valid ?
+      shadow_pw(pw) : xstrdup(pw->pw_passwd);
 ...
-  return encrypted_password != NULL &&
+  ret = encrypted_password != NULL &&
+      strlen(pw_password) >= MIN_PASSWORD_HASH_LEN &&
       strcmp(encrypted_password, pw_password) == 0;
+  freezero(pw_password, strlen(pw_password));
+  return ret;

/* openbsd-compat/xcrypt.c, shadow_pw() */
-  return pw_password;
+  return pw_password == NULL ? NULL : xstrdup(pw_password);
This patch introduces two changes. First, a stored field shorter than 4 characters can never match, so *, !, !! and *0 are dead. Second, shadow_pw() now returns a heap copy instead of a pointer into libc’s static getspnam() buffer, and pick_salt() frees each copy. openbsd-compat/port-uw.c gets the same copy-and-free change. The commit message says OpenSSH does not consider the root cause to be inside OpenSSH. The CWE-394 assignment is confirmed as the caller did not handle a legitimate but unexpected return value.
Attack path: from a port scan to root
The attack needs one guessed username and two password tries in the same connection. The rest of the chain is ordinary Alpine cloud-image behavior.
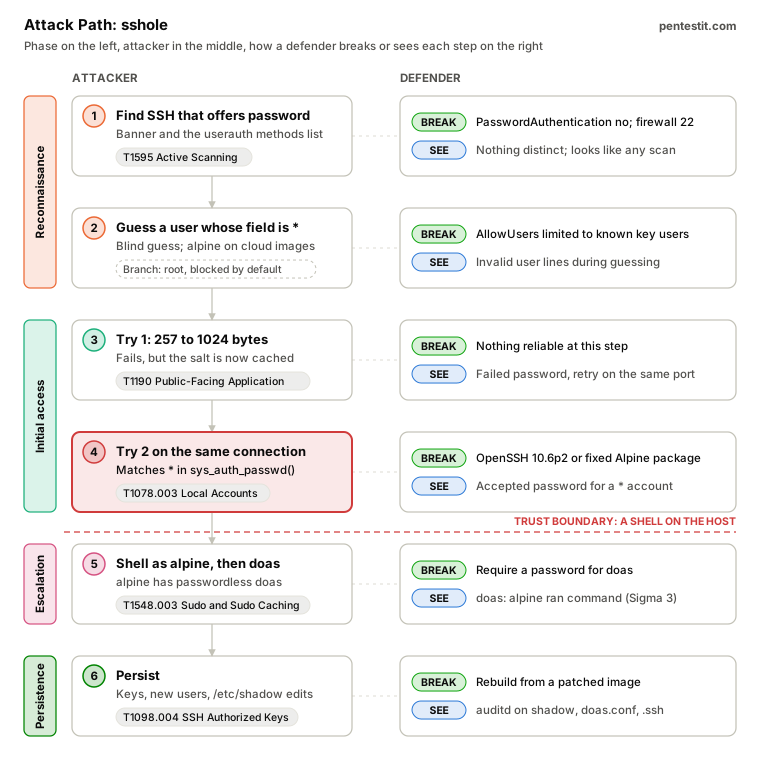
An attacker cannot fingerprint the vulnerable conditions from outside as the banner gives only OpenSSH version. Alpine builds carry no distribution suffix, but neither do upstream, Fedora or Arch builds, so “no suffix” is a weak hint. The only useful remote signal is whether password appears in the methods list the server returns after a failed none request (RFC 4252, section 5.1). musl, PAM and the shadow layout are invisible from the network, so the attack is a blind guess: a likely * username plus an over-length password. That makes it cheap to spray and makes the host log the best place to catch it.
Why two tries? I read the pre-fix source. pick_salt() calls shadow_pw() for other accounts and then zeroes the donor hash with explicit_bzero(), while pw_password still points into libc’s shadow buffer. The salt is cached in a static variable, so the second try in the same connection skips the scan and compares against an intact *. Default MaxAuthTries is 6, so the second try is allowed.
Root is not a target by default. auth_password() forces ok = 0 for uid 0 unless PermitRootLogin yes, and the default is prohibit-password. A * account whose shell is /sbin/nologin still passes allowed_user(), which only checks that the shell exists and is executable. With AllowTcpForwarding at its default, it could still serve as a tunnel.
Reachability: what must be true for the bypass to fire
A packet reaches the vulnerable strcmp() only if all nine checks go the attacker’s way. Any green exit means that host is not exploitable through that path.
Detect CVE-2026-123158
These were a few approaches I think can help detect exploitation attempts. Some rules definitely need correlation and will need baselining.
- Sigma rule 1: password login to an account with no password
- Sigma rule 2: Failed then Accepted pair (correlation)
The correlation groups onsrc_ipanduser. Your SIEM must extract those fields from the syslog line; keyword rules alone do not create them. Raise it to high when the user is in the*list. - Sigma rule 3: doas by the cloud-image user
Which public sshole poc repositories are safe to run, and which work?
Short answer: I graded 49 public GitHub repositories for CVE-2026-123158 with my repository reliability score (v2.3). 31 ship an attack client or lab, so they get a safety status only and no score. 18 are defensive. Three carry a caution. One scanner cannot start, and the most-starred repositories are exploits. The method is the same as in my earlier PHP2Shell scoring post: score = 50 content + 30 provenance + 20 hygiene, capped at 100 × content + 20, compared within a class only. Exploit, lab and crash repositories are never scored or ranked. No repository code was run. Every number below is static, with no lab.
sshole repositories by class
Scores by class
Scores compare inside a particular class only. A plain document page earns points for stating facts by default where as a scanner earns them for giving a right answer. Putting them on one list would mislead readers.
Scanner and checker scores (static)
Details now:
| Repository Name | Class | Score | Class percentile | Content / Provenance / Hygiene | Reasoning |
|---|---|---|---|---|---|
| mlazzarotto/ansible-sshole-remediate | Patch | 56 | 100 | 27.8 / 15 / 13.3 | Installs the fixed package; no tests; CI actions not pinned |
| coboliqcom/cve-2026-123158-sshole-safe-rust | Patch | 47 | 50 | 16.7 / 15 / 15 | Its C diff shares none of the 34 changed lines in 4353fdc; has tests |
| mc493/openssh-musl-enterprise–hardening-cve-2026-123158 | Mitigation | 78 | 100 | 50 / 15 / 13.3 | Sets PasswordAuthentication no, notes the restart, points to the patch |
| Certbn/CVE-2026-123158-OpenSSH-sshd-SSHhole-sshole- | Docs | 85 | 100 | 50 / 15 / 20 | Fixed versions, both conditions, patch |
| ansonhsu-ai/sshhole-cve-2026-123158-ste | Docs | 85 | 100 | 50 / 15 / 20 | Same |
| techtaek77/sshole-guide | Docs | 85 | 100 | 50 / 15 / 20 | Same |
The weights check holds. Re-ranking under 70/20/10, 40/40/20, 40/30/30 and equal weights gives Spearman correlations of 0.94, 1.00, 0.99 and 0.99 with 50/30/20. All are above 0.9, so the weights do not drive the order for this CVE.
Installed-package checkers
- 10 of 12 scanners read the host, image or Dockerfile and never log in mid: Static scores sit between 55 and 65, a 10-point spread low: All 10 cite the fixed versions outcome: Without a lab they are indistinguishable on accuracy. Pick by what they read: apk database, shadow field, UsePAM and libc.
Use, after reading the script
Remote login probes
- CriticalWombat sends a 300-byte all-A password twice on one connection high: A positive result is a real login to a * account high: rothoma2 imports ssh_scanner, which the repository does not contain outcome: One probe is an exploit with a report printer. The other cannot start.
Do not point at hosts you do not own
CVE-2026-123158 indicators of compromise
These come from vendor sensors and honeypots, not from victim networks. Attacker addresses rotate, so treat them as hunting leads for the days around Nov 5 to 9, not as a blocklist. GreyNoise says its sightings are not representative of all sshole activity. [Certain that the vendors report them]
| Indicator of Compromise | Type | Type | Notes |
|---|---|---|---|
| 20.255.63.133, 209.248.50.17, 183.220.91.15, 20.2.81.241, 47.80.65.43, 79.116.138.30 | Attacker IP addresses, confirmed post-exploitation | GreyNoise | Six addresses behind 16 successful chains |
| 43.224.227.158 | First tagged exploit attempt, Nov 5 18:34 UTC | GreyNoise | Attempt only |
| tac.vpnla.org | C2 domain for the “TAC Agent” implant | GreyNoise | Block the domain. It resolves to 104.21.88.83, a shared Cloudflare address, so do not block that IP |
| 55e6384f6d1648be9b48fb899e46623e9c05eb0df2cbf95f6701680d4e7cbc2a | SHA-256 of the implant | GreyNoise | Python agent with comments in Chinese; no built-in persistence |
| /opt/py3/tac_agent.py, /etc/init.d/tac-agent, /tmp/apk_repos | Files | GreyNoise | The init script gives the implant persistence through OpenRC |
| Extra sshd on port 2222; C2 domain pinned in /etc/hosts; DNS settings changed | Behavior | GreyNoise | Also cloud metadata queries and reading /etc/shadow and root keys through doas |
| 146.75.26.132 | Alpine package mirror | GreyNoise | Benign. Attackers fetched packages from it; do not block |
| 156.238.252.37:8000 serving /bot.x86_64, saved as /tmp/b | Botnet dropper | SANS ISC | Came from buggy brute-force scripts that started on Nov 1, before sshole was public. Not confirmed as sshole exploitation |
| Passwords made entirely of the letter A | Attempt pattern | SANS ISC | Seen in honeypots that record passwords. A real sshd never logs the password, so this does not help on your hosts |
Read-only host checks for the GreyNoise artifacts (BusyBox syntax, run as root):
ls -la /opt/py3/tac_agent.py /etc/init.d/tac-agent /tmp/apk_repos /tmp/b 2>/dev/null
sha256sum /opt/py3/tac_agent.py 2>/dev/null   # match: 55e6384f6d16...e7cbc2a
grep -n 'vpnla' /etc/hosts /etc/resolv.conf 2>/dev/null
rc-update show 2>/dev/null | grep -i tac
netstat -tlnp 2>/dev/null | grep ':2222 '
ps -o pid,user,args | grep -E 'tac_agent|sshd.*2222' | grep -v grep
grep -hE '(20\.255\.63\.133|209\.248\.50\.17|183\.220\.91\.15|20\.2\.81\.241|47\.80\.65\.43|79\.116\.138\.30|43\.224\.227\.158)' /var/log/messages* 2>/dev/null
Patch sshole
Upgrade, then restart the daemon.
apk upgrade -U -a
rc-service sshd restart
Fixed openssh packages:
| Branch | Package |
|---|---|
| edge | 10.6_p2-r0 |
| 3.24 | 10.3_p1-r2 |
| 3.23 | 10.2_p1-r1 |
| 3.22 | 10.0_p1-r11 |
| 3.21 | 9.9_p2-r1 |
| 3.20 | 9.7_p1-r6 |
| 3.19 | 9.6_p1-r3 |
| 3.18 | 9.3_p2-r4 |
| 3.17 | 9.1_p1-r7 |
| 3.16 | 9.0_p1-r6 |
Point releases 3.21.10, 3.22.8, 3.23.8, and 3.24.4 carry them. 3.16 through 3.20 are out of regular support and still received the backport. New cloud images from those point releases onward ship the fix. Older images need it on every running instance.
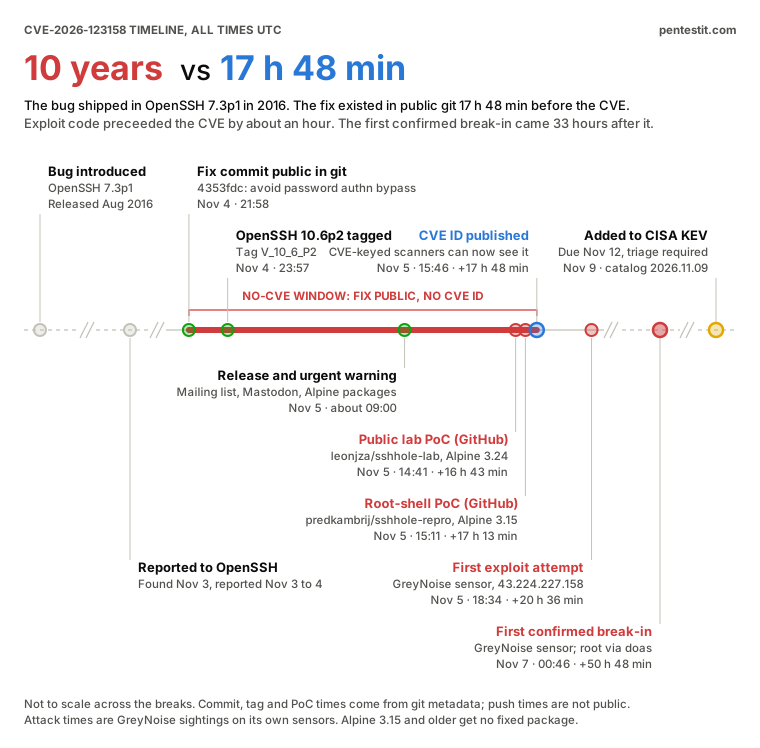
CVE-to-Patch Timeline: CVE-2026-123158
A patch existed for the CVE. However, what was missing was the CVE ID. This is an interesting CVE-to-Patch timeline for CVE-2026-123158:
Which government CERTs have issued alerts?
Seven national bodies had published something by 2026-11-09: France, Hong Kong, Hungary, Canada, the Netherlands, Japan and Belgium. CISA changed its SSVC rating to active exploitation and added the CVE to KEV on Nov 9, with a Nov 12 due date. Only Belgium’s CCB calls the bug actively exploited, and only JPCERT/CC lists all five conditions the way Alpine does.
| Agency (country) | Notice and date | Rating | What it says |
|---|---|---|---|
| JPCERT/CC (Japan) | CyberNewsFlash, 2026-11-09 | None stated | All five conditions, matching Alpine. Alpine-based commercial products are in use in Japan. Cites GreyNoise for attempts from Nov 5 and success on Nov 7; no confirmed compromise of a Japanese organization |
| CCB (Belgium) | Warning, about 2026-11-06 to 09 | Patch Immediately | Title: “Actively exploited CVE-2026-123158 (CVSS 8.1)”, musl libc without PAM |
| NCSC-NL (Netherlands) | NCSC-2026-0469, 2026-11-06 08:54 CET | Priority “Normal” | Correct scope and the 257 to 1024 byte window; Debian and Ubuntu out of scope. Advises not exposing SSH and disabling password logins |
| CERT-FR (France) | CERTFR-2026-ALE-015, alert, 2026-11-05 | Called “trivial to exploit” when conditions are met | musl without PAM, or PAM disabled. Login with two passwords, the second longer than 256 and shorter than 1024 characters. Workaround: disable password authentication, or SSH entirely |
| CERT-FR (France) | CERTFR-2026-AVI-1468, advisory, 2026-11-05 | Security policy bypass | One-line summary, points to the OpenSSH release notes |
| HKCERT (Hong Kong) | Security bulletin, 2026-11-06 | Medium | CVE-2026-123158, security restriction bypass, apply 10.6p2. Notes public proof of concept and that glibc distributions are unaffected |
| NKI (Hungary) | Vulnerability notice, 2026-11-05 16:46 | High, CVSS 8.1, priority “Elevated” | Restates the CVE record; links the commit, mailing list post and reproductions; cross-references ENISA EUVD-2026-117552 |
| Canadian Centre for Cyber Security | AV26-1130, “OpenBSD security advisory”, 2026-11-05 | None stated | Points to the OpenSSH release notes |
| CISA (United States) | Vulnrichment update in the CVE record, 2026-11-09 16:50 UTC | SSVC: Exploitation active, Automatable no, Technical Impact total | Adds a link to the KEV catalog for this CVE |
Frequently asked questions
What is CVE-2026-123158?
It is an OpenSSH password authentication bypass, nicknamed sshole, in sshd before 10.6p2 on Linux systems that use musl libc without PAM. A password of 257 to 1024 bytes logs into any account whose shadow field is *.
Is Alpine Linux affected?
Yes, Alpine 3.16 through 3.24 and edge with the default openssh-server package, password logins on, a * account and a $5$/$6$ hash present. Fixed revisions are listed above.
Are Debian, Ubuntu or RHEL affected?
No. They link OpenSSH against glibc and use PAM. Red Hat lists every product as not affected.
Are Docker containers affected?
Only containers that run sshd. An Alpine base image without sshd is not exposed.
What is the fastest mitigation?
Set PasswordAuthentication no, run sshd -t, restart sshd and confirm with sshd -T.
How do I know if I was attacked?
Search the auth log for Accepted password for an account whose shadow field is *. Any hit means the host is compromised until proven otherwise.
Is it being exploited?
Yes. GreyNoise confirmed successful attacks on its own vulnerable Alpine sensors from Nov 7, 2026, after attempts began on Nov 5. CISA added CVE-2026-123158 to the Known Exploited Vulnerabilities catalog on Nov 9 with a Nov 12 due date. No real organization had been reported compromised as of Nov 9.
https://pentestit.com/sshole-cve-2026-123158-openssh-musl-password-bypass/
Published: 2026 11 06 07:29:14
Received: 2026 11 20 07:48:30
Feed: PenTestIT
Source: PenTestIT
Category: News
Topic: Security Tooling
Views: 0
